Application security posture management (ASPM)
The Proof-Based ASPM Platform. All Your AppSec Tools. Zero Noise.
Invicti ASPM unifies DAST, SAST, SCA, IaC, Secrets, container testing, and more under one platform, and validates findings with runtime proof so only confirmed risks reach your team.
- AppSec leaders: see posture in a single view
- Developers: get automated remediation workflows
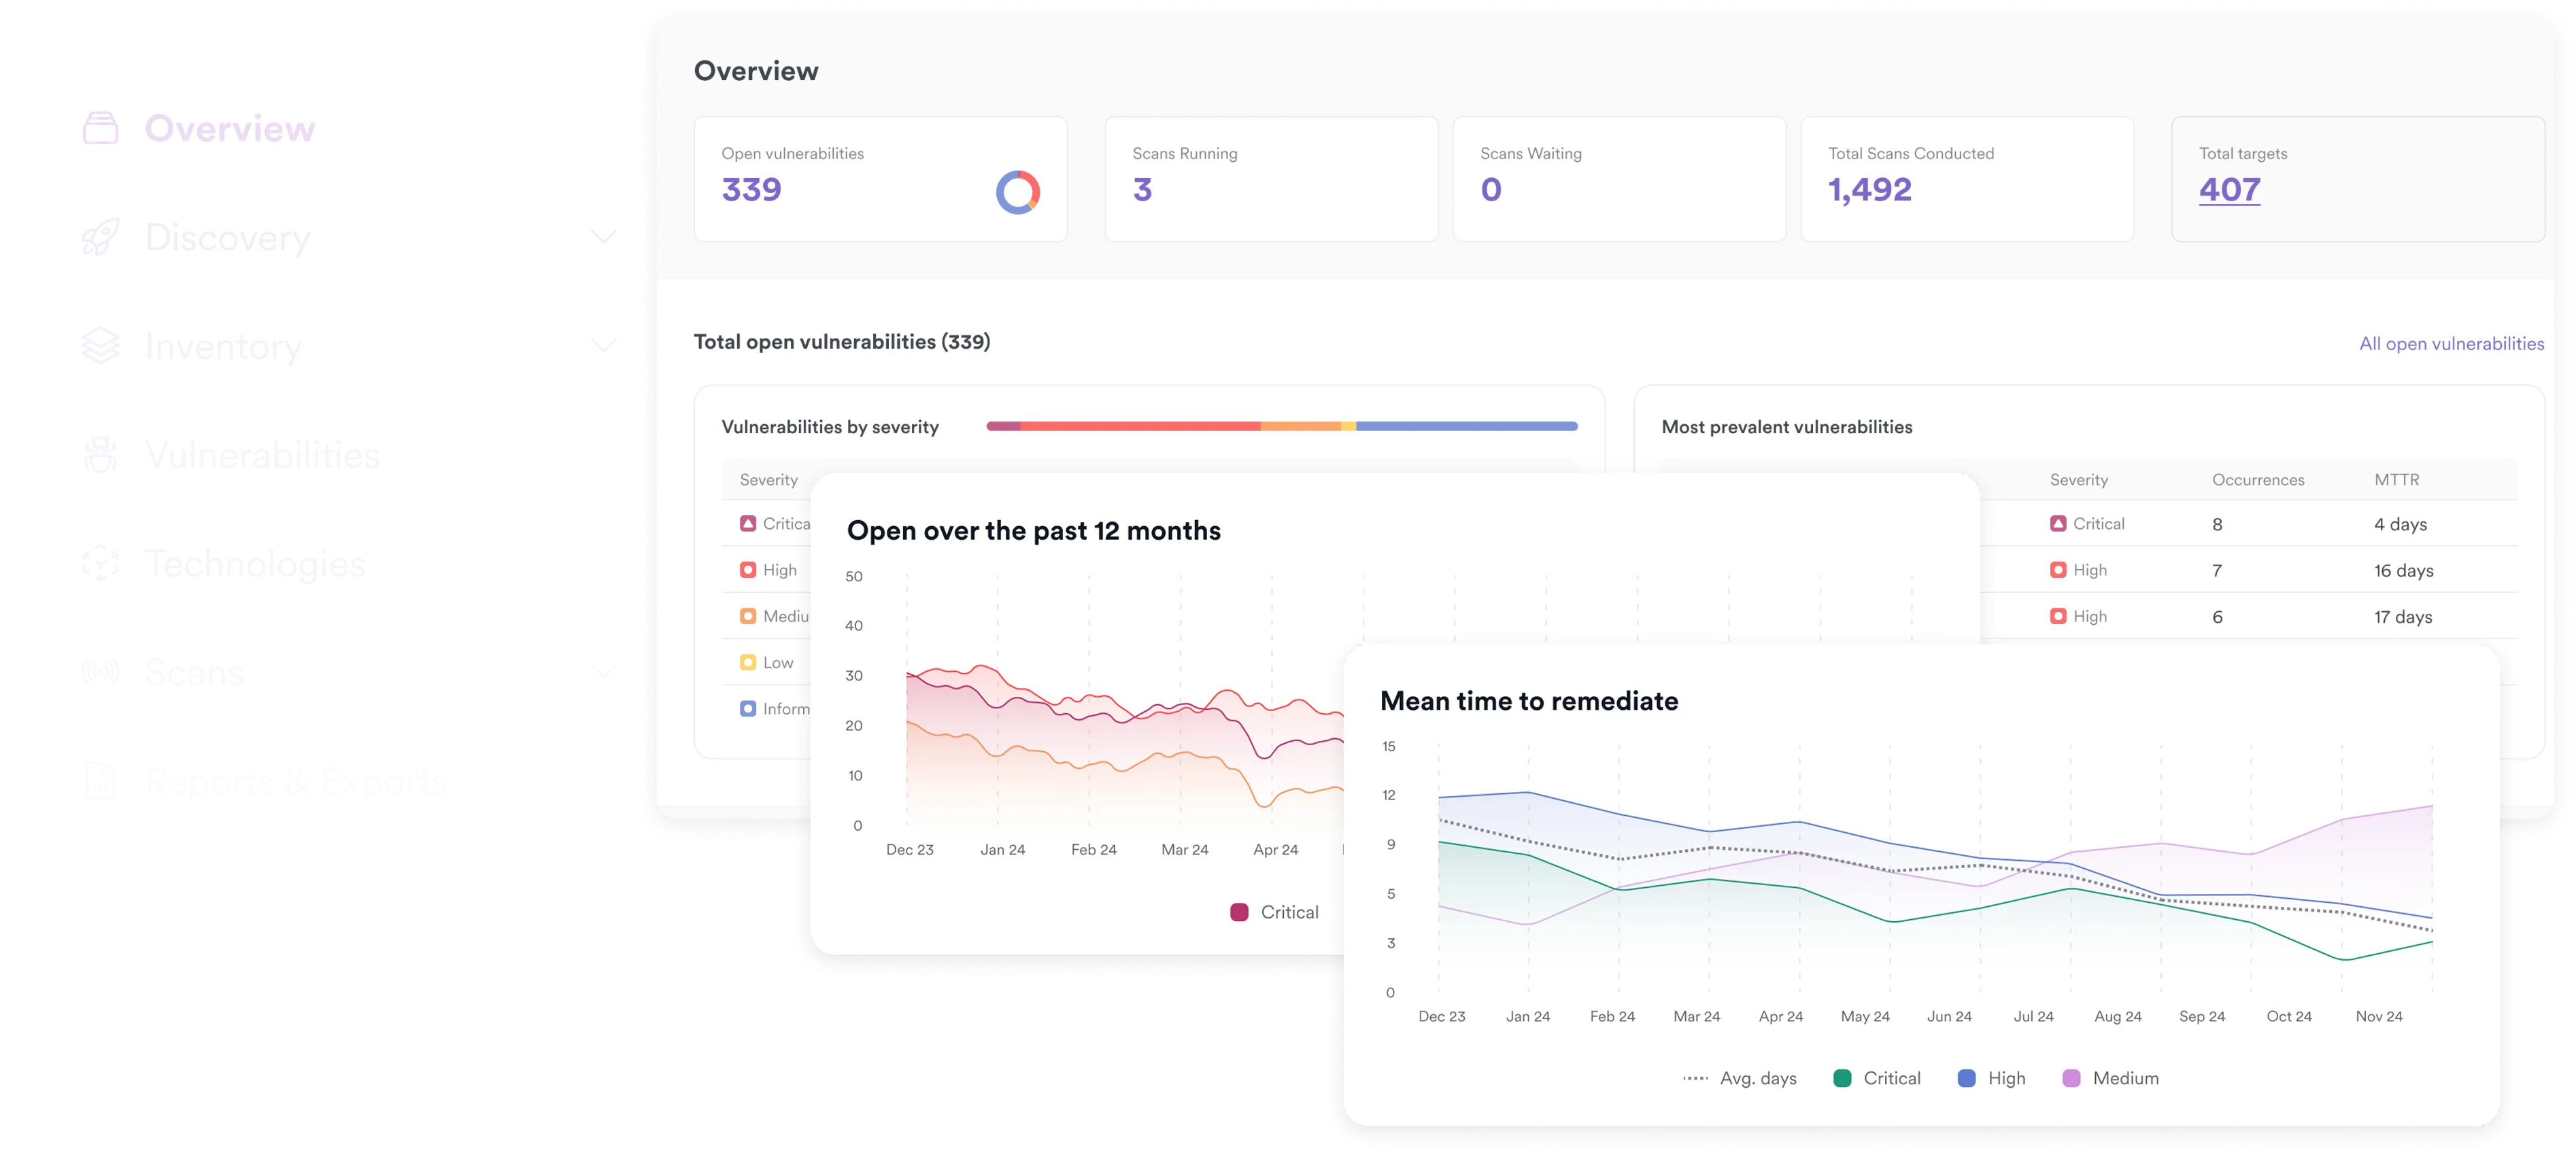
- Organizations: track MTTR and risk with clear KPIs
Get a demo
5000+ Top Organizations Trust Invicti




The Challenges of Application Vulnerability Management
Testing noise and fragmentation
Scanners flood teams with duplicate CVEs and siloed results. Without deduplication and normalization across AST tools, teams can’t see real risk.
Manual triage and remediation
Security teams waste hours manually assigning issues and chasing duplicates across disconnected pipelines. Weak automation, validation, and integration = slow remediation.
No clear KPIs or posture reporting
Most tools stop at reporting, leaving leaders in the dark on their actual security posture. Without remediation guidance and integrated training, vulnerabilities keep coming back.
Centralize and correlate
See all AppSec findings in one view
automate at scale
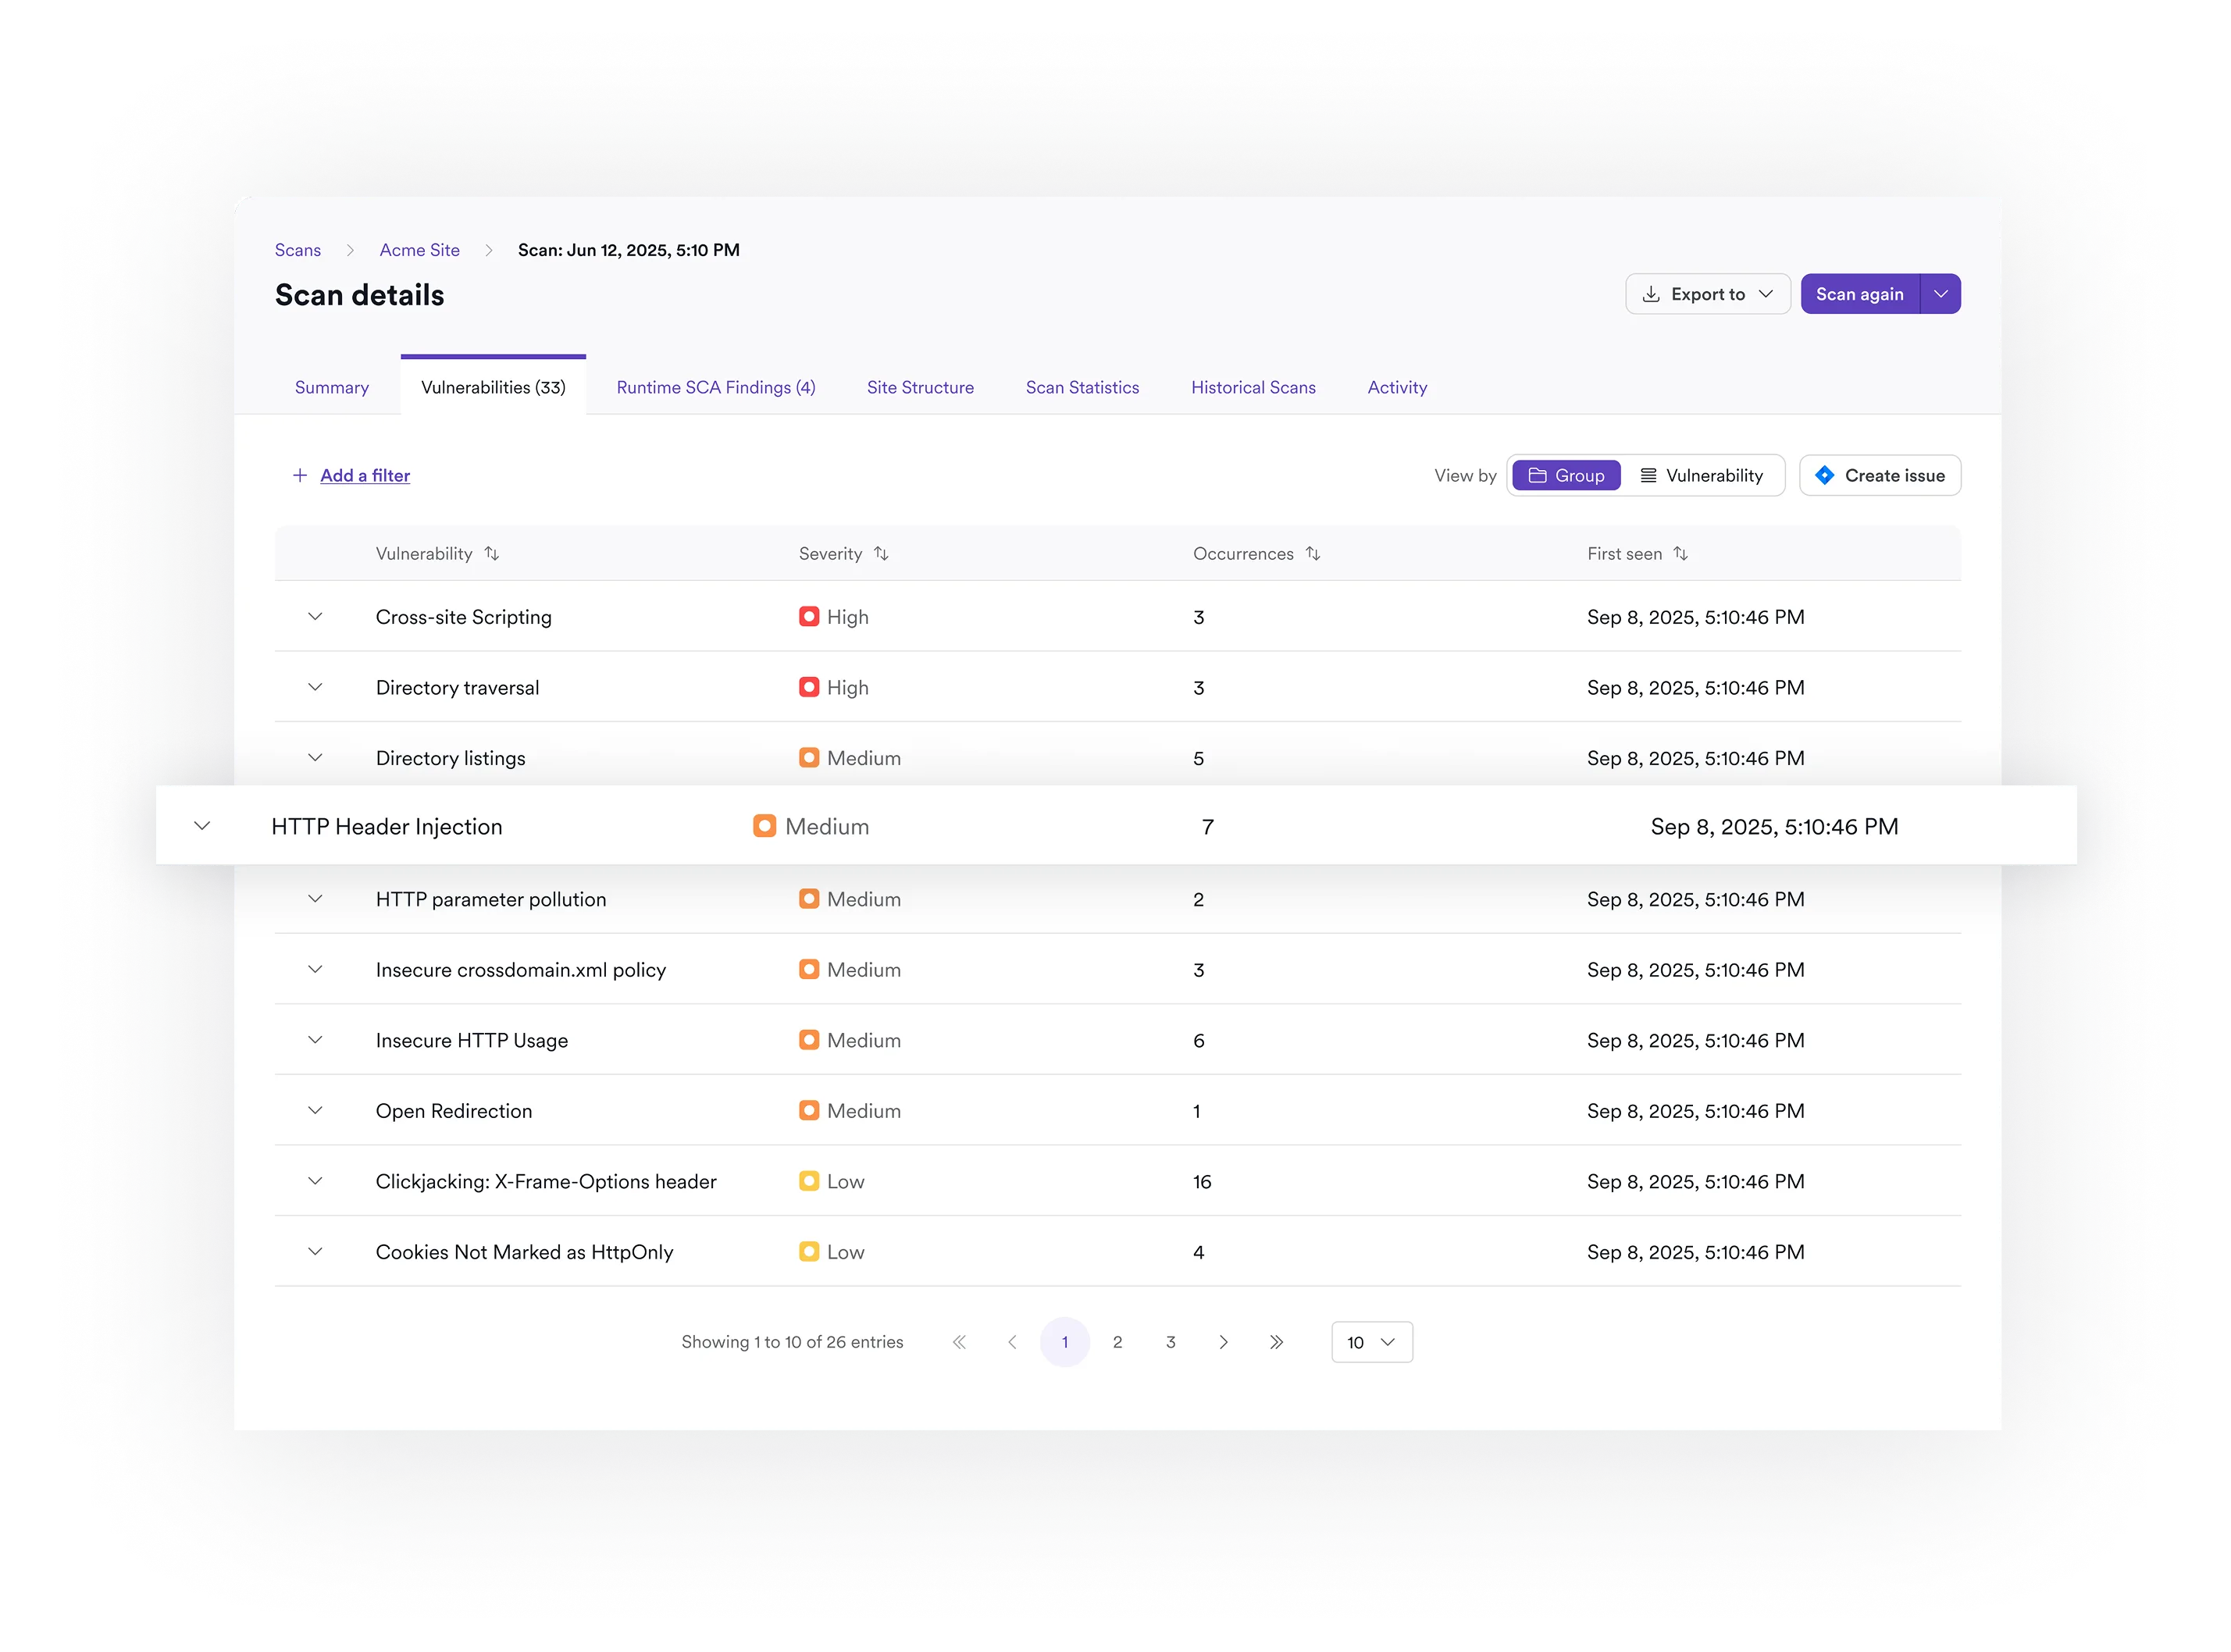
Triage and remediate faster

Support developers
Empower developers with guidance

Application Security Posture Management
One vulnerability management platform for every AppSec tool
See Invicti ASPM in action
110+ INTEGRATIONS
Integrated with the tools you already use




What customers say
“For more websites, we now don’t need to go externally for security testing. We can fire up Invicti, run the tests as often as we like, view the scan results, and mitigate to our hearts’ content. As a result, the budget we were spending every year on penetration testing decreased by approximately 60% almost immediately and went down even more the following year, to about 20% of our initial spending.”
—Brian Brackenborough | CISO, Channel 4
“Invicti detected web vulnerabilities that other solutions did not. It is easy to use and set up...”
—Henk-Jan Angerman | Founder, SECWATCH

“I had the opportunity to compare expertise reports with Invicti ones. Invicti was better, finding more breaches.”
—Andy Gambles | Senior Analyst, OECD

“Invicti is the best web application security scanner in terms of price-benefit balance. It is a very stable software, faster than the previous tool we were using and it is relatively free of false positives, which is exactly what we were looking for.”
—Harald Nandke | Principal Consultant, Unify (now Mitel)
Application Security Posture Management Questions
What is application security posture management (ASPM)?
ASPM centralizes findings from all your application security tools (DAST, SAST, SCA, IaC, Secrets, and container testing), deduplicates and prioritizes them, and tracks remediation and risk over time. Invicti ASPM adds runtime proof, so teams act on vulnerabilities that are confirmed exploitable.
Is ASPM the same as a vulnerability management platform or CNAPP?
ASPM is vulnerability management focused on applications: it manages findings and risk from code to runtime. CNAPP secures cloud infrastructure. Invicti ASPM is purpose-built for application security and can sit alongside a CNAPP.
How is Invicti ASPM different from other ASPM tools?
Most ASPM tools aggregate findings from other scanners. Invicti is built DAST-first: its own proof-based scanning validates findings at runtime, so the posture data you prioritize and report on is confirmed, not guessed.
Gain clarity, remediate faster, measure progress
Single-pane visibility, automatic remediation, measurable results.