Discover + test
Secure the apps behind public services
Scan running web apps and APIs with runtime testing.
Discover API endpoints through scans, gateways, and source code.
Test authenticated workflows and API authorization.
Secure the applications and APIs behind essential public services. Validate real risk, prioritize remediation, and support federal security requirements with actionable evidence.

Know where application risk exists.

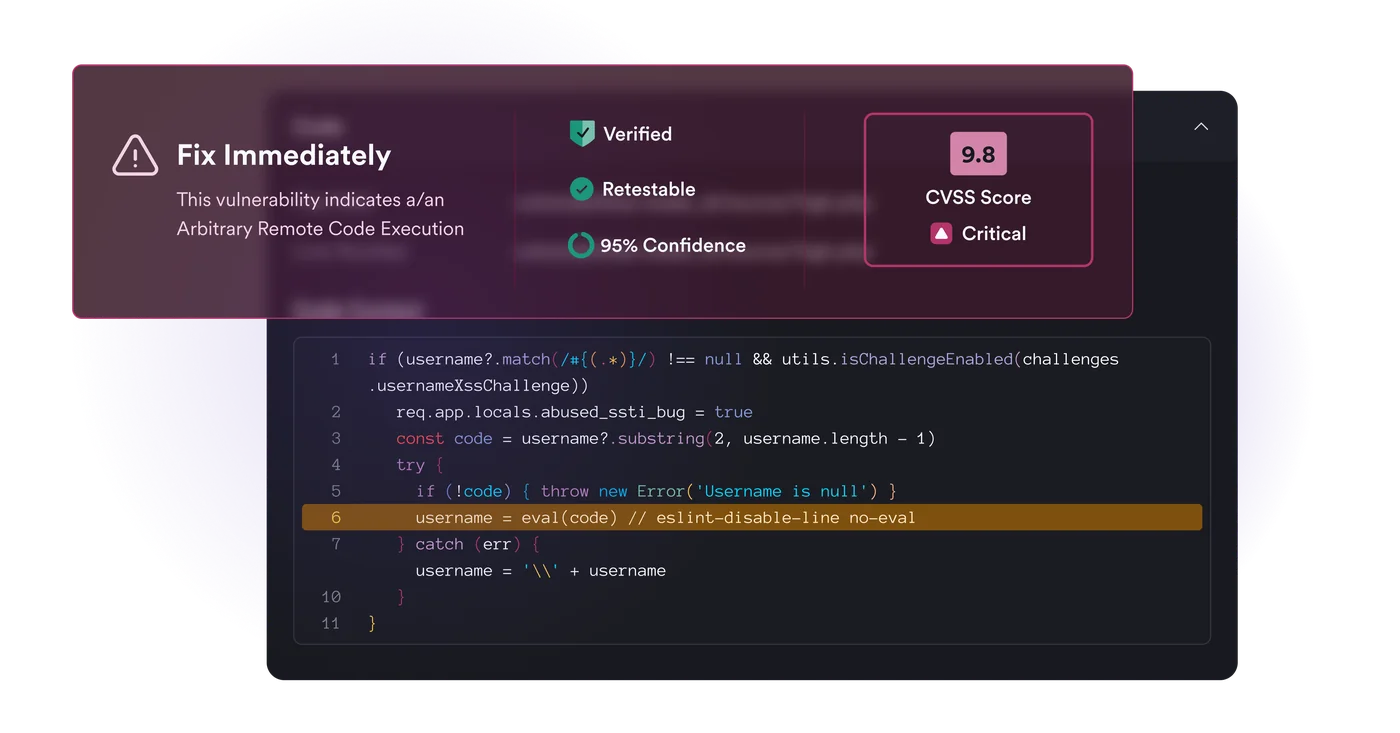
Focus on proven, high-impact threats.

Track and demonstrate risk reduction.
Test applications and APIs, validate real risk, and document remediation across agency programs.
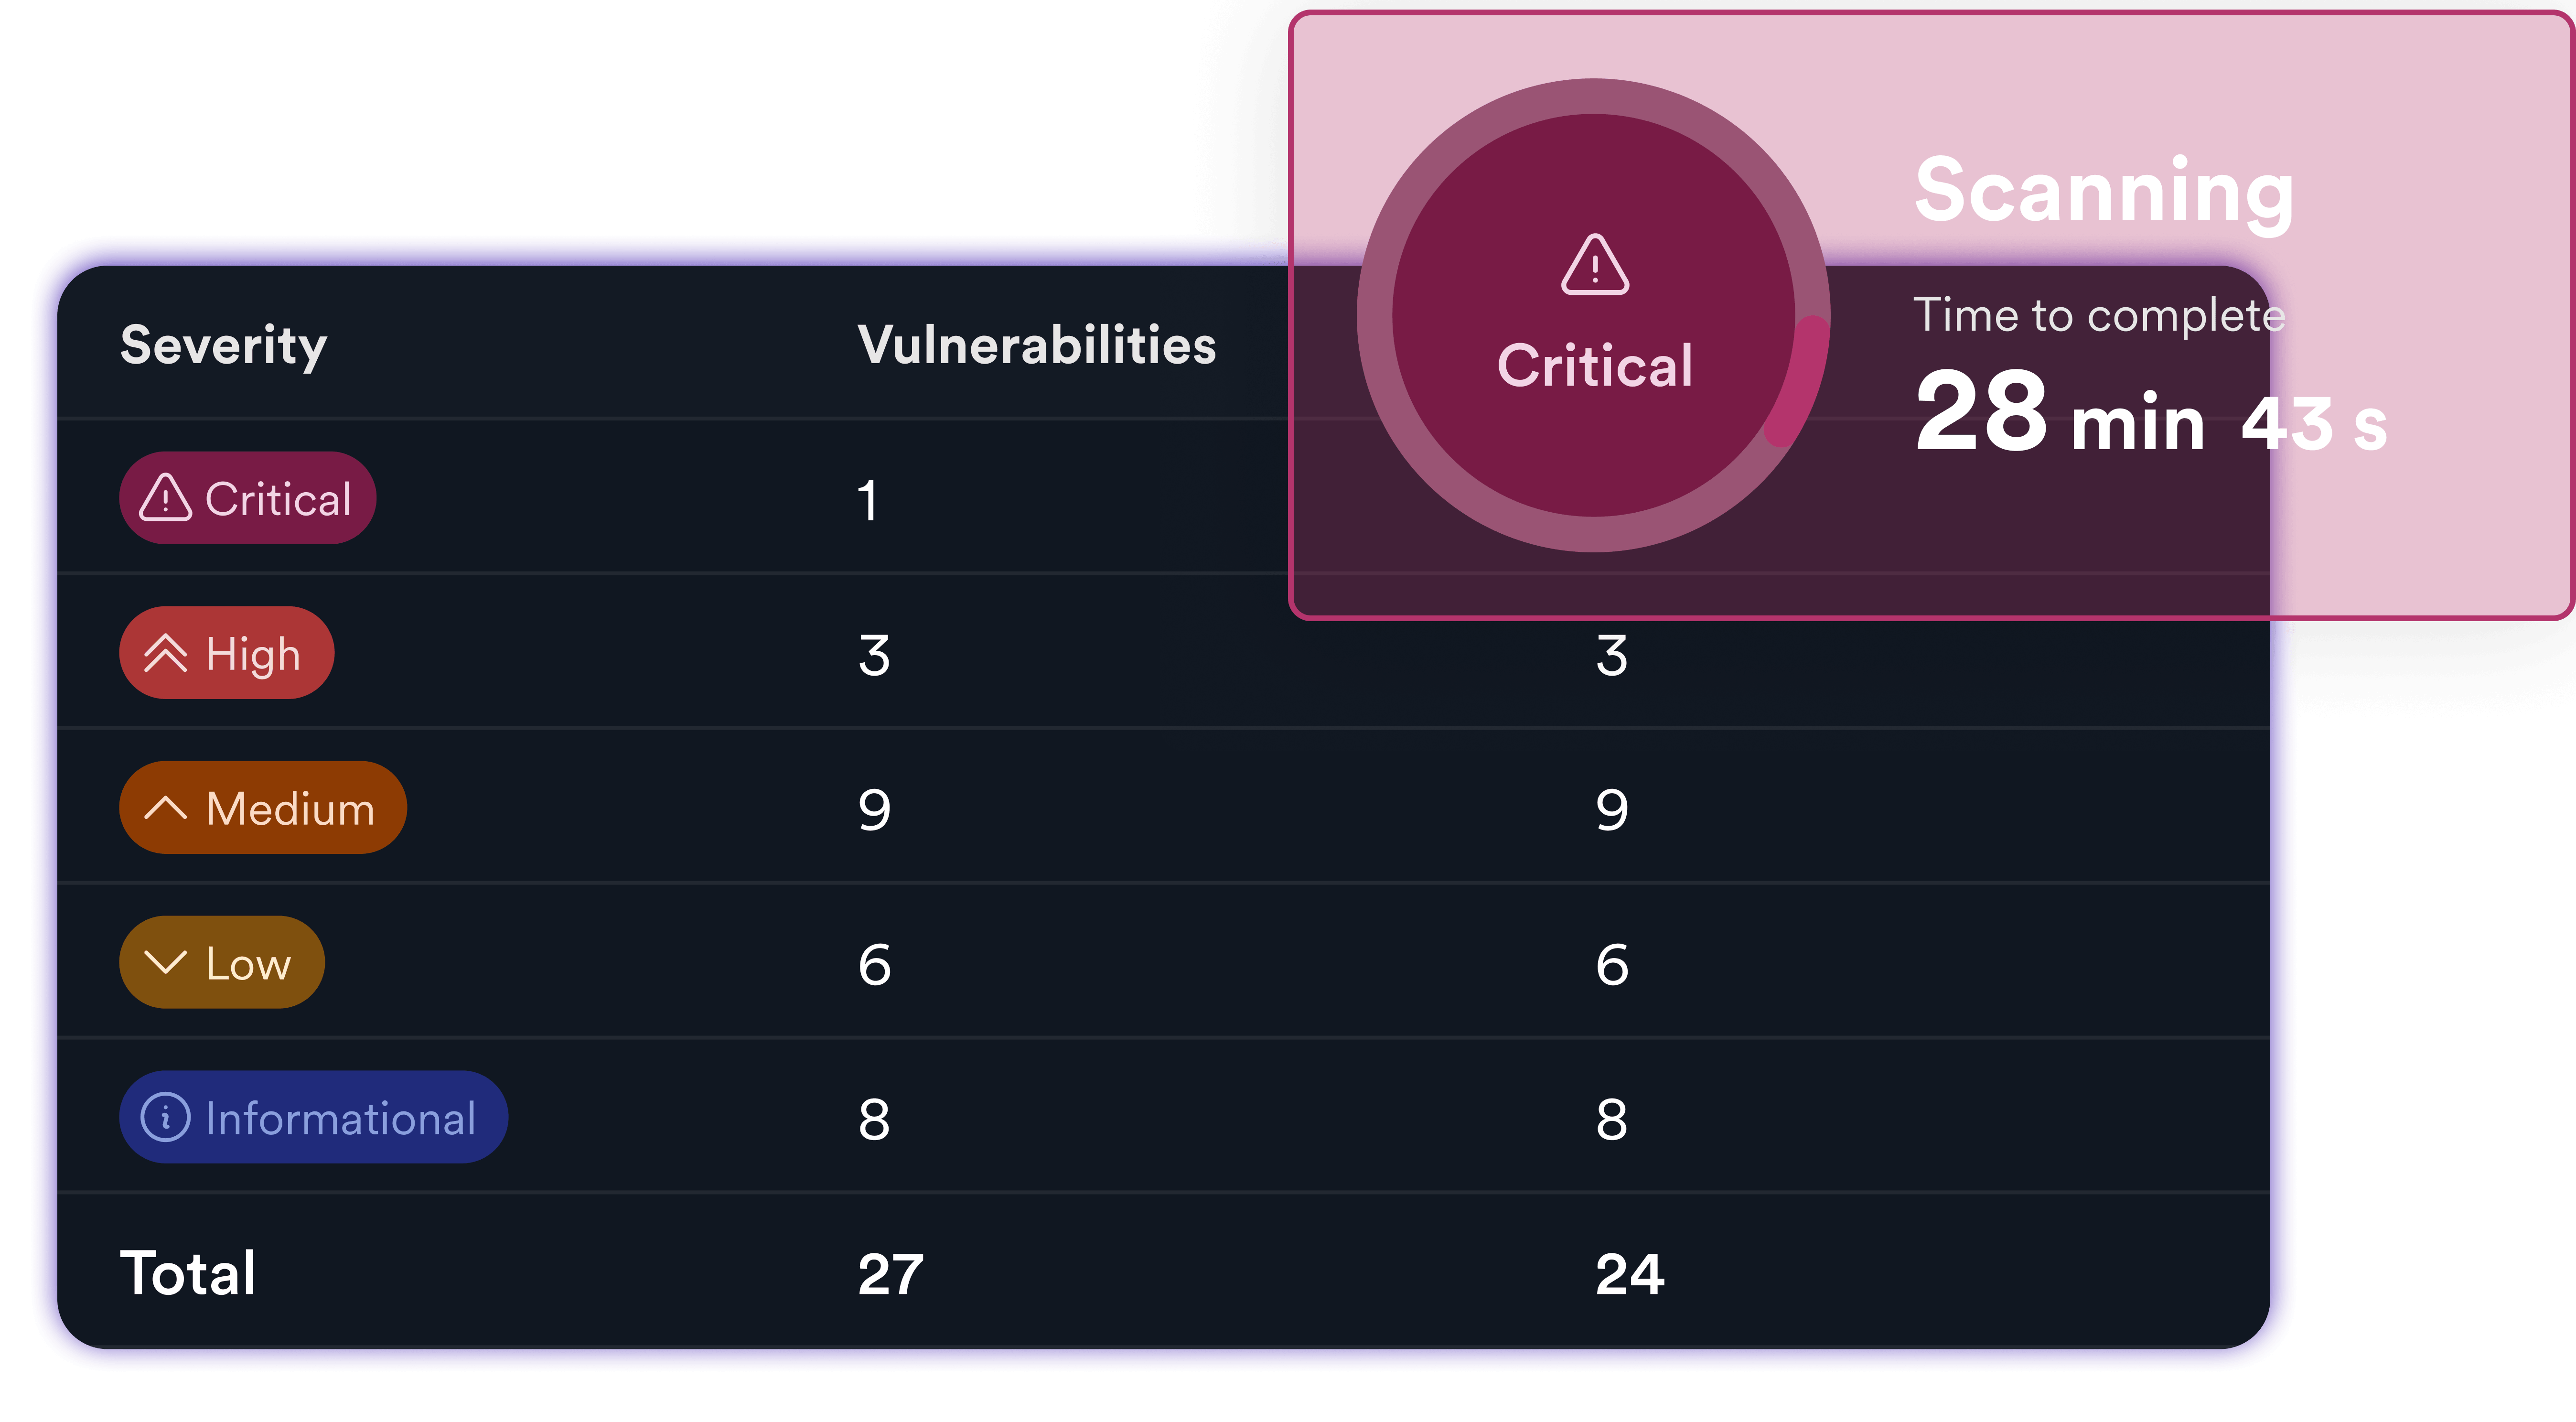


Find exploitable weaknesses in citizen portals, public websites, and agency applications.

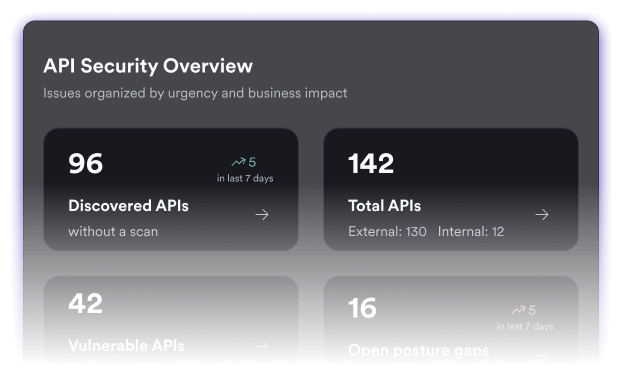
Discover exposed and undocumented APIs, then test authorization and complex API workflows.

Use proof-based scanning to cut manual validation for supported vulnerability types.

Use adaptive, code-informed testing to examine application-specific attack paths.

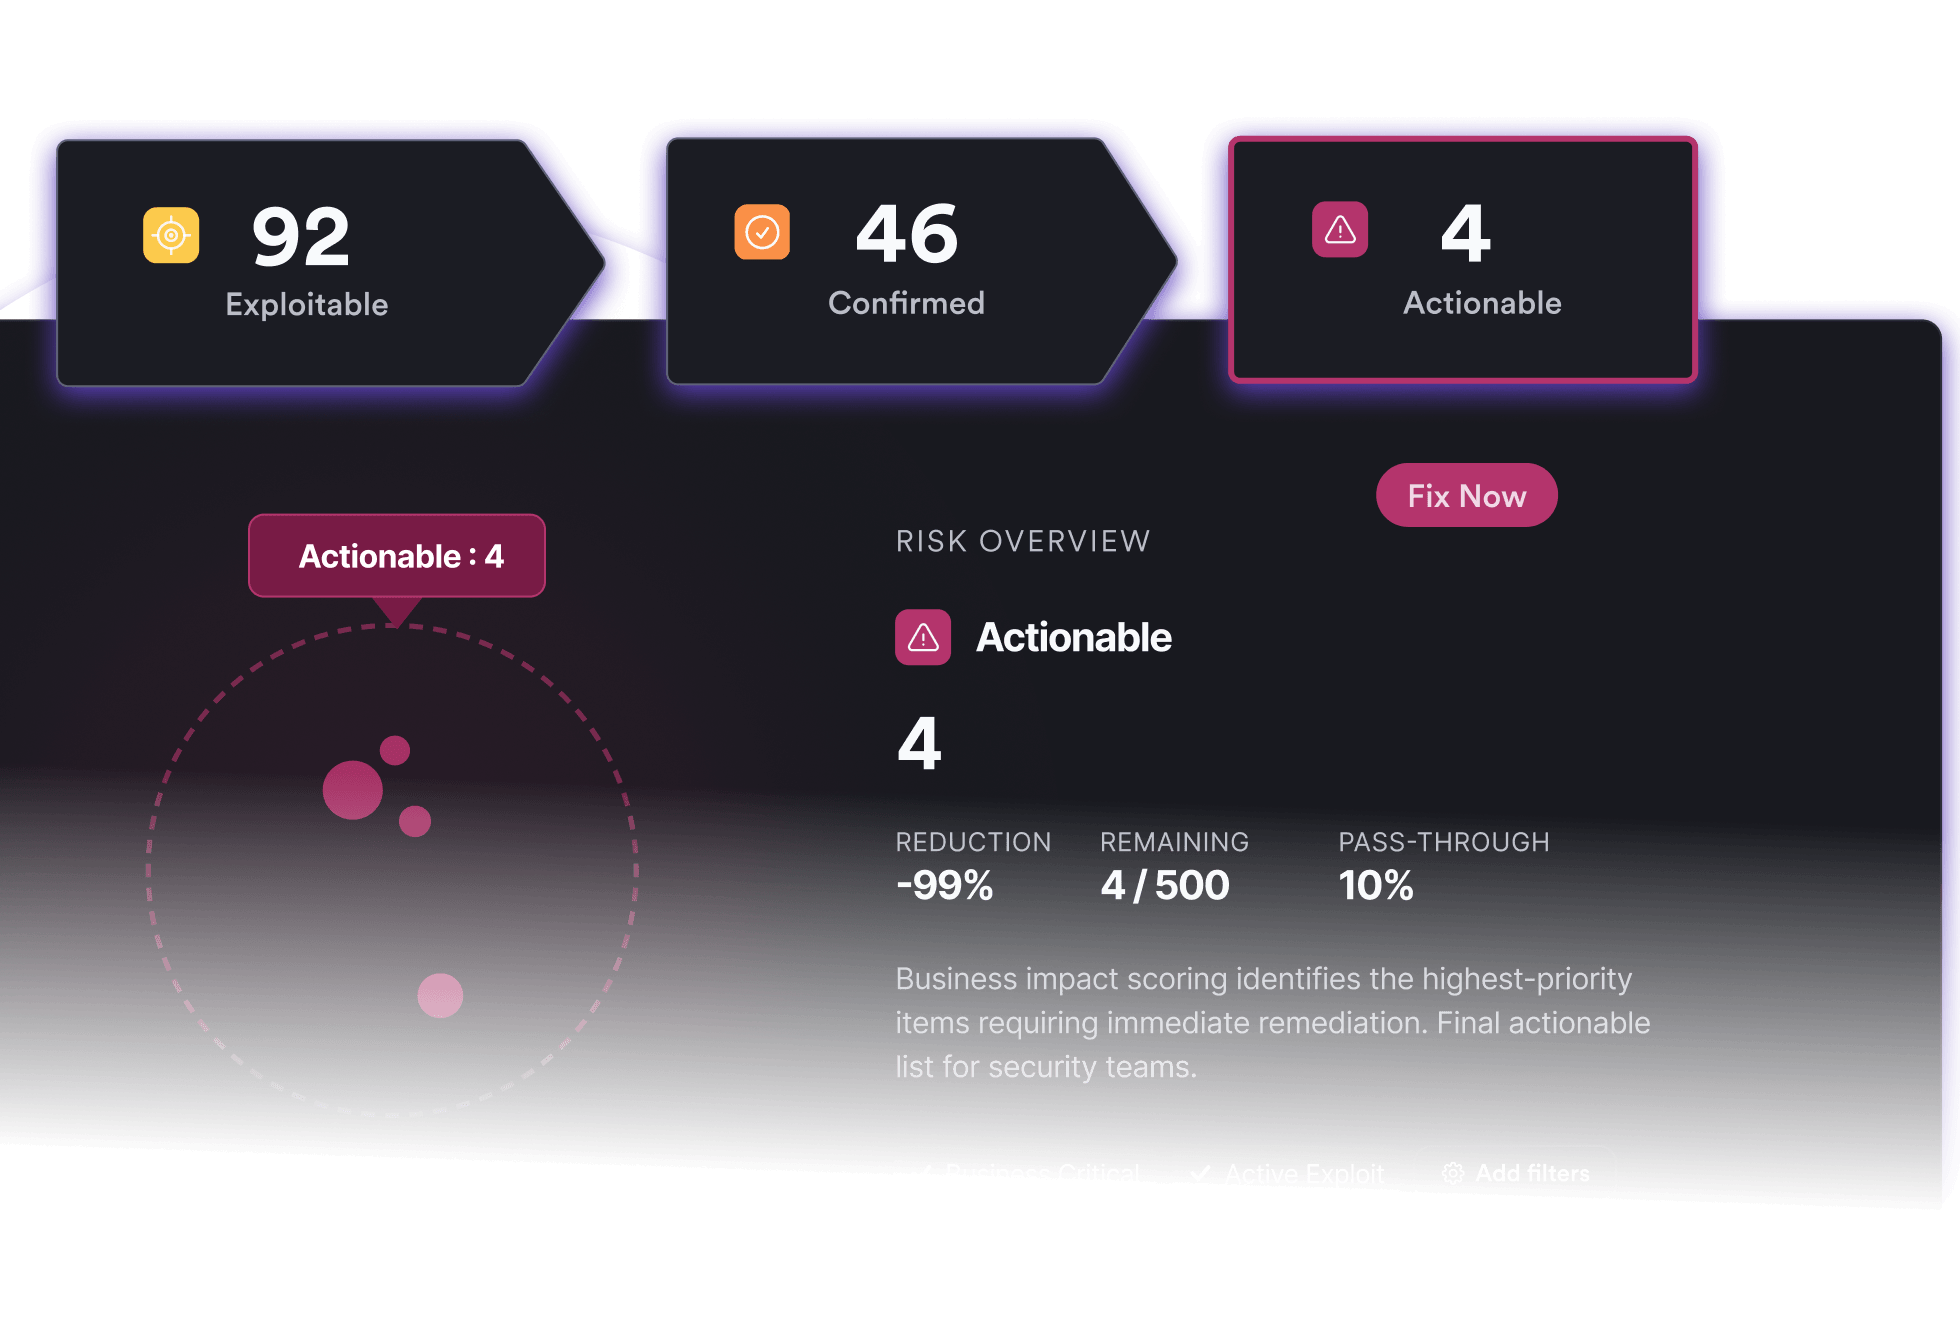
Correlate findings and apply runtime evidence to prioritize remediation across programs.

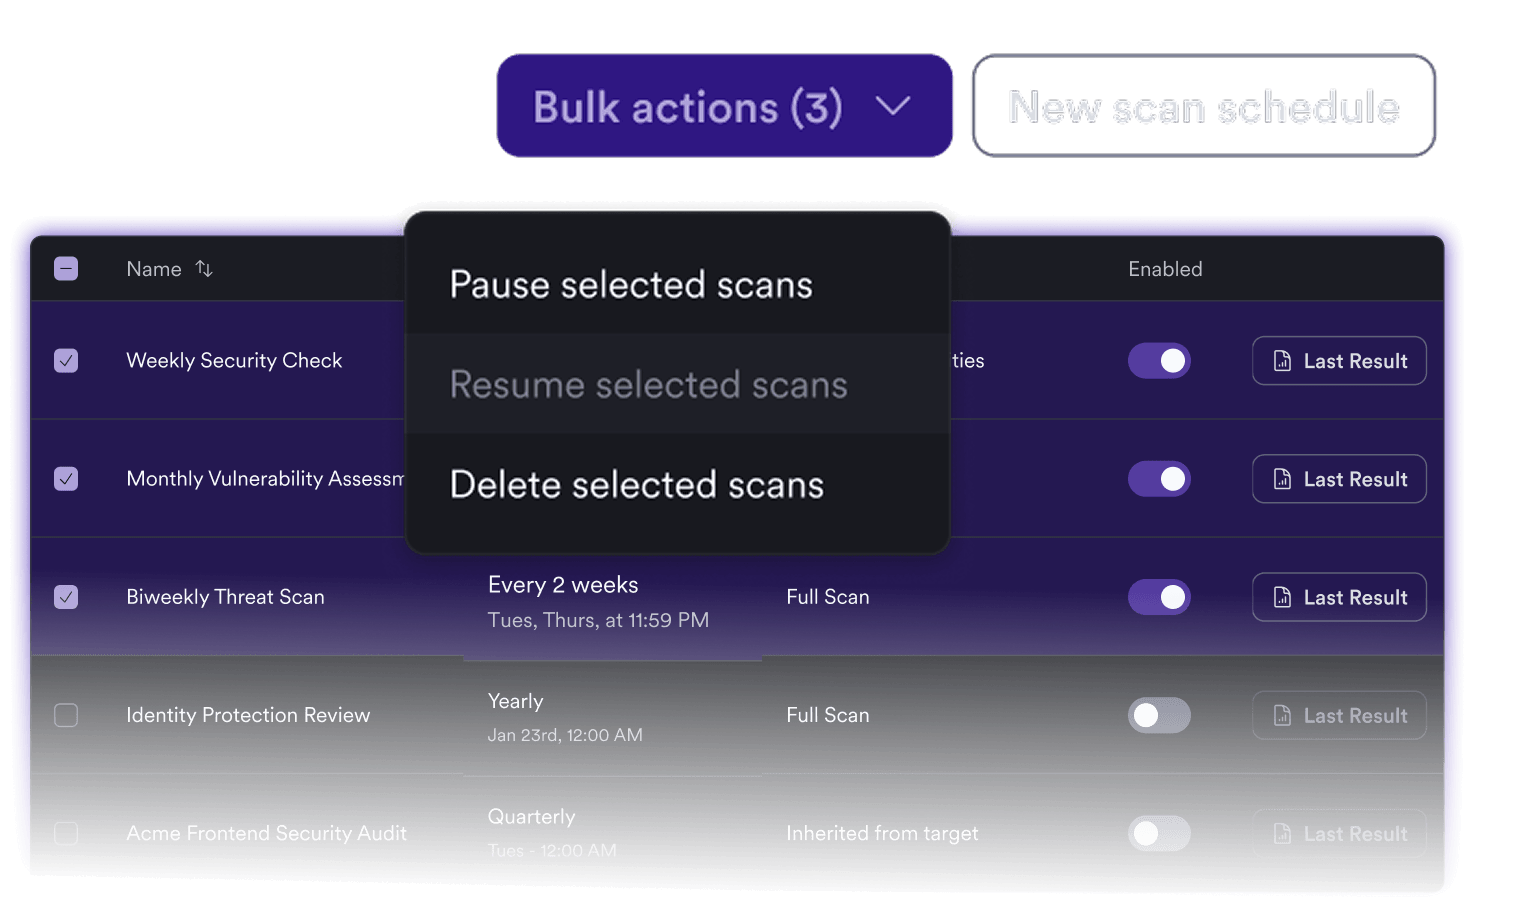
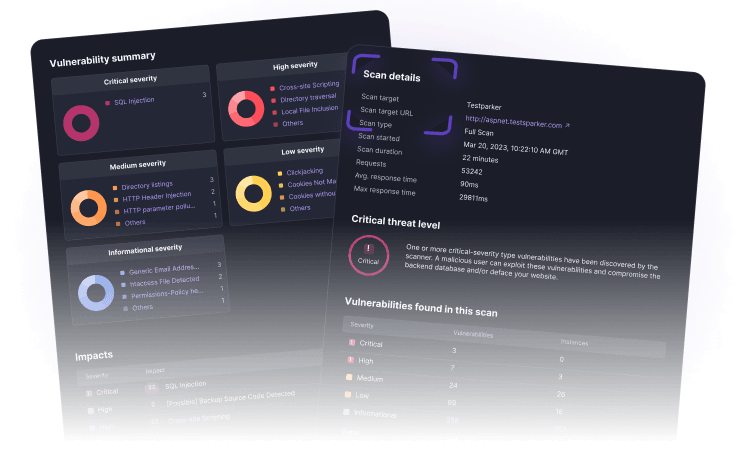
Track security assessments, fix status, and trends to support oversight and audits.




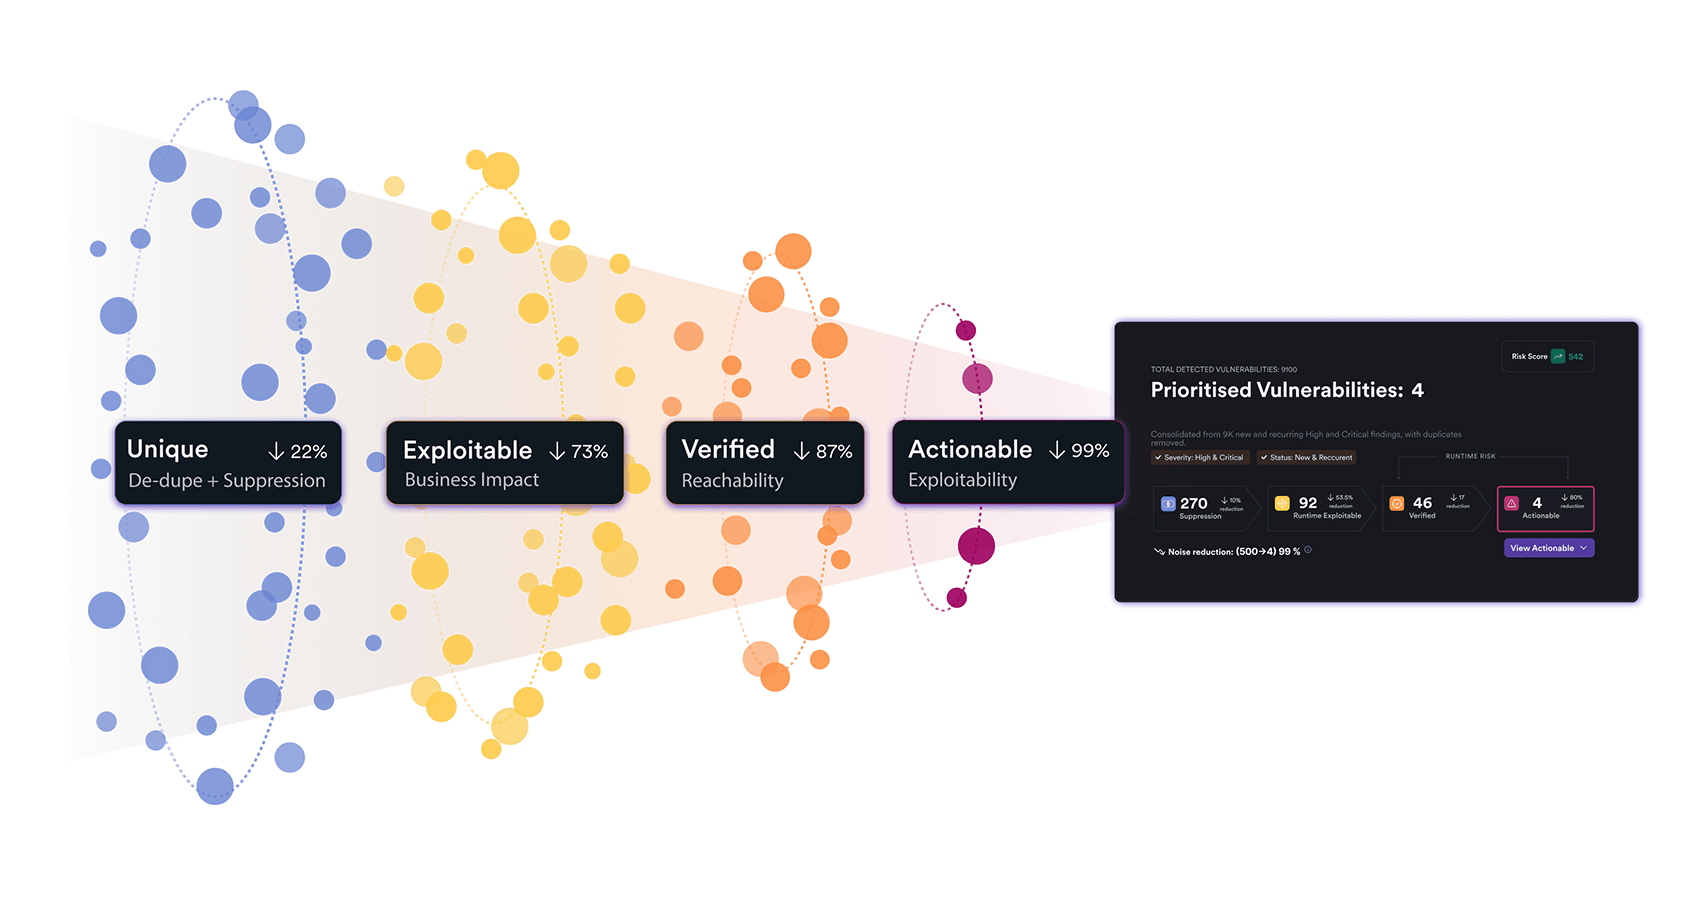
Accurate findings and faster fixes, backed by independent benchmark results.
Confirmed by Miercom as the industry’s most accurate DAST. Scan running web applications and APIs, validate findings with proof-based scanning, and focus developers on the vulnerabilities that pose real business risk.
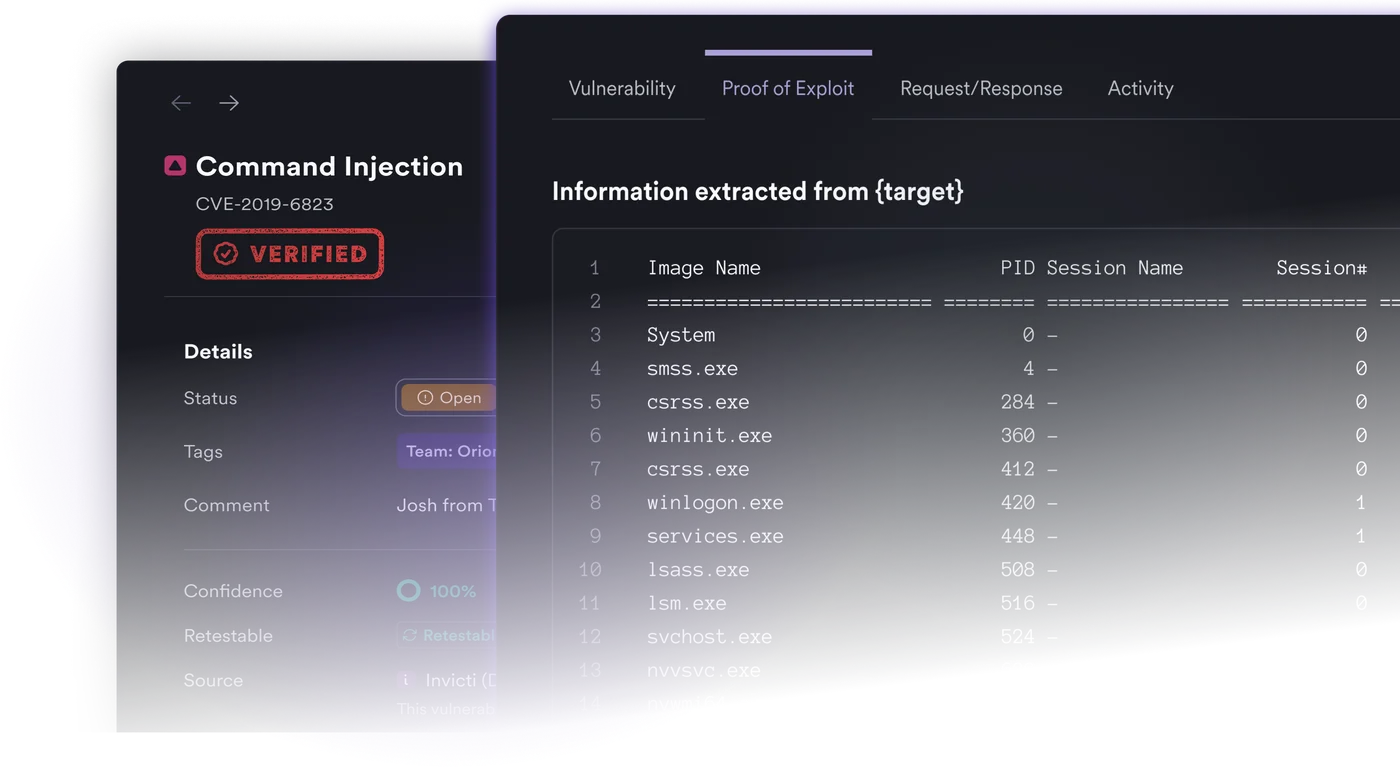
Invicti SAST moves beyond theoretical findings by connecting static analysis to verified runtime vulnerabilities, code ownership, and remediation guidance.
Discover vulnerable dependencies, generate SBOMs, identify container risks, and prioritize remediation with runtime intelligence.
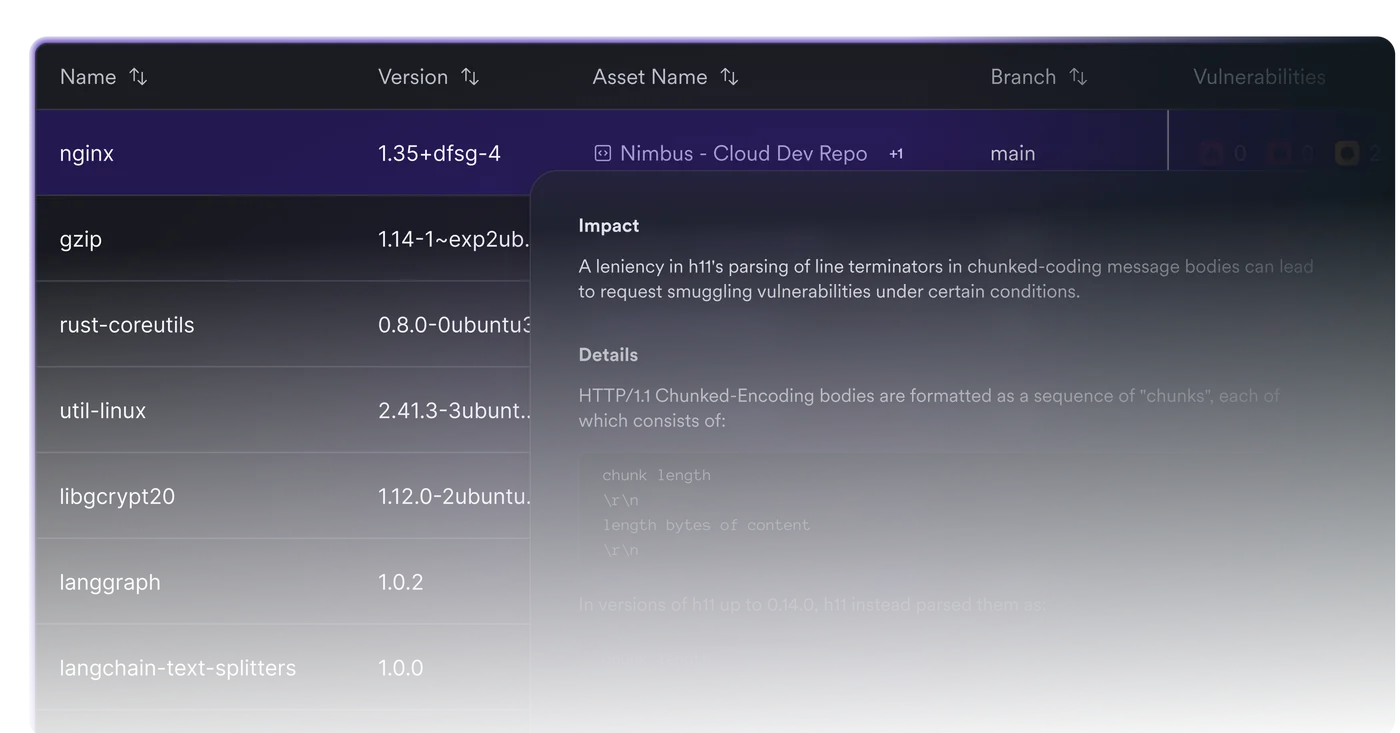
Detect misconfigurations early, enforce security policies in CI/CD, and track IaC risk alongside code and runtime findings.
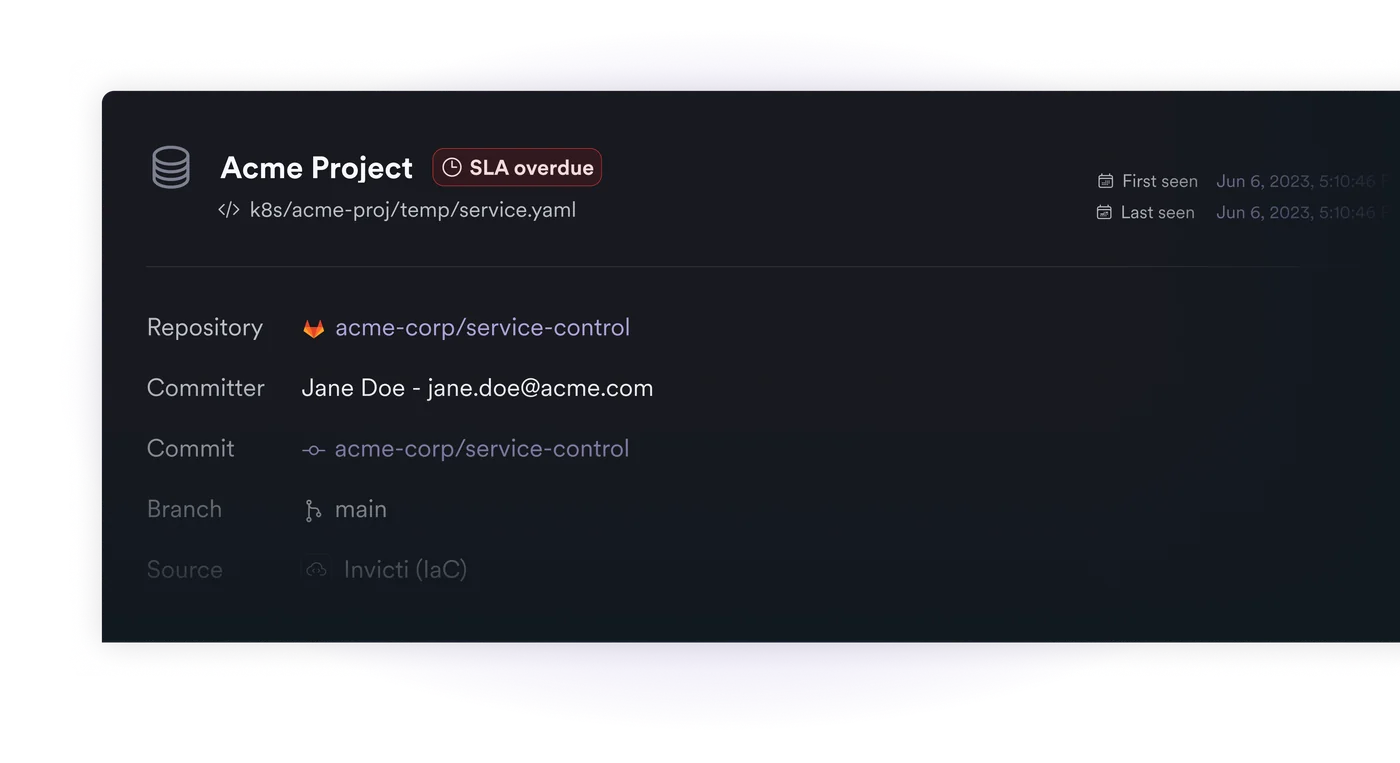
Invicti finds and surfaces exposed API keys, passwords, encryption keys, and tokens before hackers get the chance to exploit them.
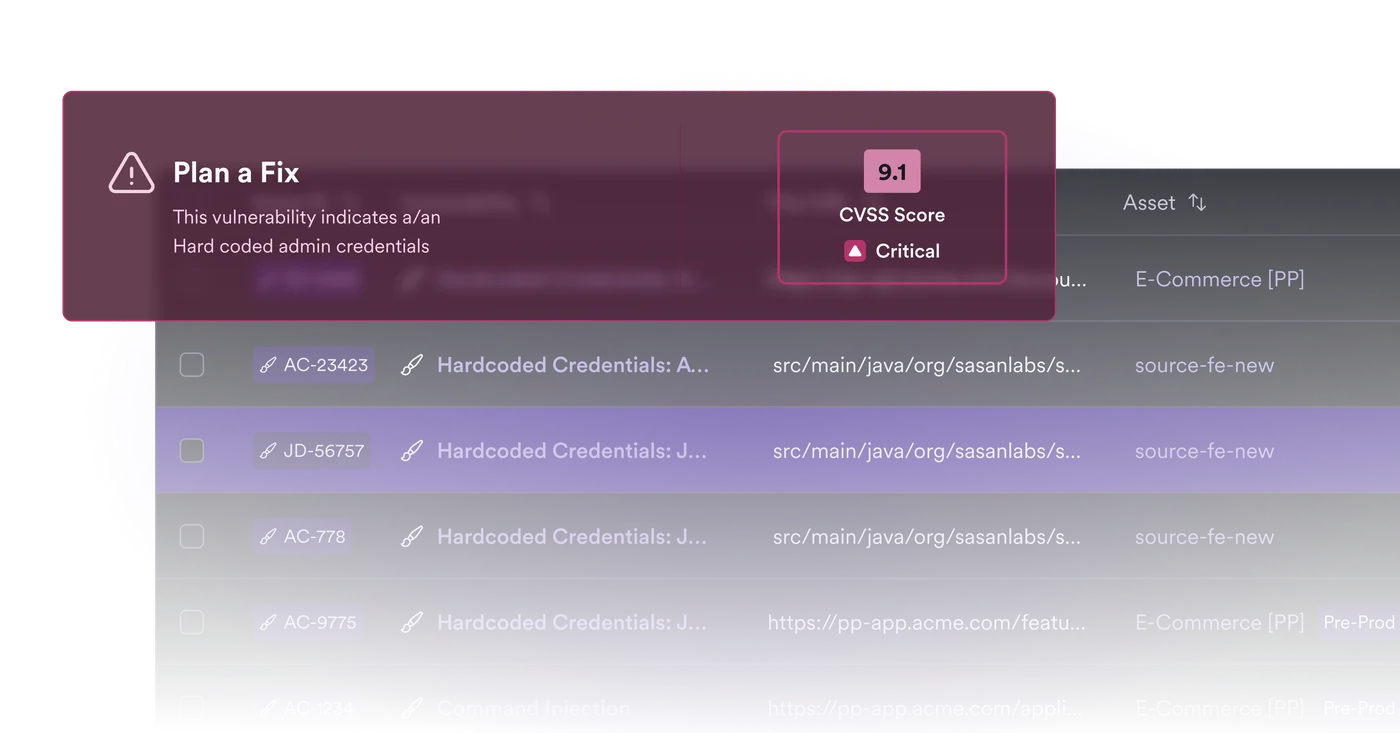
Invicti integrates container scanning with SCA, DAST, and CI/CD workflows so you can track vulnerabilities across registries and clusters, cut through complexity, and prioritize container risk in one unified view.
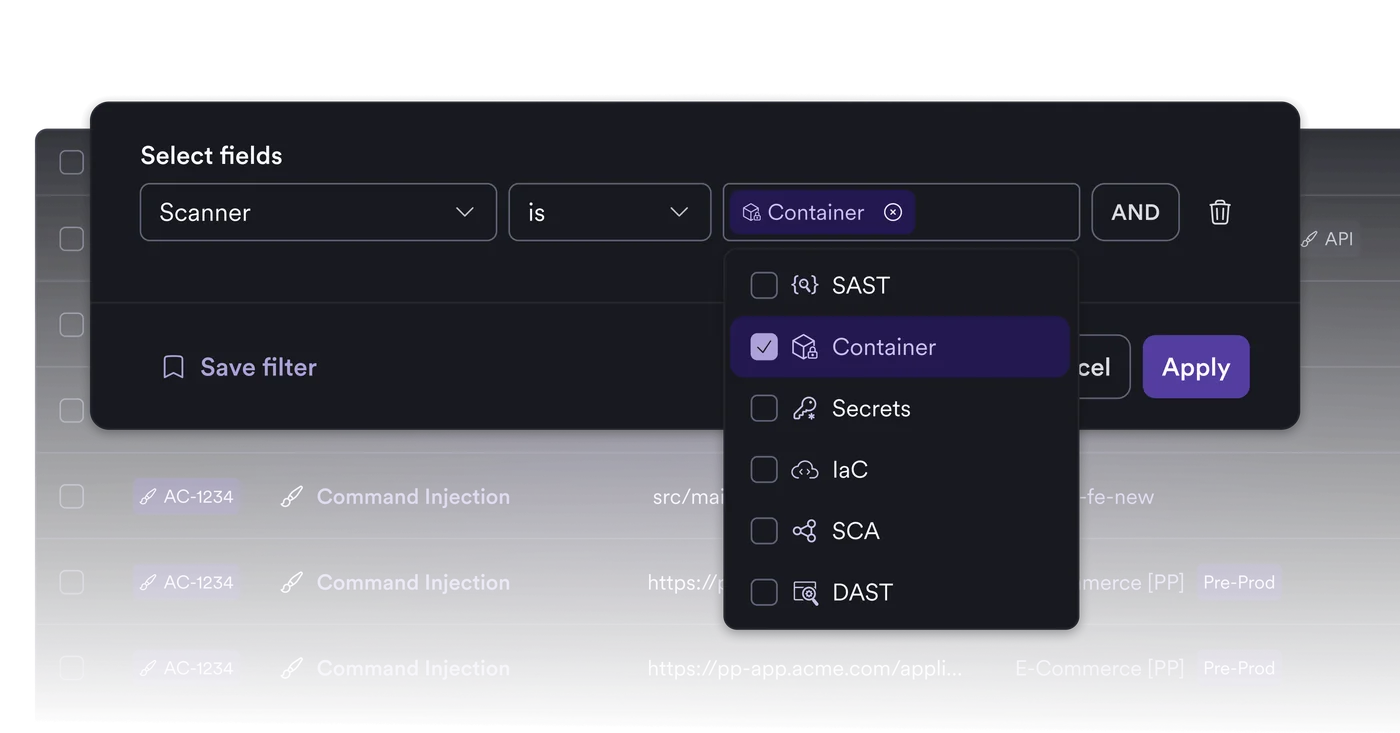
Confirmed by Miercom as the industry’s most accurate DAST. Scan running web applications and APIs, validate findings with proof-based scanning, and focus developers on the vulnerabilities that pose real business risk.
Invicti SAST moves beyond theoretical findings by connecting static analysis to verified runtime vulnerabilities, code ownership, and remediation guidance.
Discover vulnerable dependencies, generate SBOMs, identify container risks, and prioritize remediation with runtime intelligence.
Detect misconfigurations early, enforce security policies in CI/CD, and track IaC risk alongside code and runtime findings.
Invicti finds and surfaces exposed API keys, passwords, encryption keys, and tokens before hackers get the chance to exploit them.
Invicti integrates container scanning with SCA, DAST, and CI/CD workflows so you can track vulnerabilities across registries and clusters, cut through complexity, and prioritize container risk in one unified view.

A lot of security checks, that are easily customizable. You can make the exact scan profile/type that you want. Really good support that answering fast and giving you proper recommendations. Every time when we reported false positives - the reaction was fast and adequate. It is the best solution that you can find on a market.
The user interface is great, making everything straightforward. The scanning engine stands out for producing high-quality results, especially when compared to competitors. It significantly reduces the manual effort and time needed to perform actions manually. I also found the initial setup to be very easy.
The most valuable aspect of Invicti is its ability to bridge the gap between active vulnerability scanning and dependency management. While many tools focus only on active threats, Invicti provides the SCA depth we need for enterprise portfolios.
“We can fire up Invicti, run the tests as often as we like, and mitigate to our hearts’ content. The budget we were spending every year on penetration testing decreased by approximately 60% almost immediately …

“As opposed to other web application scanners we used, Invicti is very easy to use and does not require a lot of configuring. An out of the…

“Start integrating Invicti into your process and you’ll be surprised at how much time it saves you and how much ‘auto magic’ it brings to your entire development pipeline …