
Pentesters
Machine-speed recon before manual engagement
Octo AI co-tester for complex authenticated flows
Auto-generated branded reports cut write-up time by 70%
Learn more
Deliver continuous application security as a managed service. Invicti gives MSSPs, pentesters, and AppSec providers the automation and infrastructure to scale.




Every client with a web presence faces application threats. DAST and API security are no longer optional — they're a board-level concern.
Annual engagements leave clients exposed 364 days a year. Recurring, automated scanning turns a project into a predictable monthly retainer.
PCI DSS v4.0, NIS2, DORA, and ISO 27001 all require demonstrable application security testing — creating urgency your sales team can leverage.
Six repeatable services built on Invicti’s Platform
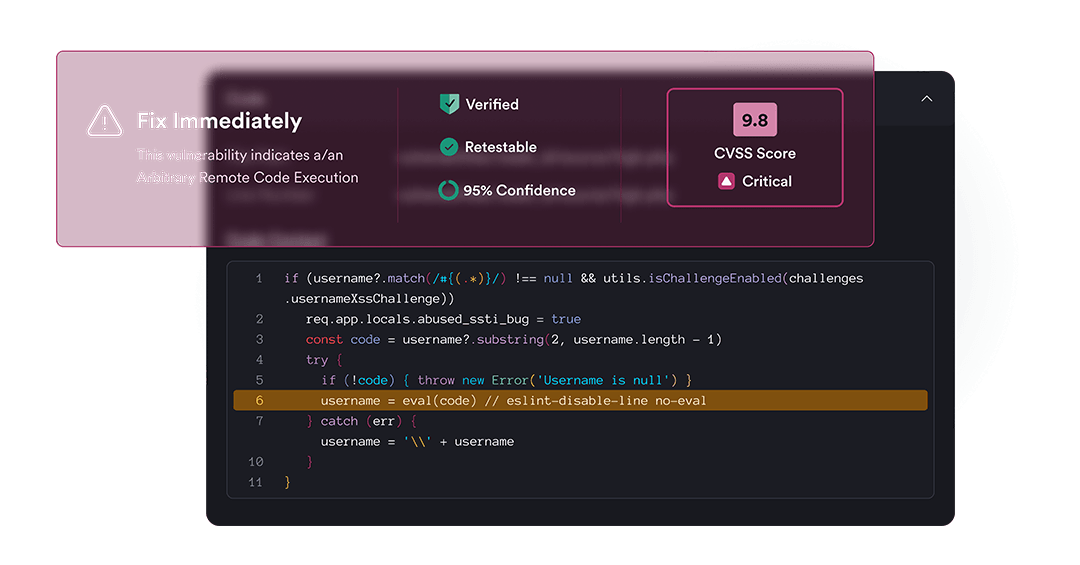
Invicti SAST moves beyond theoretical findings by connecting static analysis to verified runtime vulnerabilities, code ownership, and remediation guidance.
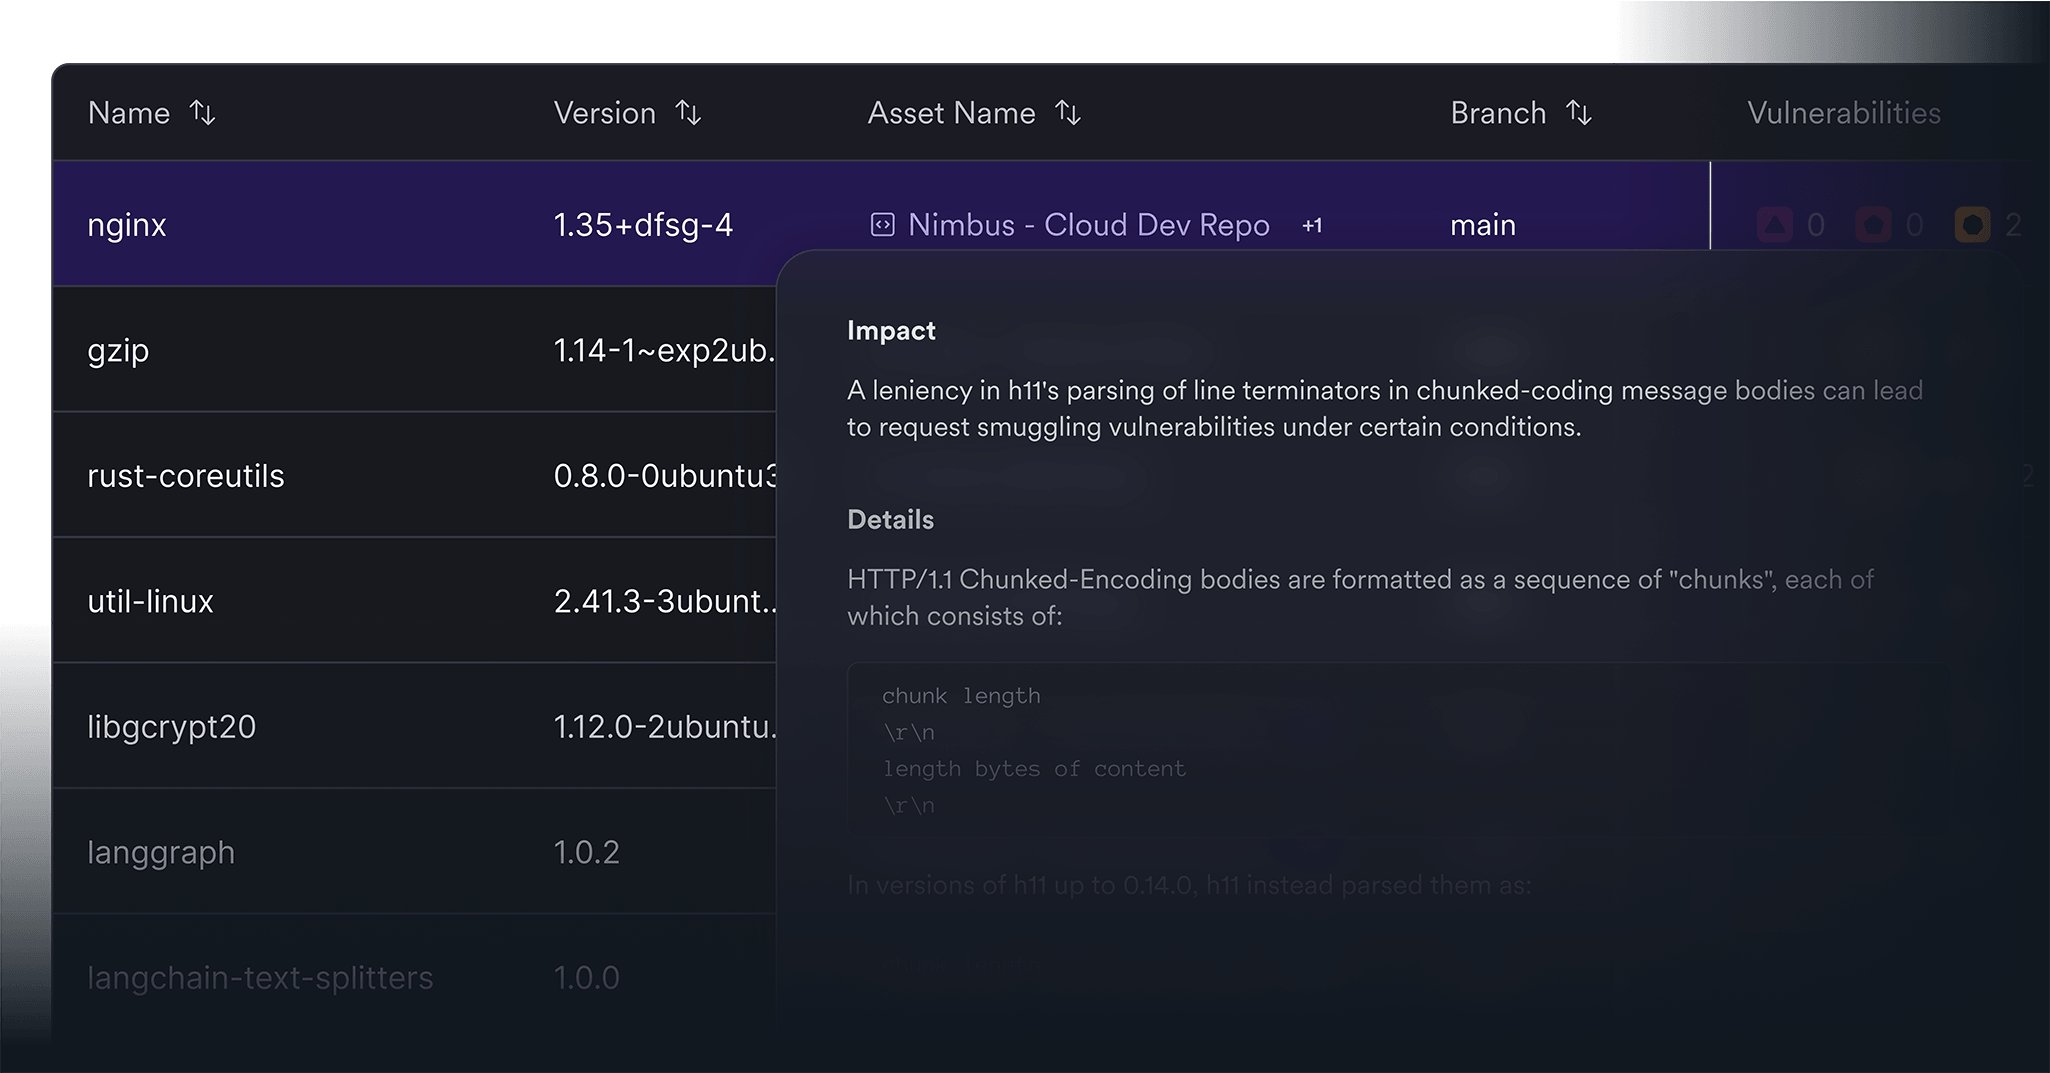
Discover vulnerable dependencies, generate SBOMs, identify container risks, and prioritize remediation with runtime intelligence.
Secure containerized applications with image scanning, software supply chain analysis, and runtime-informed prioritization that cuts through vulnerability noise.

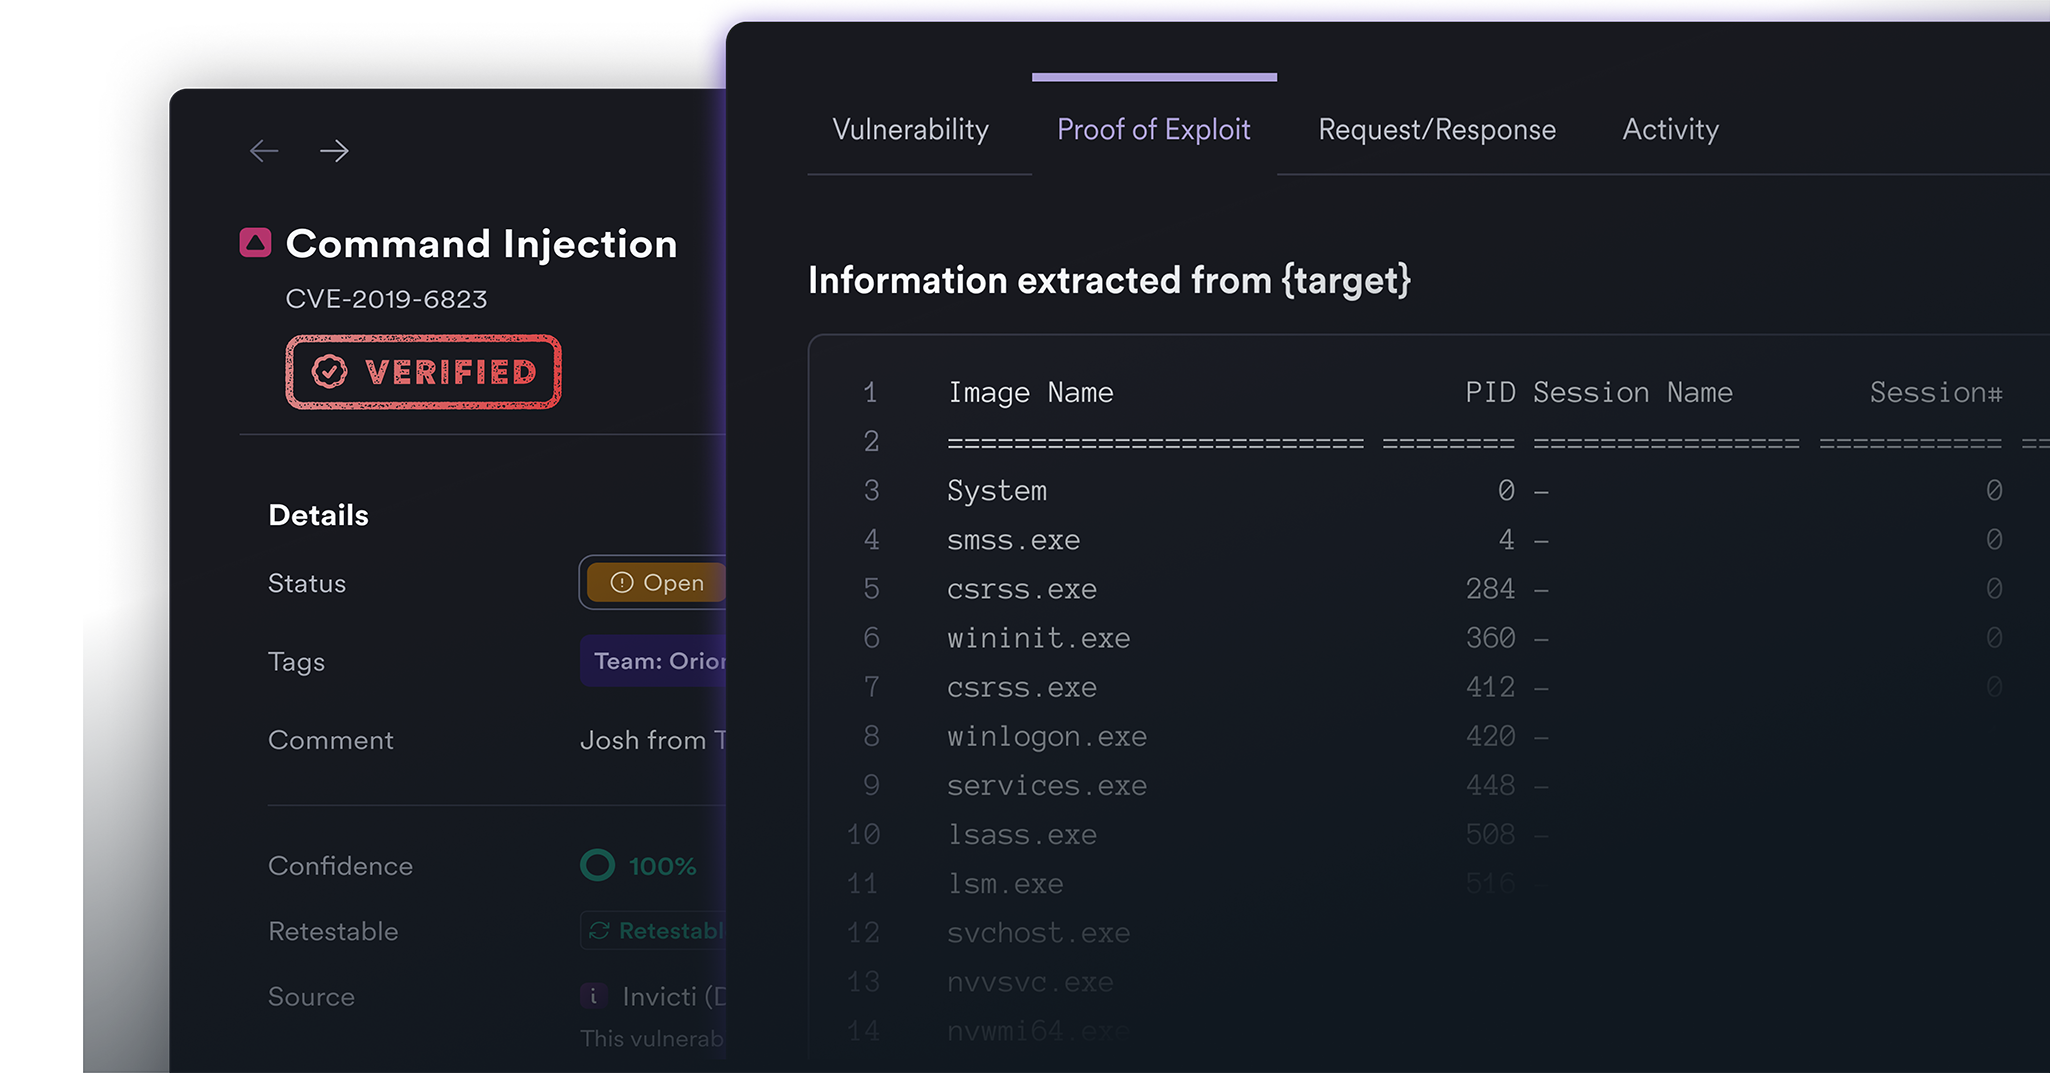
Invicti’s industry-leading DAST engine delivers proof-based scanning with an industry-best 99.98% accuracy. Fully integrated into your SDLC, it scales effortlessly across teams and portfolios.
Invicti scans REST, SOAP, and GraphQL APIs with the same depth and accuracy as web apps—validating vulnerabilities with proof before they reach production. Documented or not, your APIs get full coverage, automatically.
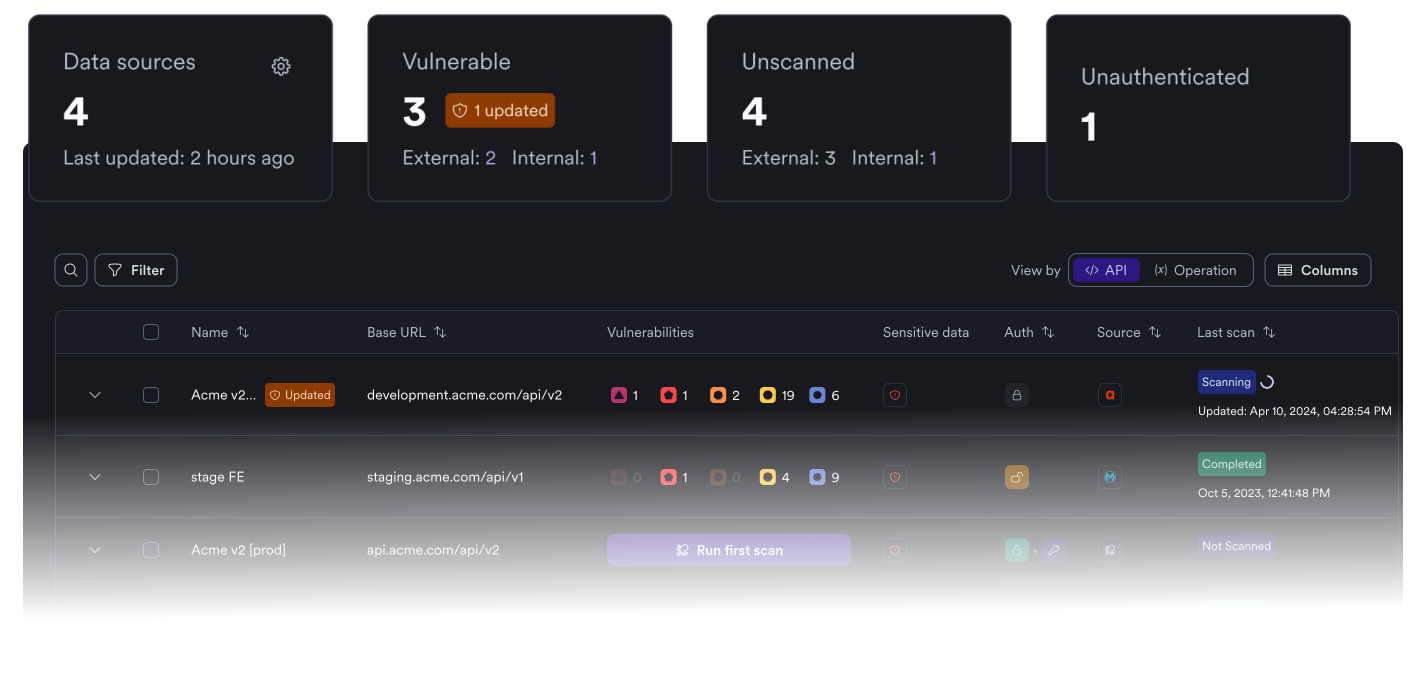
Invicti’s runtime-verified ASPM unifies, validates, prioritizes, and acts on AppSec risk. Get a single source of truth with policy enforcement and audit-ready reporting.
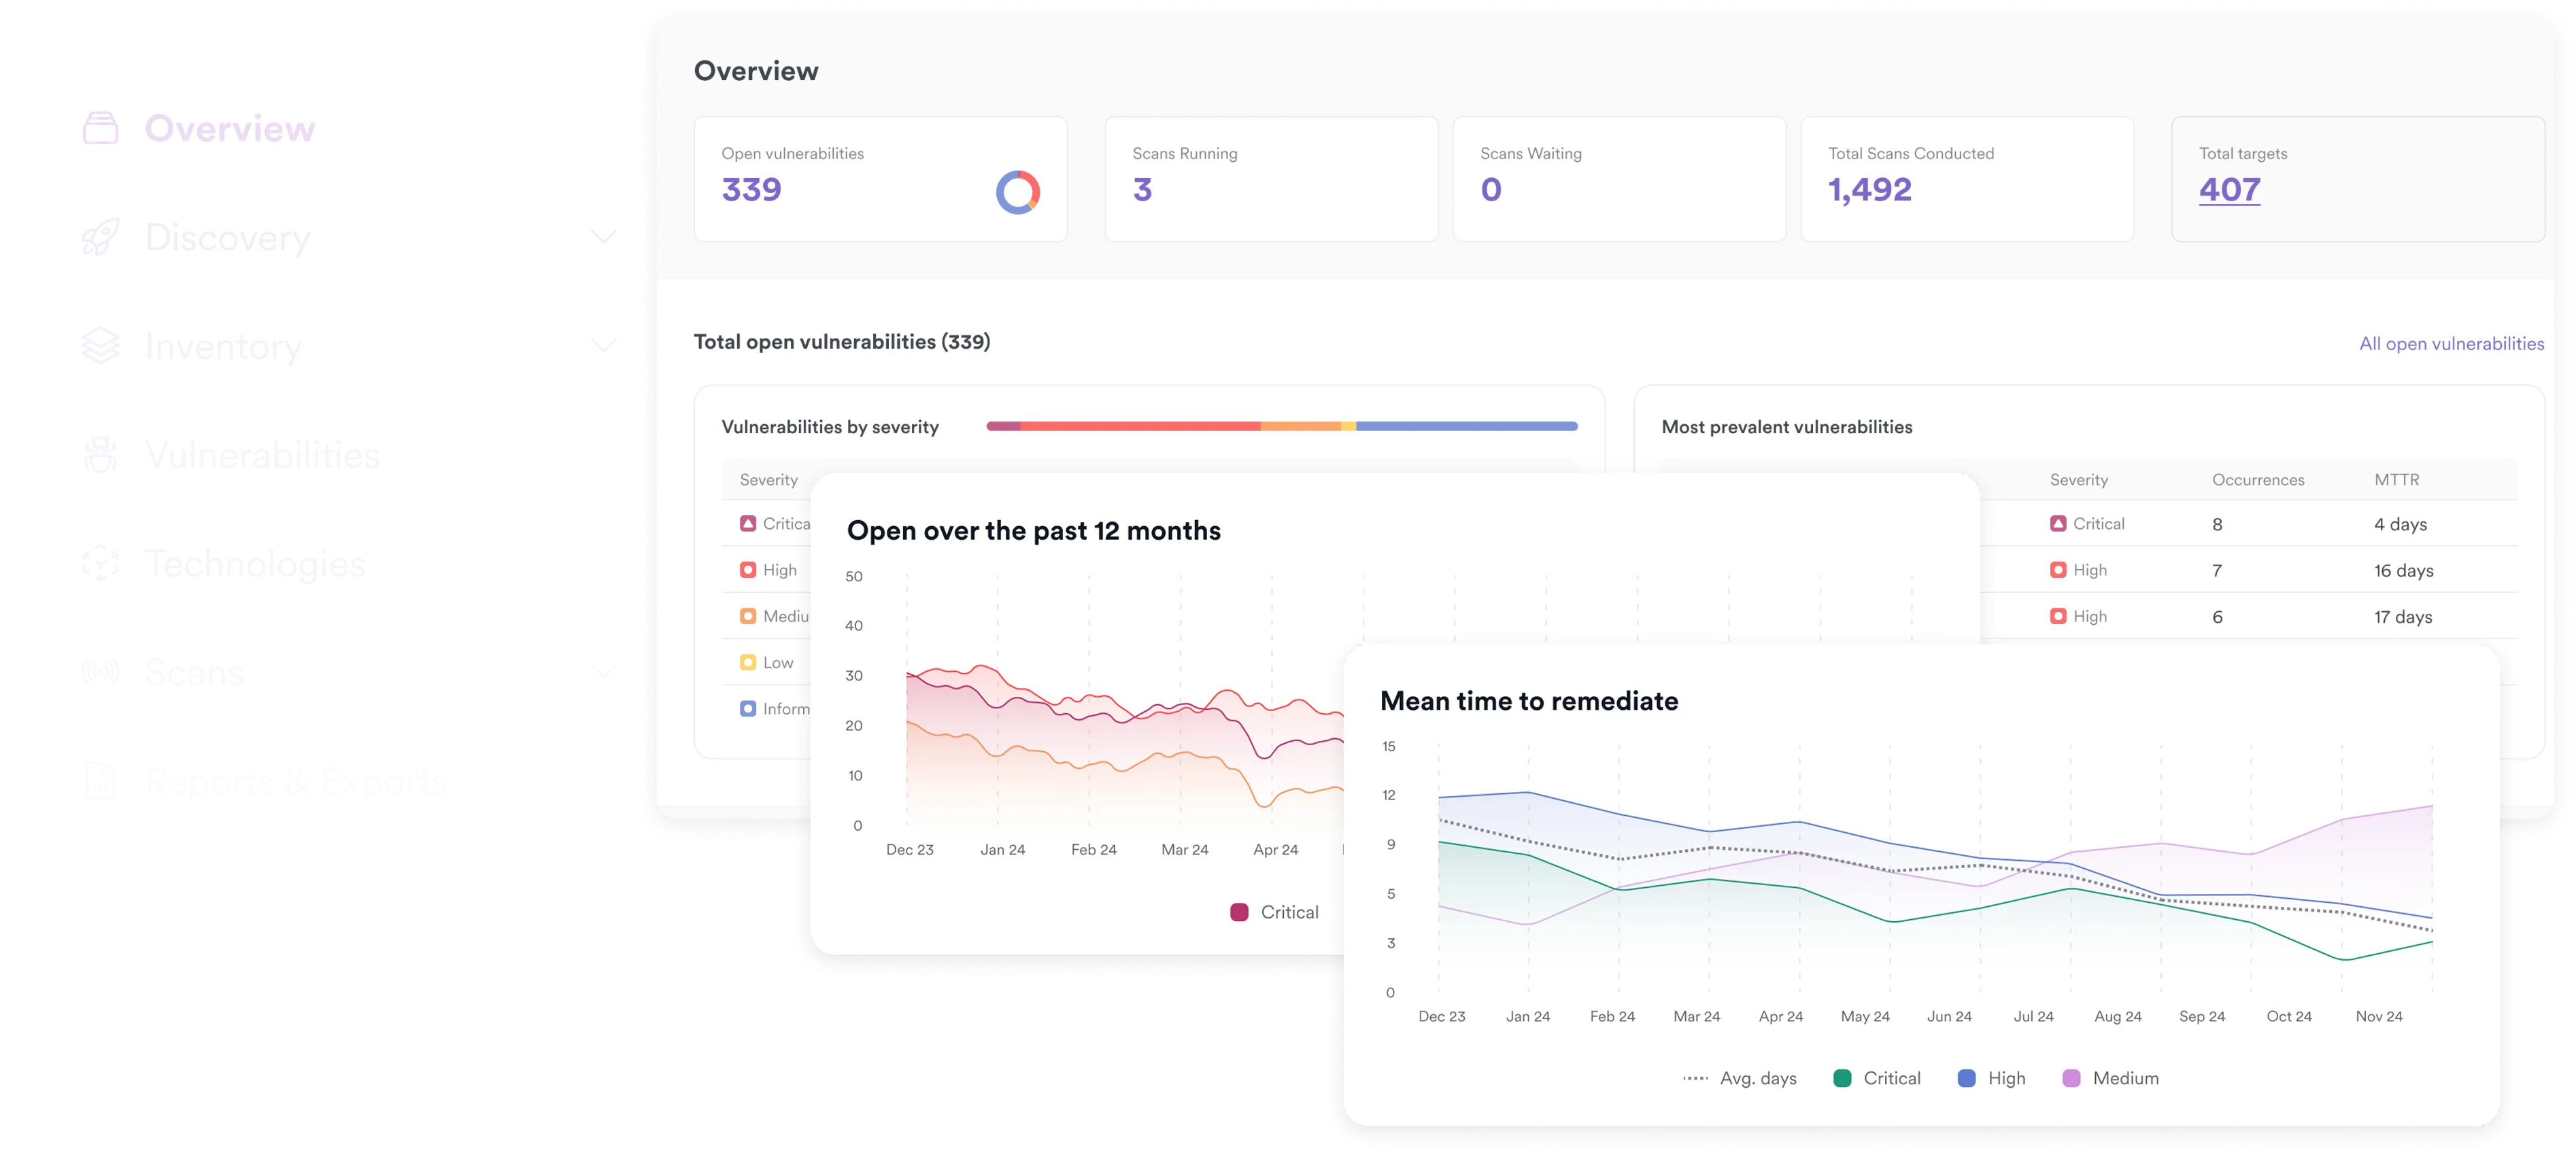
Invicti SAST moves beyond theoretical findings by connecting static analysis to verified runtime vulnerabilities, code ownership, and remediation guidance.
Discover vulnerable dependencies, generate SBOMs, identify container risks, and prioritize remediation with runtime intelligence.
Secure containerized applications with image scanning, software supply chain analysis, and runtime-informed prioritization that cuts through vulnerability noise.
Invicti’s industry-leading DAST engine delivers proof-based scanning with an industry-best 99.98% accuracy. Fully integrated into your SDLC, it scales effortlessly across teams and portfolios.
Invicti scans REST, SOAP, and GraphQL APIs with the same depth and accuracy as web apps—validating vulnerabilities with proof before they reach production. Documented or not, your APIs get full coverage, automatically.
Invicti’s runtime-verified ASPM unifies, validates, prioritizes, and acts on AppSec risk. Get a single source of truth with policy enforcement and audit-ready reporting.
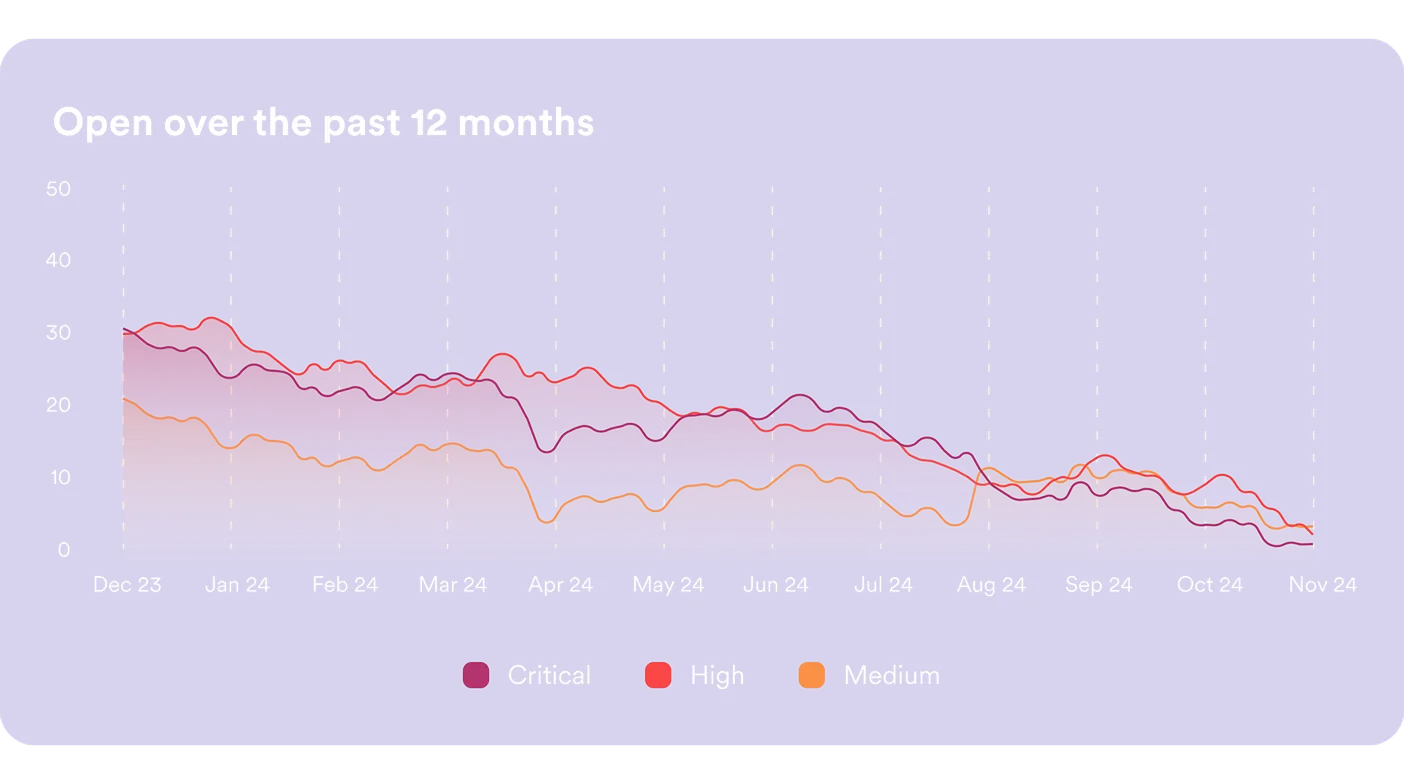
Map client web apps and APIs. Establish risk tiers and scanning cadence. Define the SLA that becomes the commercial basis of the managed service.
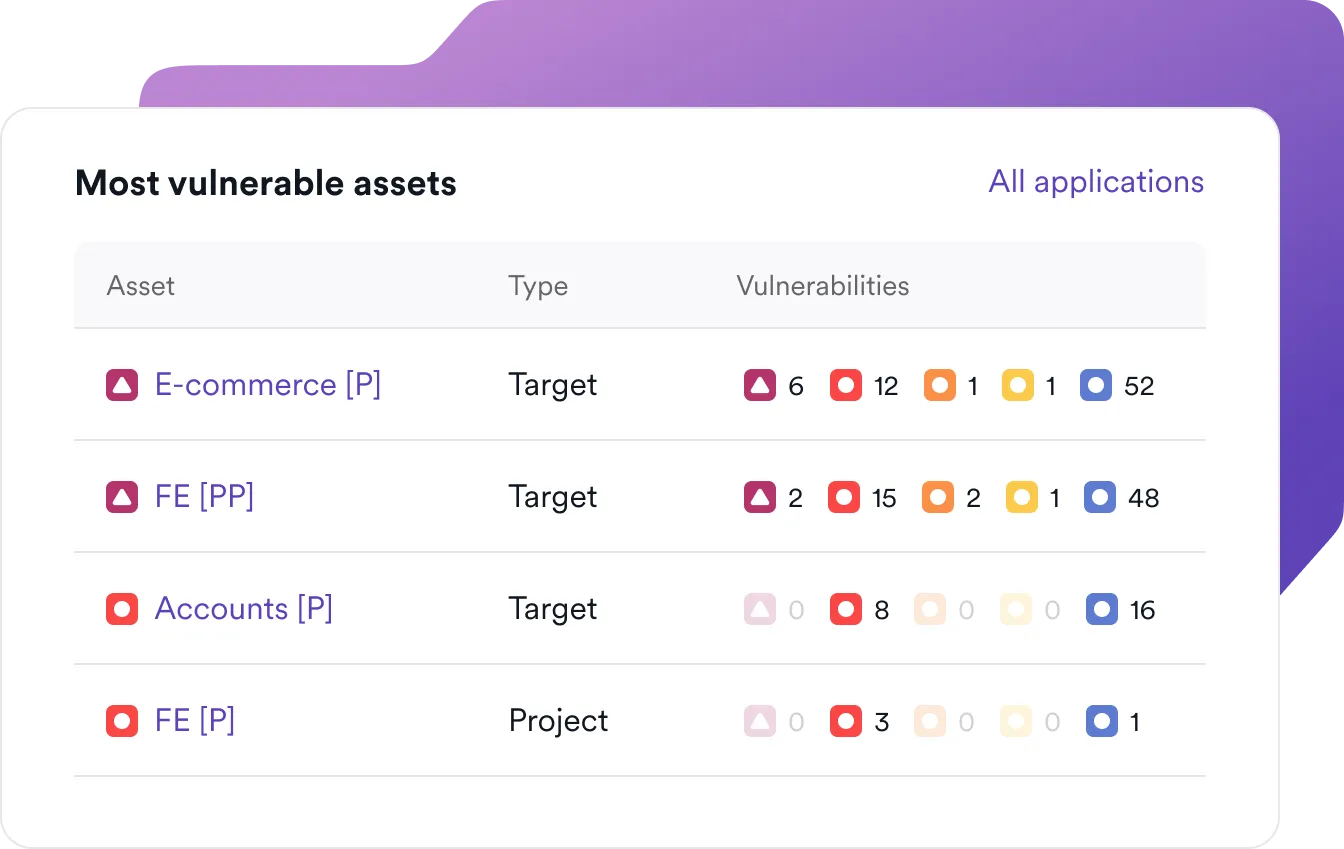
Authenticated DAST and API scans establish the vulnerability profile. Deliver an initial risk report and remediation roadmap — a billable first deliverable.
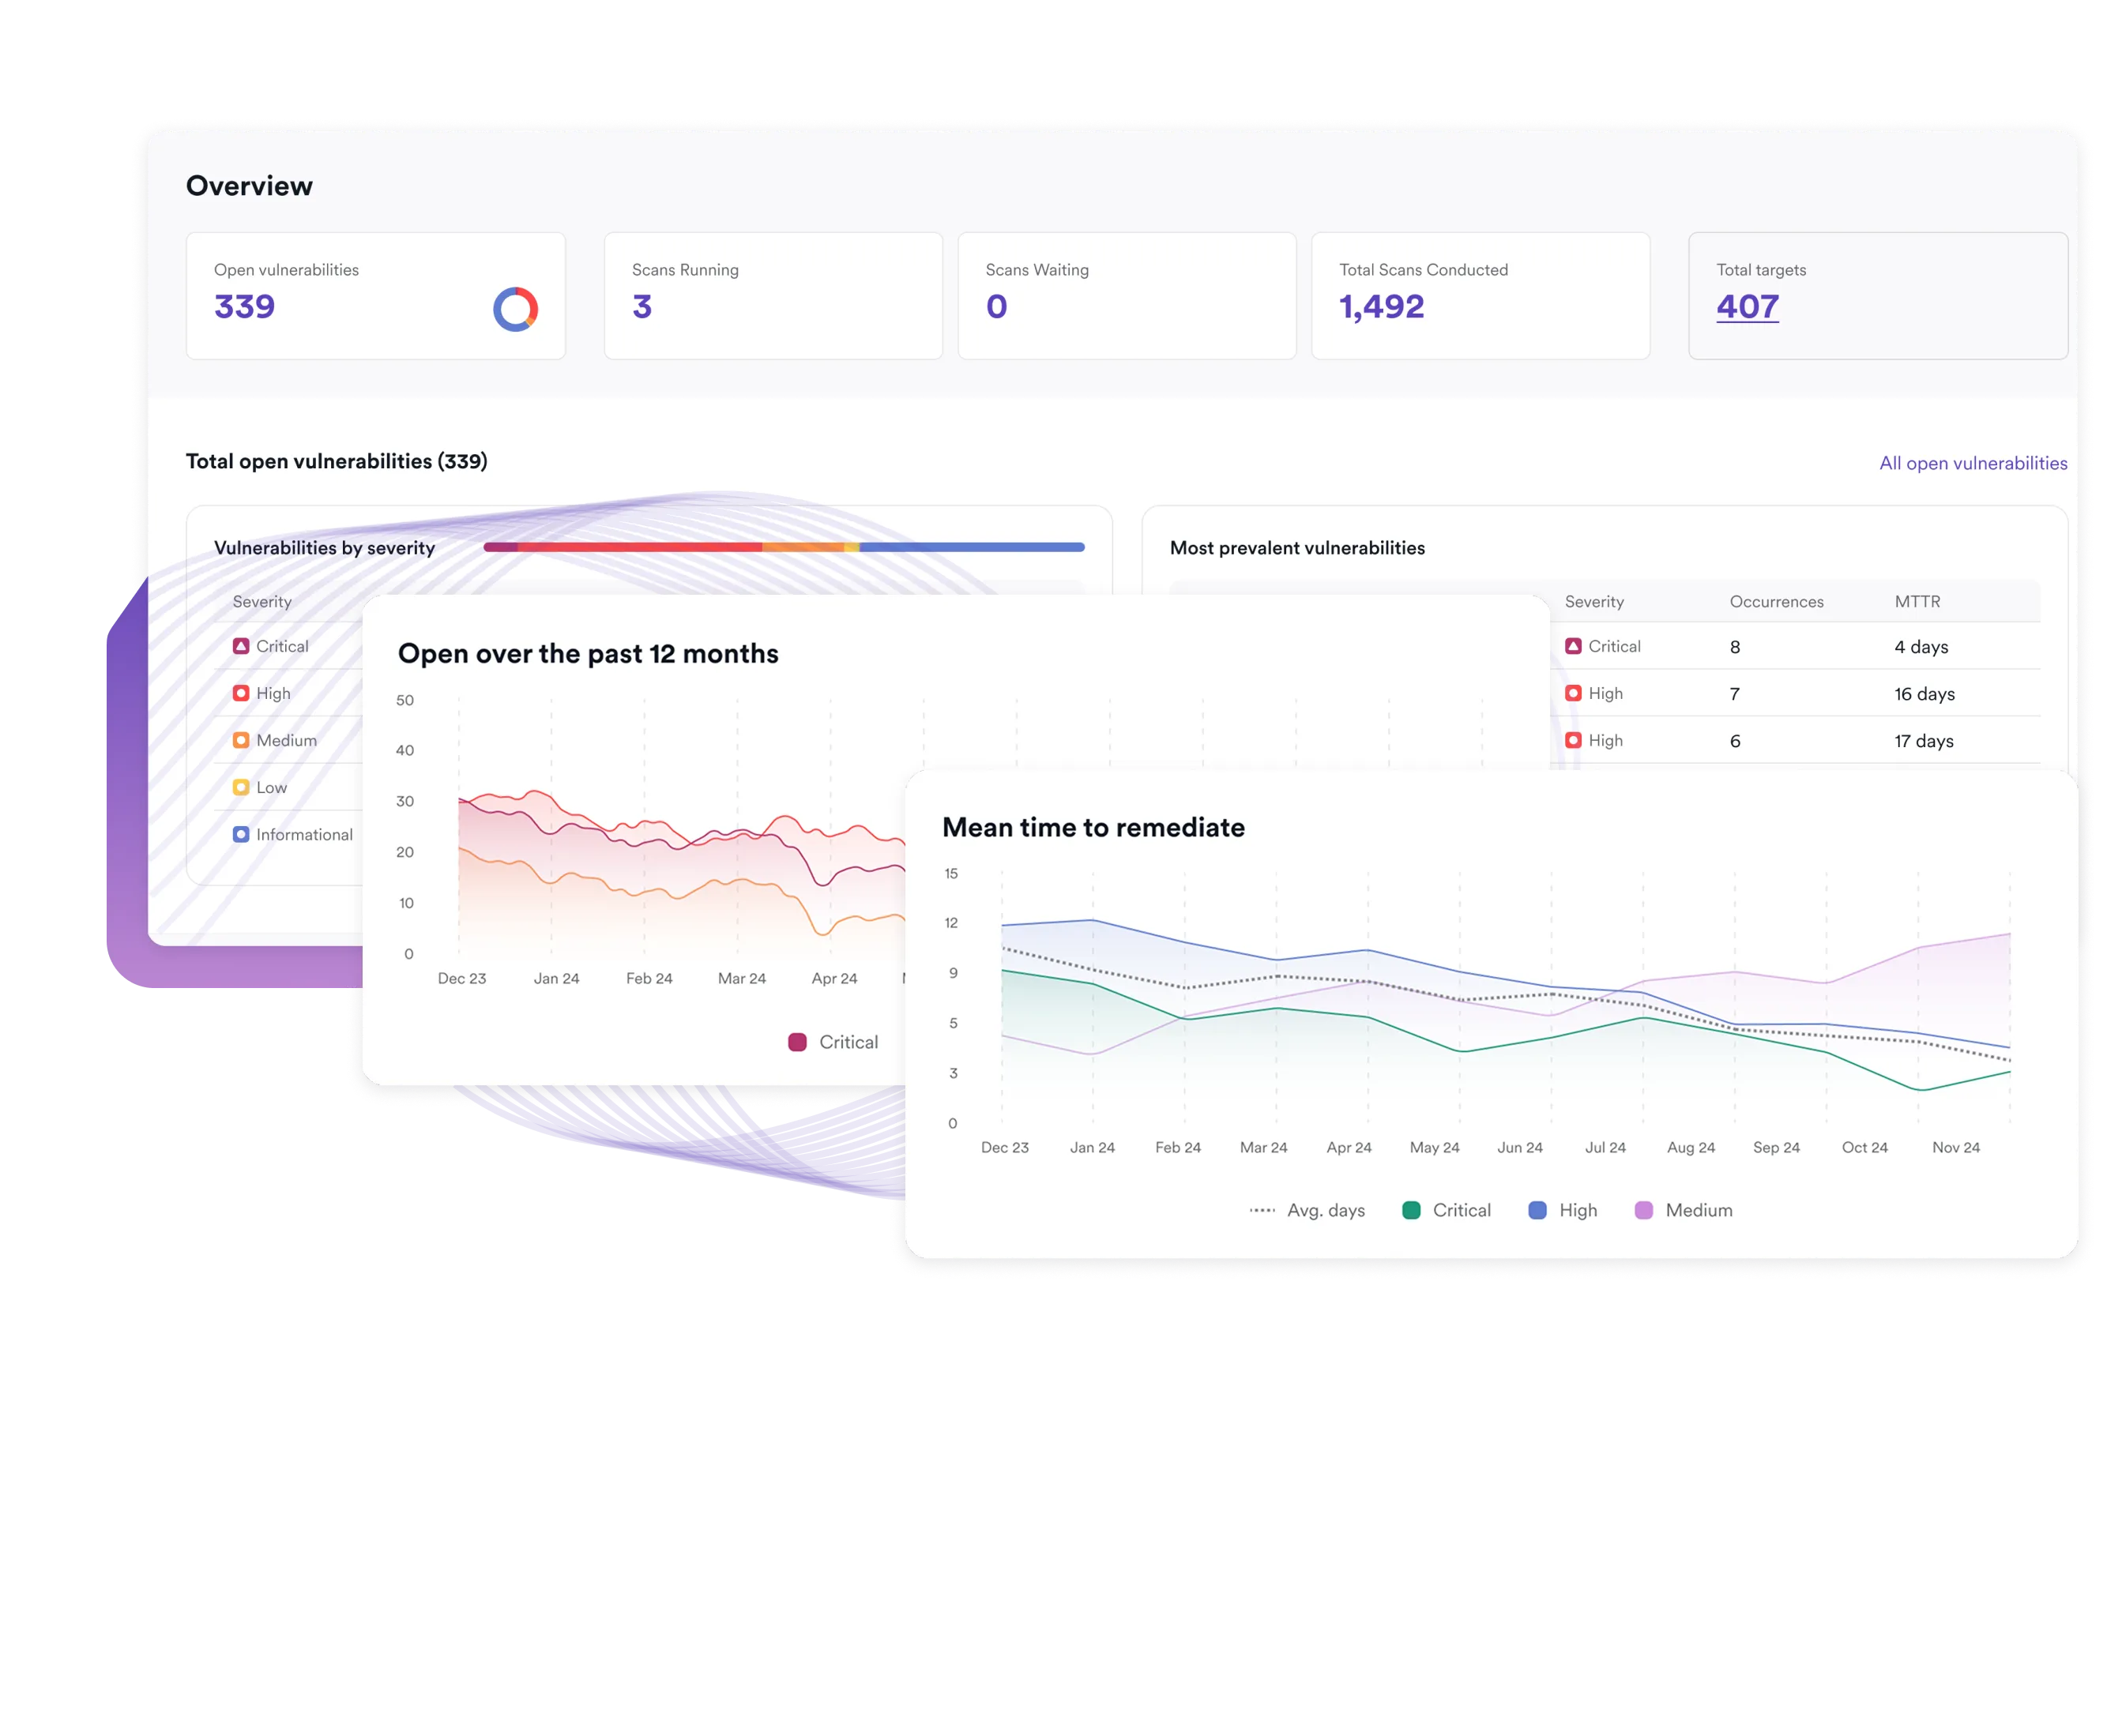
Scheduled scans aligned to release cadence. Severity-based alerting to your SOC. Auto-generated tickets in client systems when new vulnerabilities land.
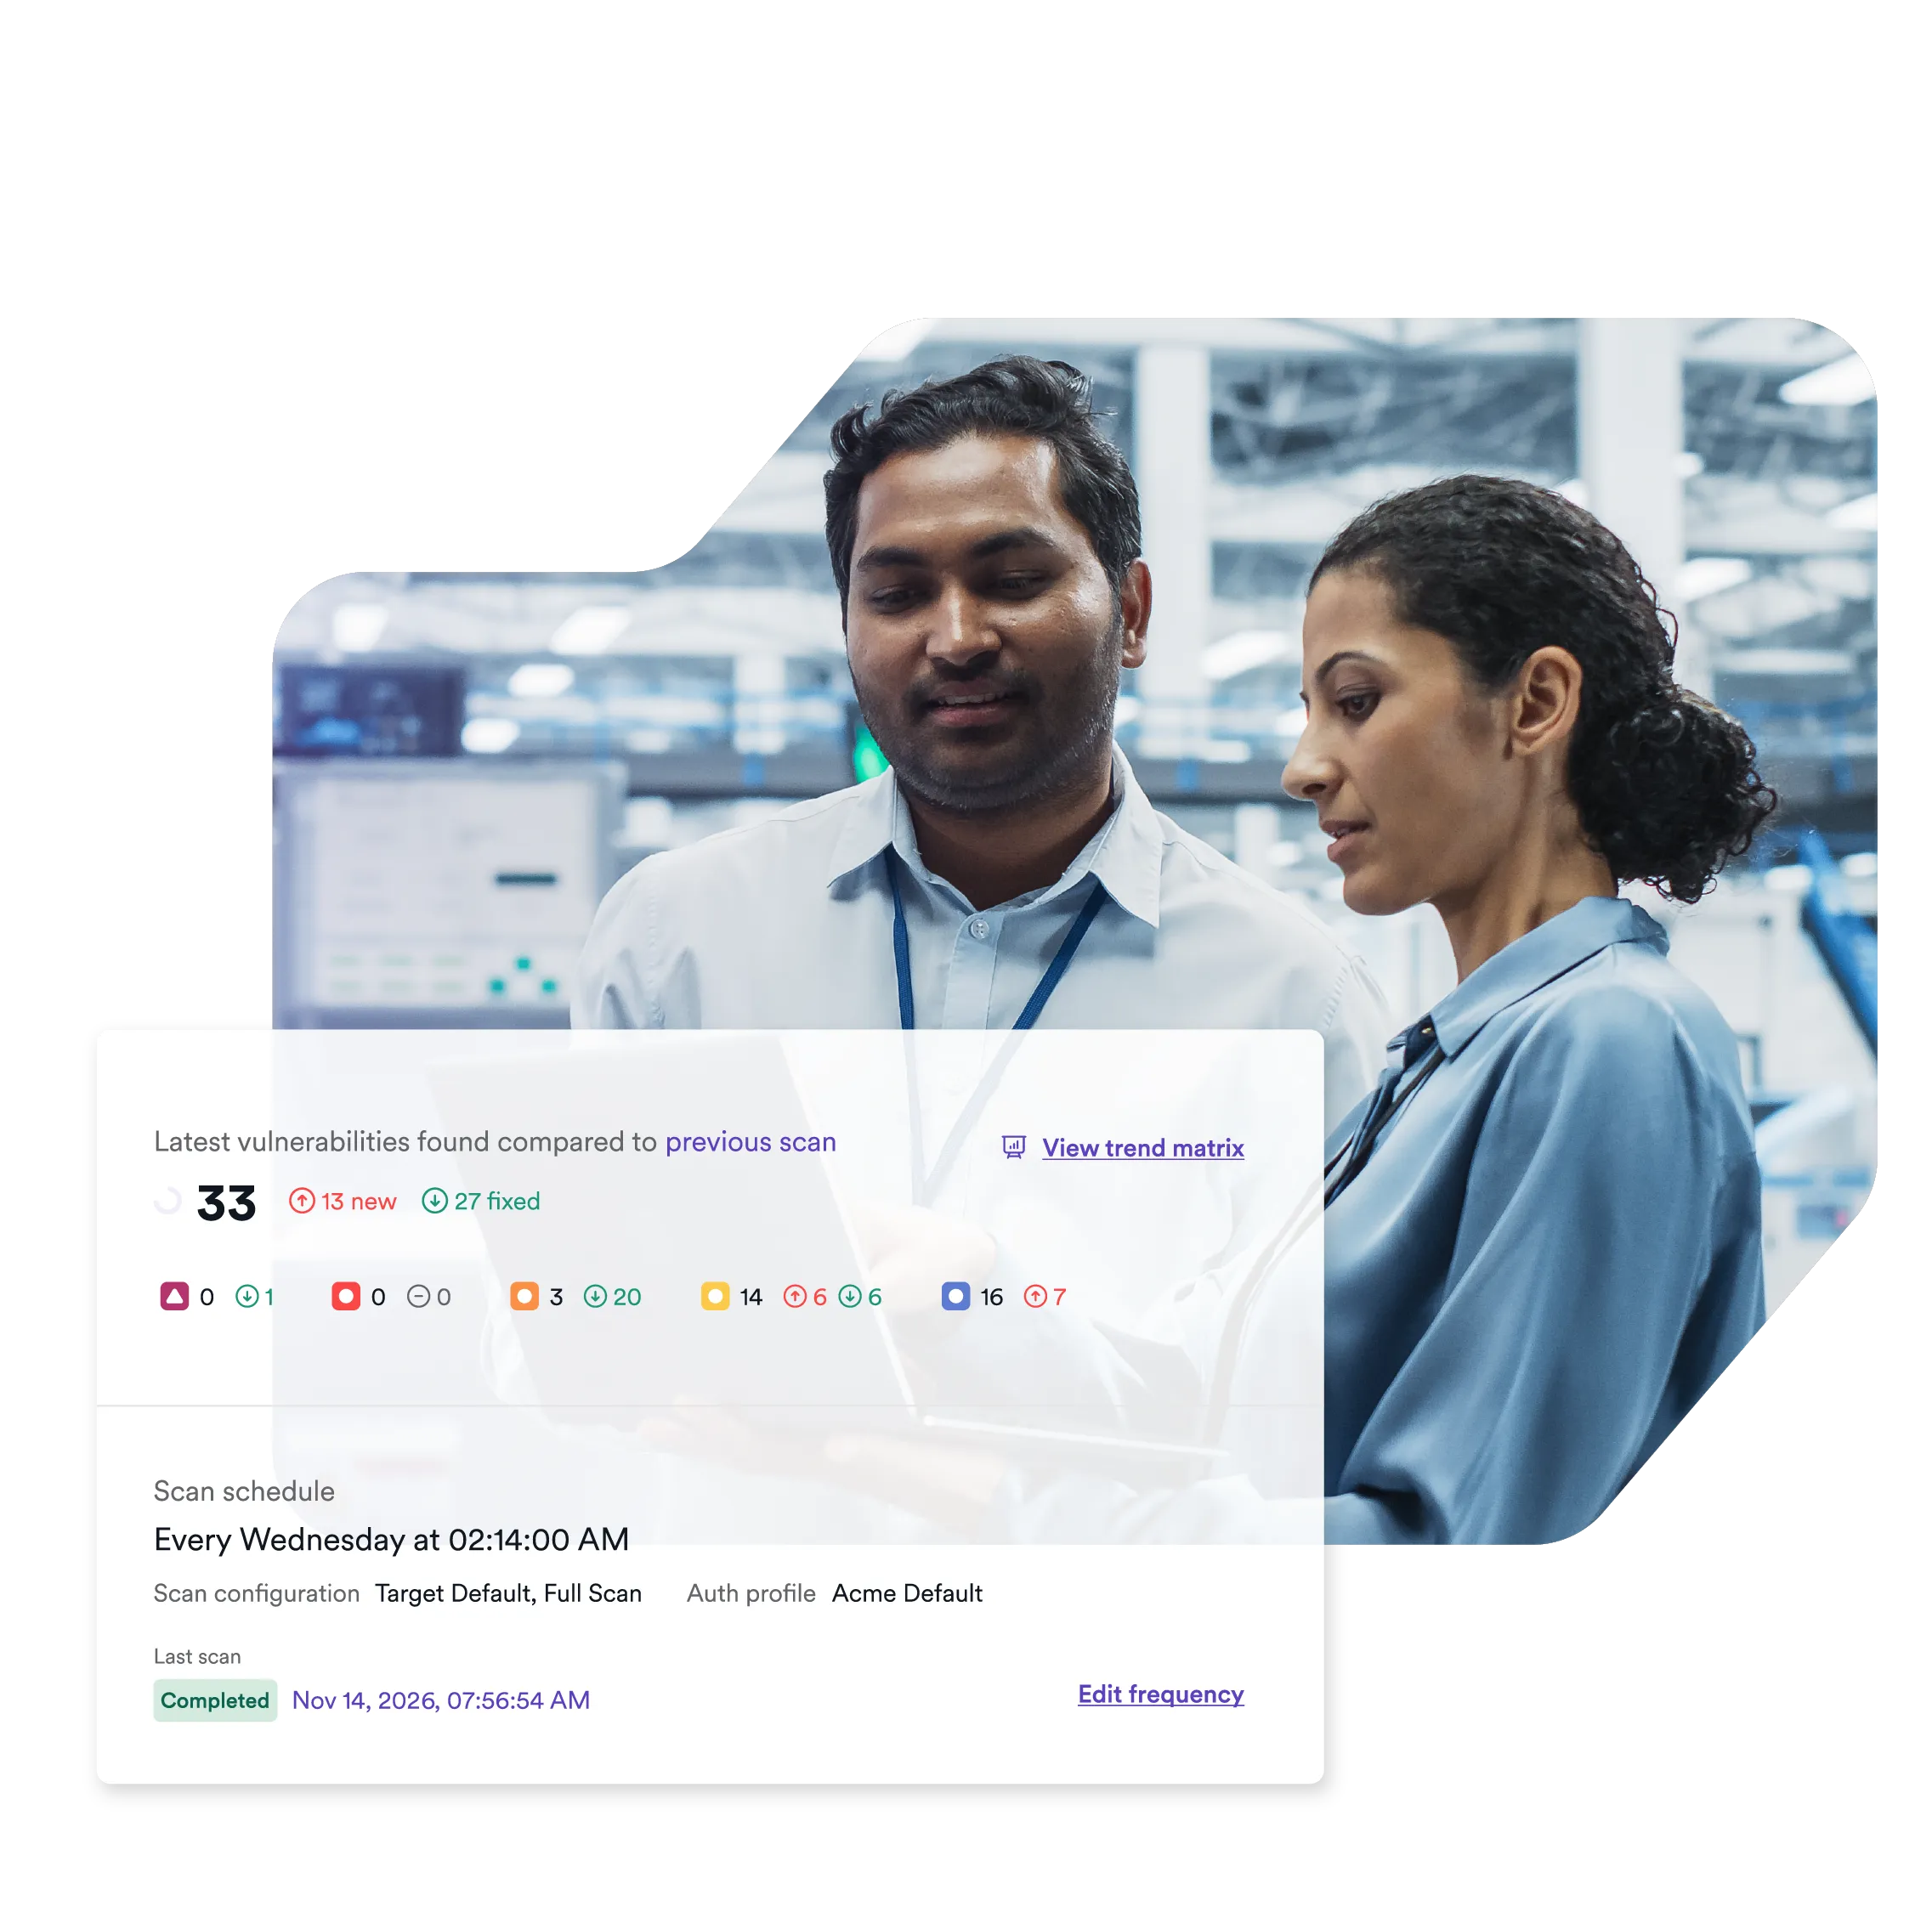
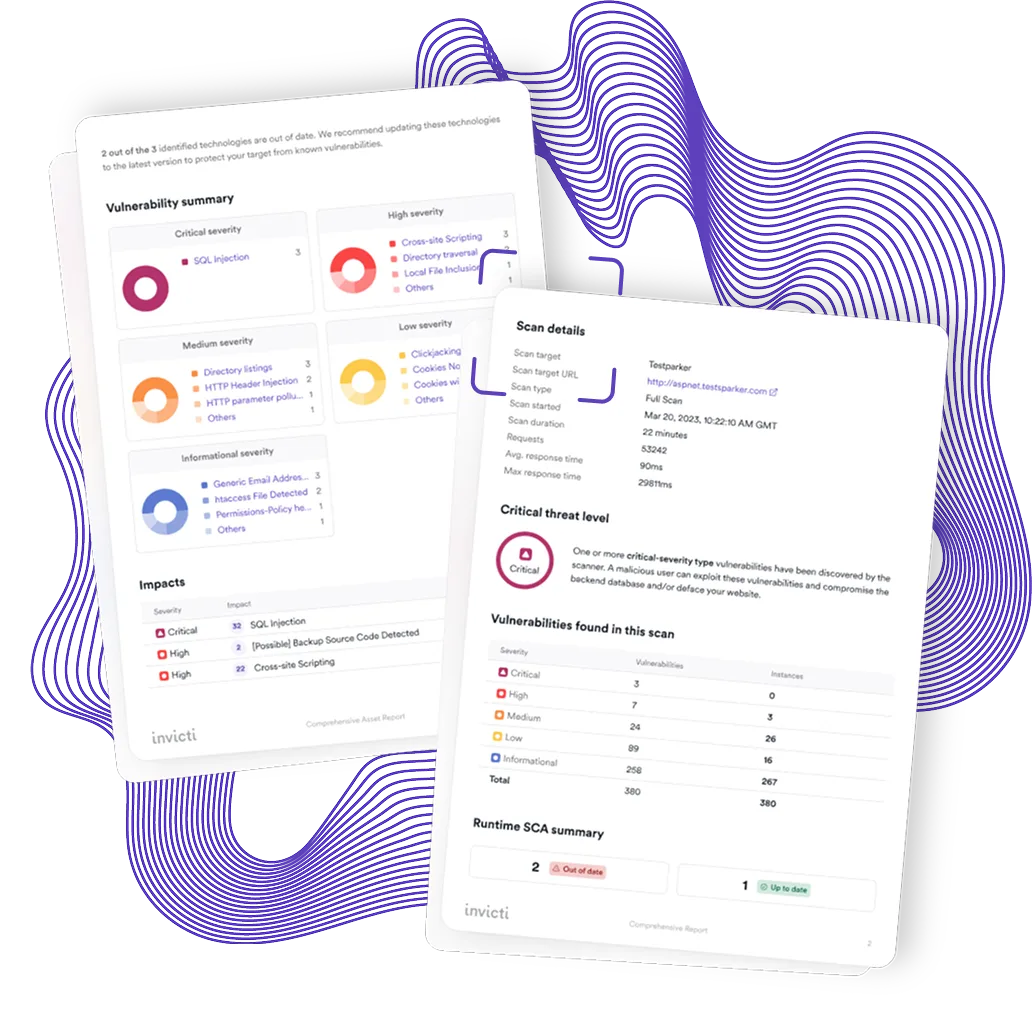
White-label posture scorecards and trend reports. Use QBRs to demonstrate progress and expand scope — adding new apps, compliance modules, and advisory services.
“For more websites, we now don’t need to go externally for security testing. We can fire up Invicti, run the tests as often as we like, view the scan results, and mitigate to our hearts’ content. As a result, the budget we were spending every year on penetration testing decreased by approximately 60% almost immediately and went down even more the following year, to about 20% of our initial spending.”
“Invicti detected web vulnerabilities that other solutions did not. It is easy to use and set up...”

“I had the opportunity to compare expertise reports with Invicti ones. Invicti was better, finding more breaches.”

“Invicti is the best web application security scanner in terms of price-benefit balance. It is a very stable software, faster than the previous tool we were using and it is relatively free of false positives, which is exactly what we were looking for.”