Protect patient data with runtime proof
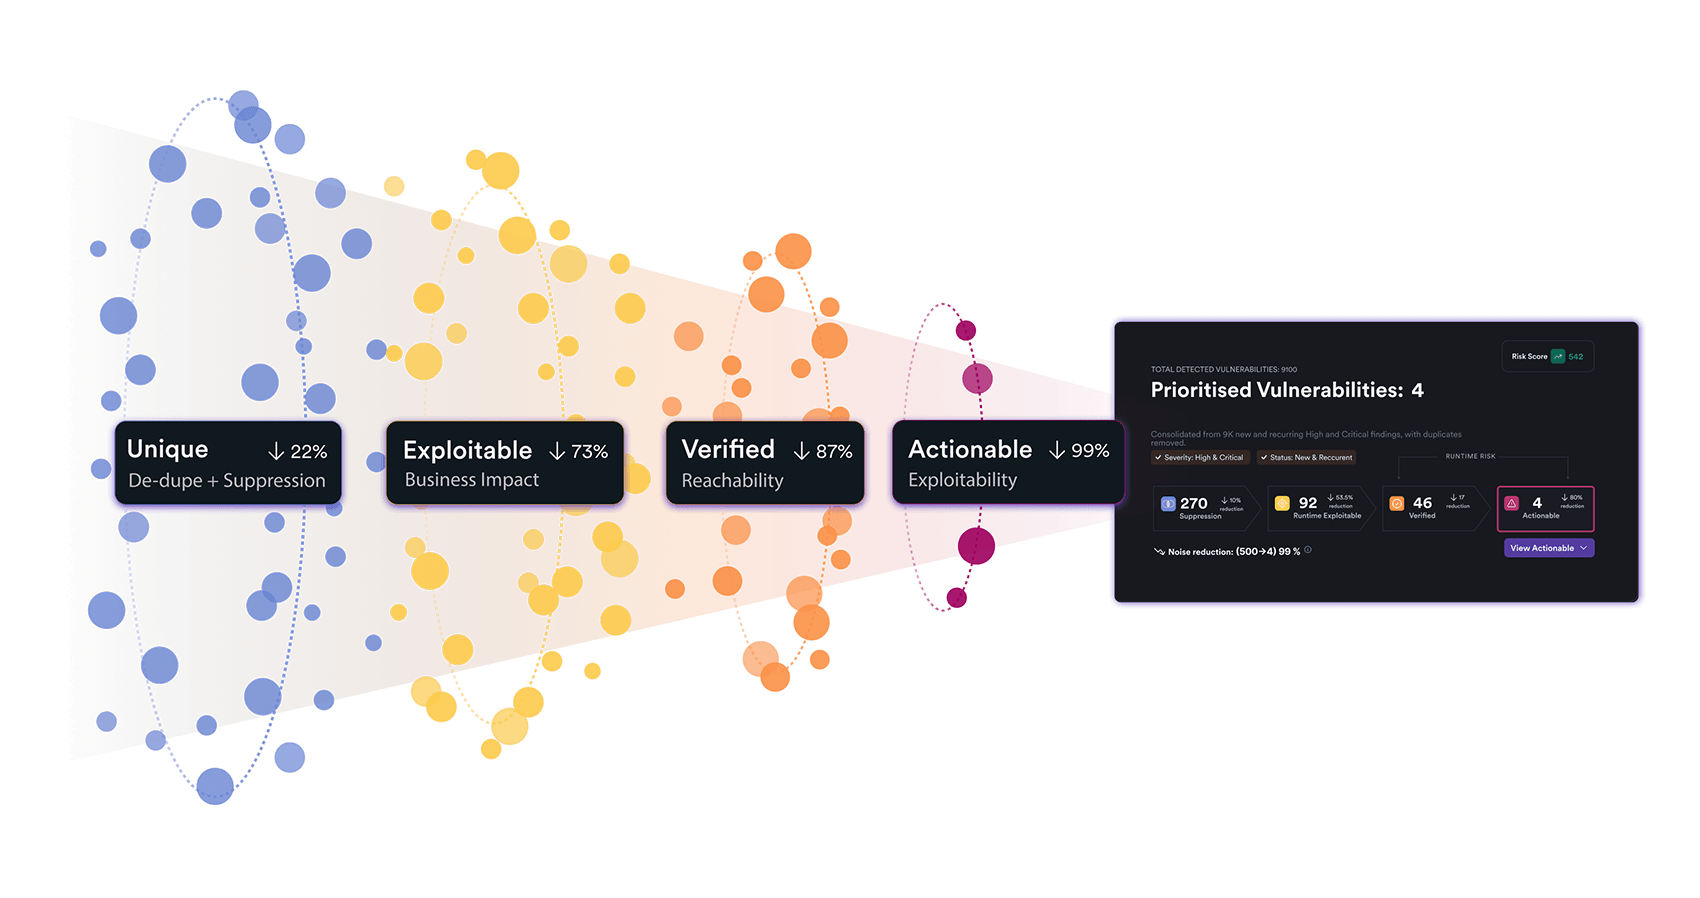
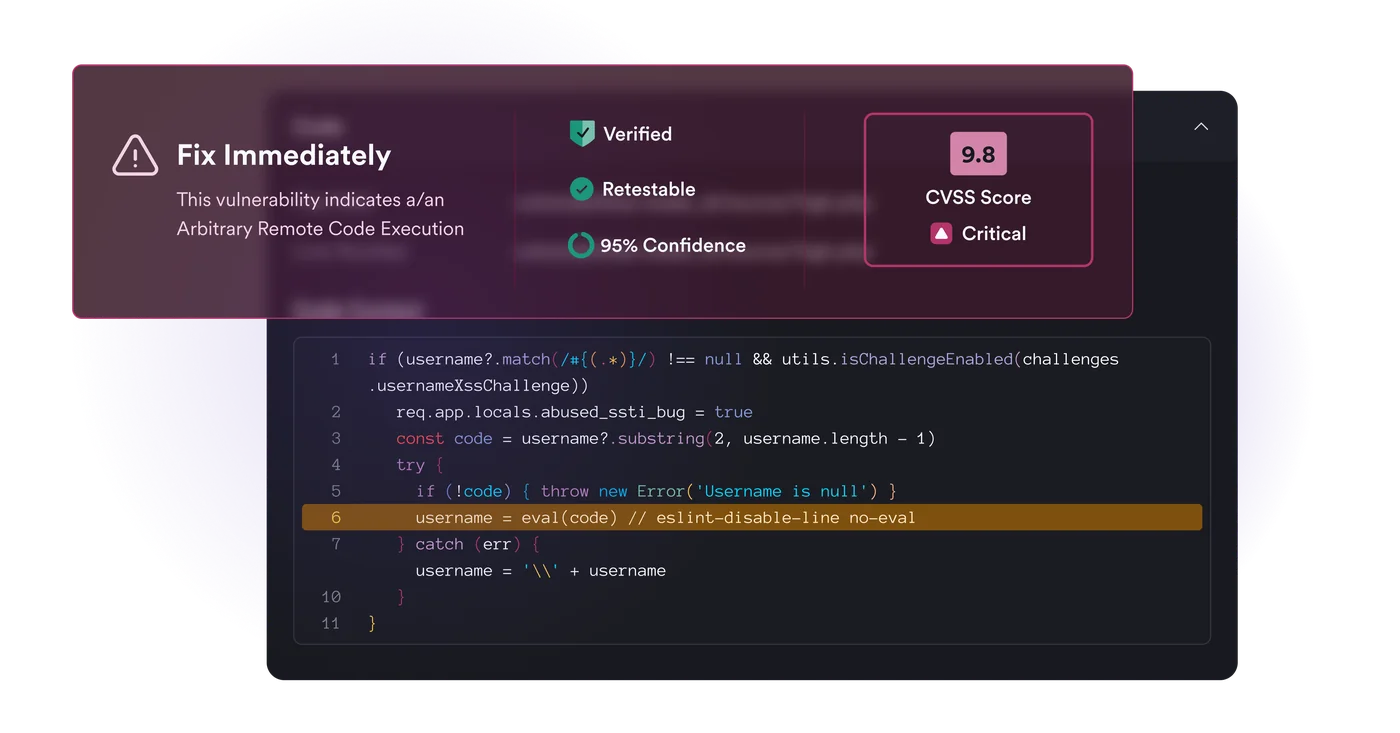
Secure patient portals, healthcare applications, and APIs. Find exploitable vulnerabilities, focus remediation on real risk, and support HIPAA security efforts with actionable evidence.


Secure patient data with evidence
Test applications and APIs, validate real risk, and document remediation to support HIPAA security efforts.


Continuously secure critical applications
Support healthcare compliance
5000+ Top Organizations Trust Invicti

.webp)

Secure patient data with proof
Accurate findings and faster fixes, backed by independent benchmark results.
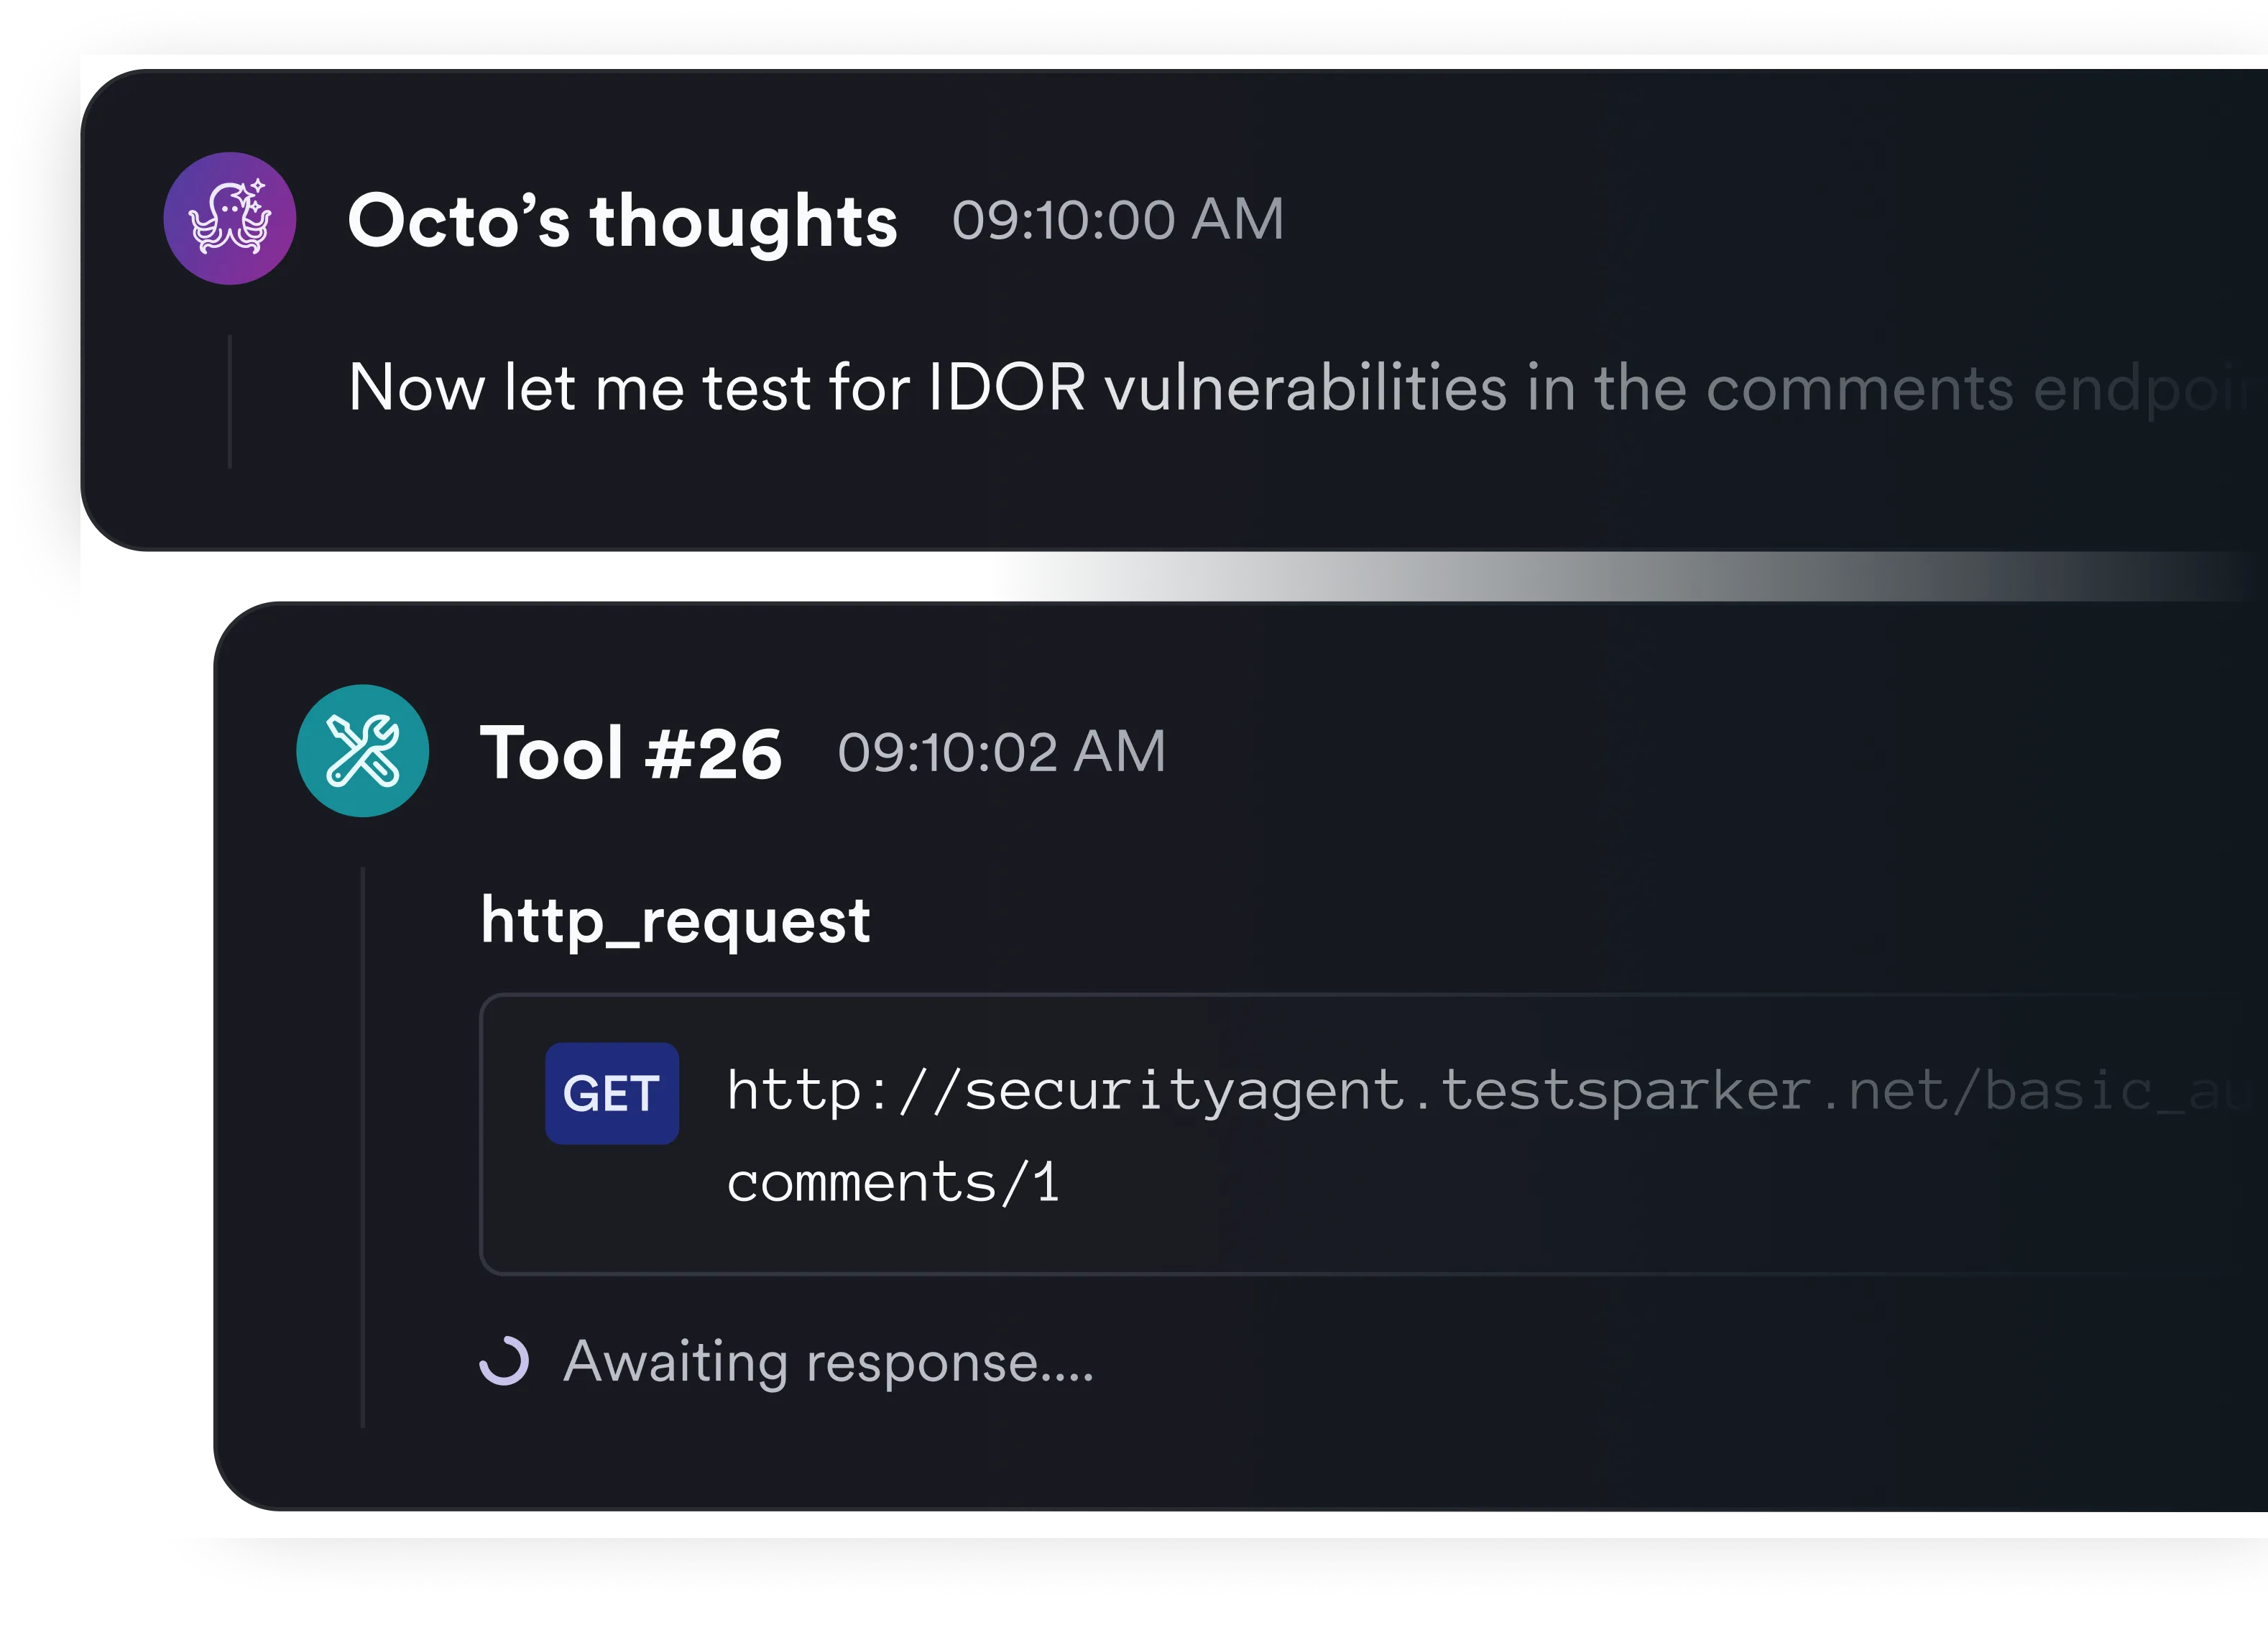
Test applications the way attackers do.
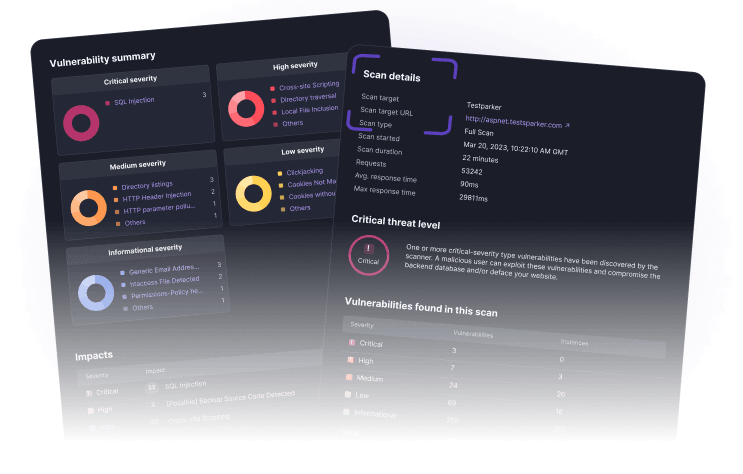
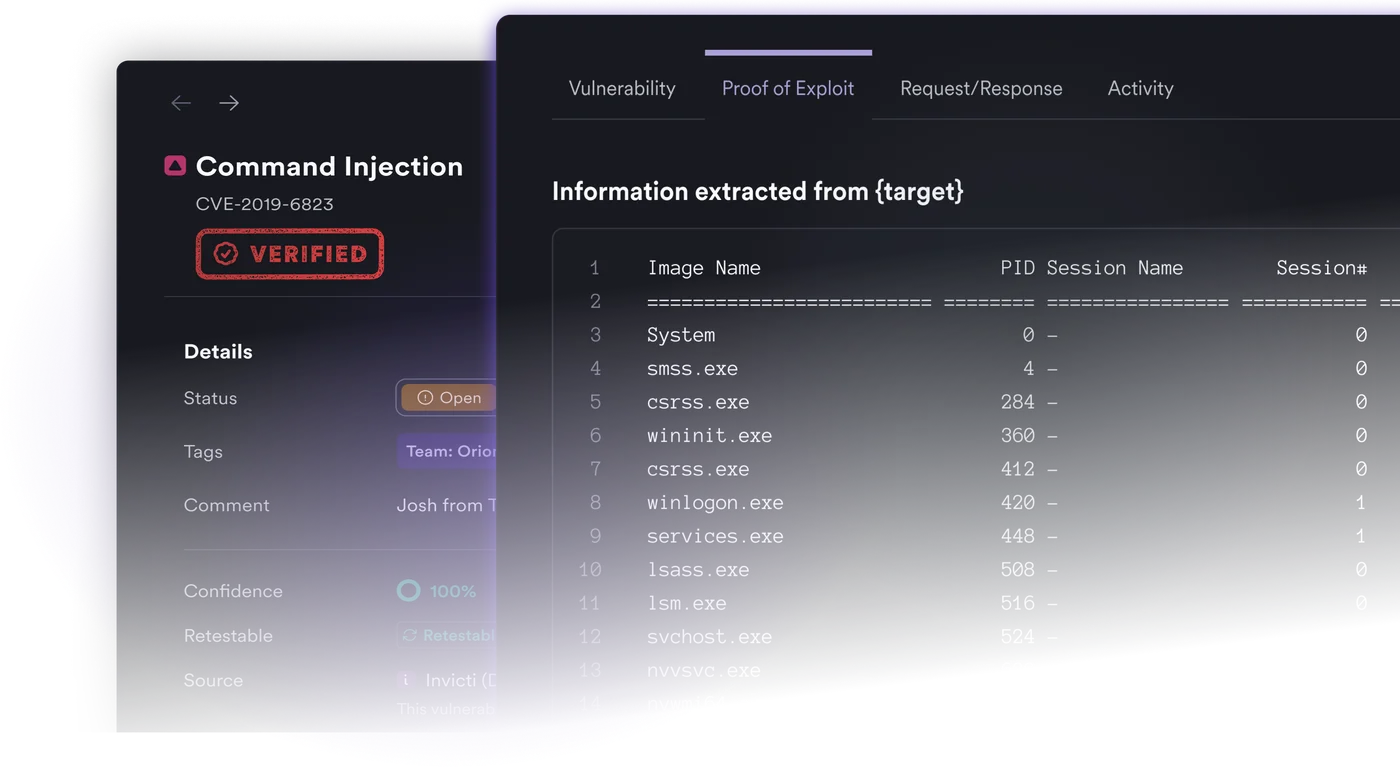
Confirmed by Miercom as the industry’s most accurate DAST. Scan running web applications and APIs, validate findings with proof-based scanning, and focus developers on the vulnerabilities that pose real business risk.

Find, prioritize, and remediate code vulnerabilities
Invicti SAST moves beyond theoretical findings by connecting static analysis to verified runtime vulnerabilities, code ownership, and remediation guidance.

Take control of open-source risk
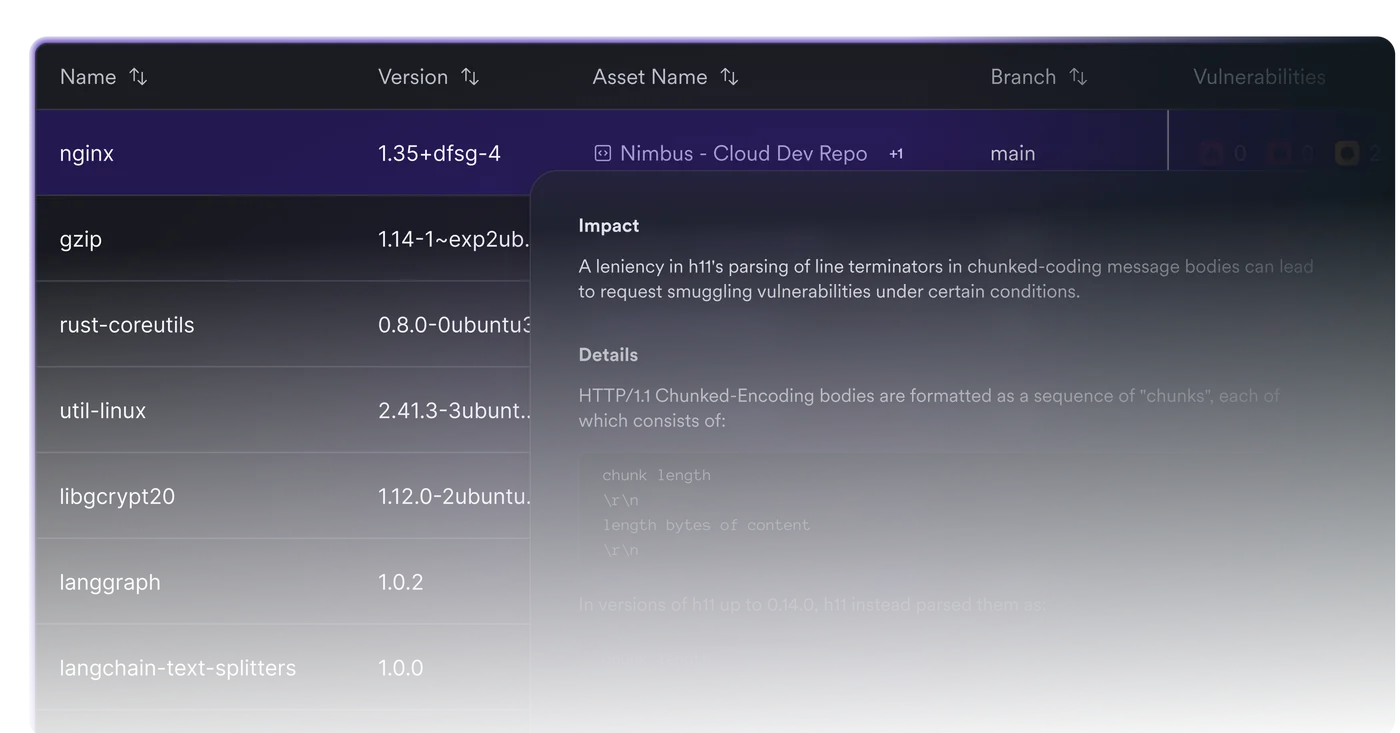
Discover vulnerable dependencies, generate SBOMs, identify container risks, and prioritize remediation with runtime intelligence.

Stop IaC Vulnerabilities Before Production
Detect misconfigurations early, enforce security policies in CI/CD, and track IaC risk alongside code and runtime findings.

Find exposed secrets
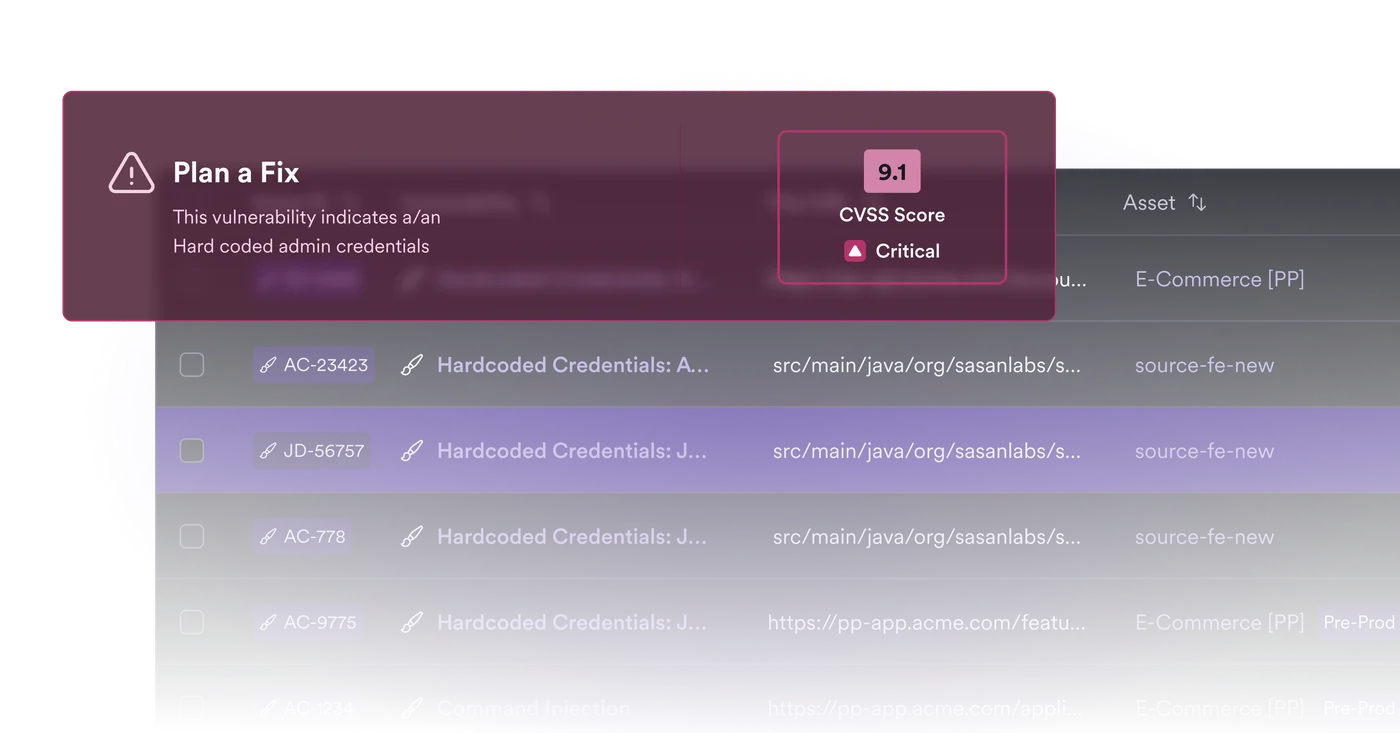
Invicti finds and surfaces exposed API keys, passwords, encryption keys, and tokens before hackers get the chance to exploit them.

Strengthen container security
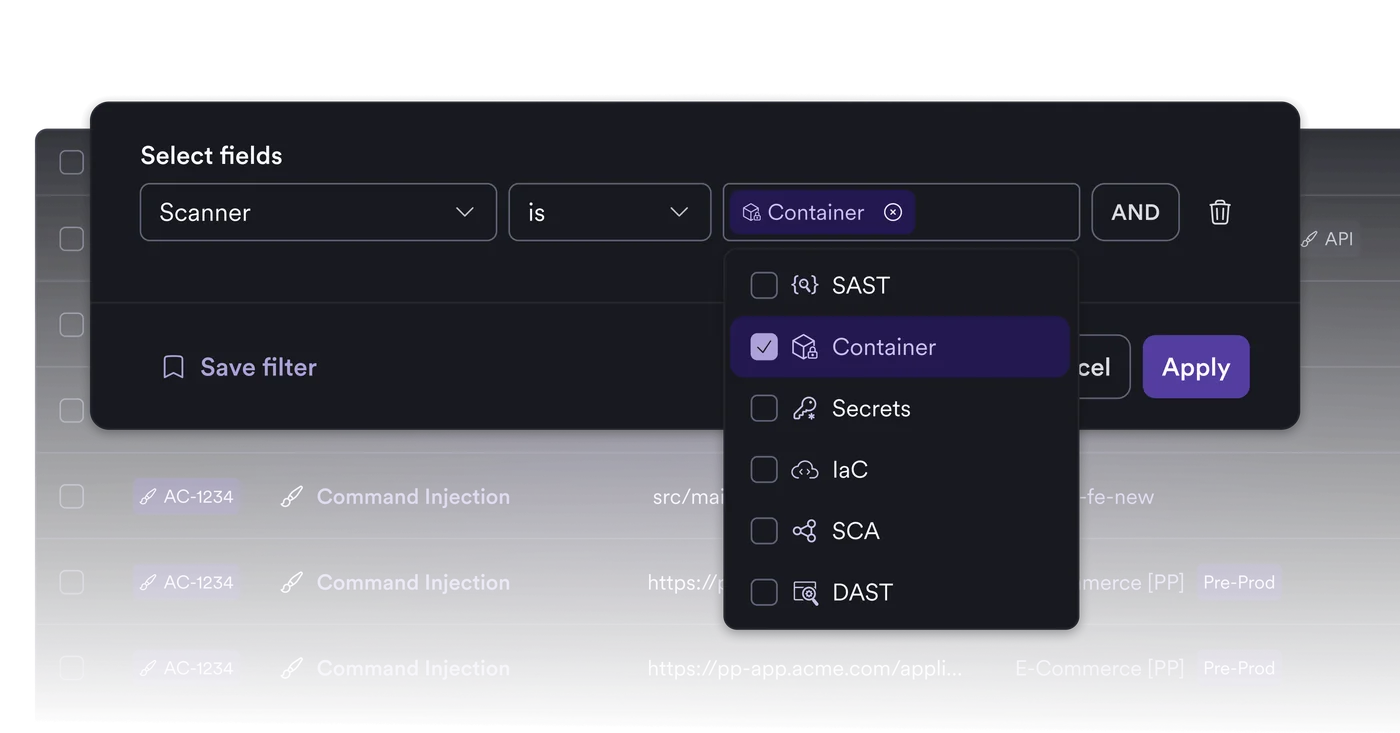
Invicti integrates container scanning with SCA, DAST, and CI/CD workflows so you can track vulnerabilities across registries and clusters, cut through complexity, and prioritize container risk in one unified view.

Test applications the way attackers do.
Confirmed by Miercom as the industry’s most accurate DAST. Scan running web applications and APIs, validate findings with proof-based scanning, and focus developers on the vulnerabilities that pose real business risk.

Find, prioritize, and remediate code vulnerabilities
Invicti SAST moves beyond theoretical findings by connecting static analysis to verified runtime vulnerabilities, code ownership, and remediation guidance.

Take control of open-source risk
Discover vulnerable dependencies, generate SBOMs, identify container risks, and prioritize remediation with runtime intelligence.

Stop IaC Vulnerabilities Before Production
Detect misconfigurations early, enforce security policies in CI/CD, and track IaC risk alongside code and runtime findings.

Find exposed secrets
Invicti finds and surfaces exposed API keys, passwords, encryption keys, and tokens before hackers get the chance to exploit them.

Strengthen container security
Invicti integrates container scanning with SCA, DAST, and CI/CD workflows so you can track vulnerabilities across registries and clusters, cut through complexity, and prioritize container risk in one unified view.