
Invicti vs. Tenable Nessus: Validate web app and API risk
Comparing Nessus for application security? Invicti brings deep DAST and API testing together with proof-based validation for supported vulnerabilities, runtime-informed prioritization, and developer-ready remediation workflows.
Get a demo
5,000+ organizations trust Invicti




Compare Invicti and Tenable ratings on G2
What customers say about scanner accuracy and false positives

"Scan results are near perfect with few false positives compared to other costly solutions available in the market."

"The reports contain false positive sometimes that needs to be understood from the application perspective and sorted with business impact points."
"False positives and false negatives are very low."
"Nessus is susceptible to produce false positives and because of that the testers need to put more effort and time."
"Fast and lightweight web application security scanner, their motto is zero false positive and their word is completely true."
"What I dont like this Nessus proffesional version is some time it gives false positives. If those results are false positive, all the search time and testing times are wasted."
"Finds security vulnerabilities very effectively. One of the best zero or less false/positive thread generation."
"Sometimes it Gives false results which lead to waste of my Time."
"Very little false positives and best of all it confirms most of the findings."
"Nessus is susceptible to the development of false positives and therefore the testers need to put more effort and time into this."
Test web applications and APIs beyond infrastructure findings
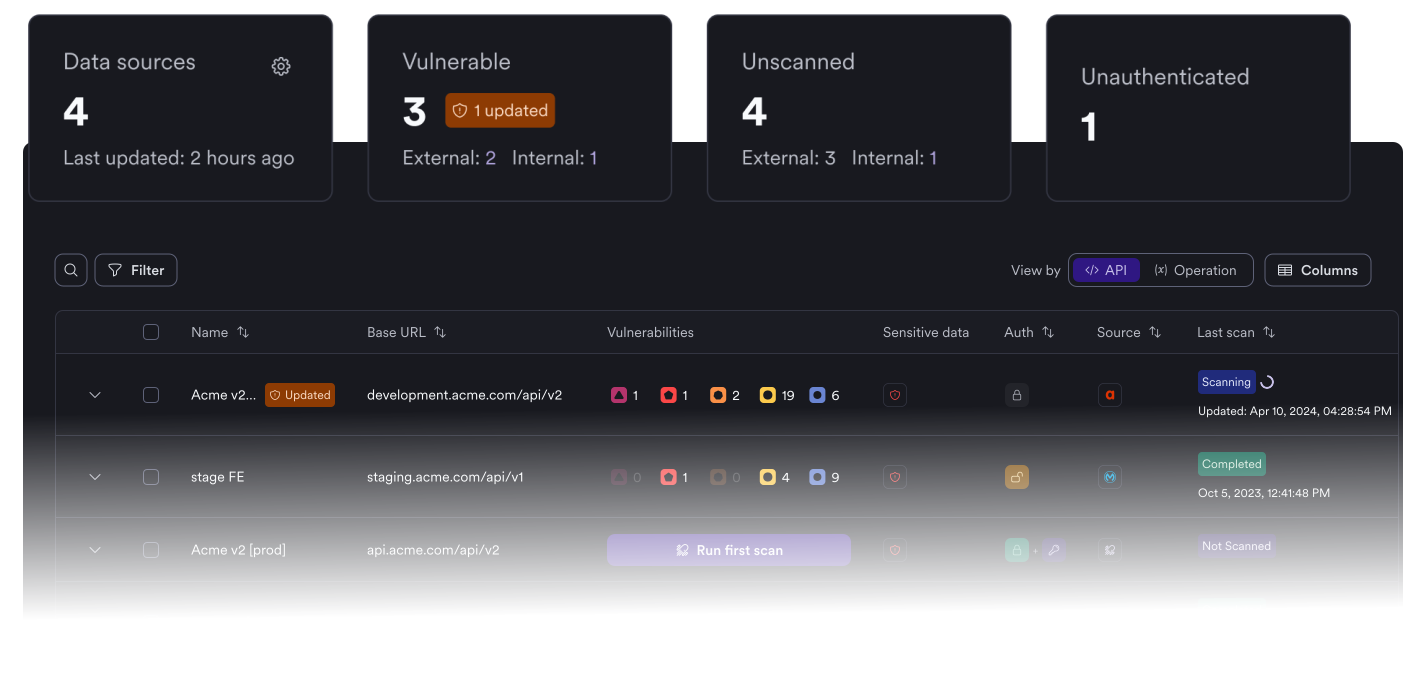
Invicti tests running web applications and APIs for security weaknesses in real workflows, including authenticated and JavaScript-heavy areas. Use dynamic testing evidence to focus remediation on issues attackers may be able to exploit. Testing covers:

The software is an important part of my security strategy which is in progress toward other services at OECD. And I find it better than external expertise. I had, of course, the opportunity to compare expertise reports with Invicti ones. Invicti was better, finding more breaches.
Turn validated vulnerabilities into developer-ready fixes
Proof-based results help developers see why a vulnerability matters and how to reproduce or remediate it. Where static and dynamic findings can be correlated, runtime evidence can also help pinpoint the relevant code. Invicti helps teams:


We scan all our websites for vulnerabilities as they are being developed. These scans are also used to satisfy a yearly scanning requirement from our governing organization. We have identified and corrected over 100 vulnerabilities with Invicti.
Build verified AppSec into existing workflows
Integrate testing into development: Run scans as applications move through build, test, and release workflows. Track findings, fixes, and retesting from a centralized view.

Connect verified findings to your development workflows












Test complex web apps and APIs in runtime
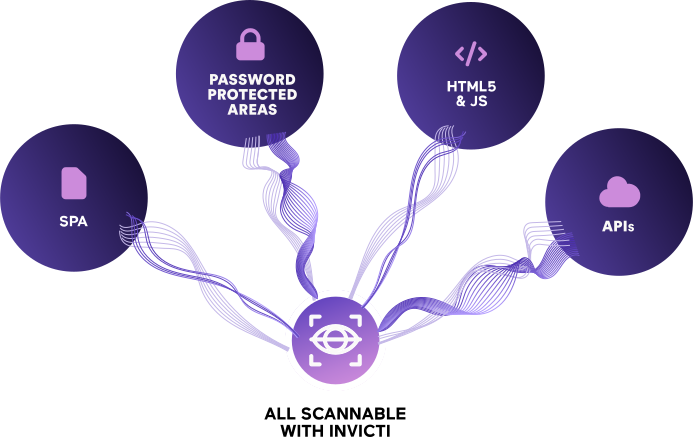
Runtime testing follows application behavior and user workflows to uncover vulnerabilities that are easy to miss in complex environments. Invicti crawls and tests complex applications in runtime, including technologies and workflows that can be difficult to assess with shallow scanning alone:
Invicti is Stable, Accurate and Versatile, with a lot of thought put into each of its features. An excellent product in the arsenal of any security professional.
The AppSec platform built on runtime truth

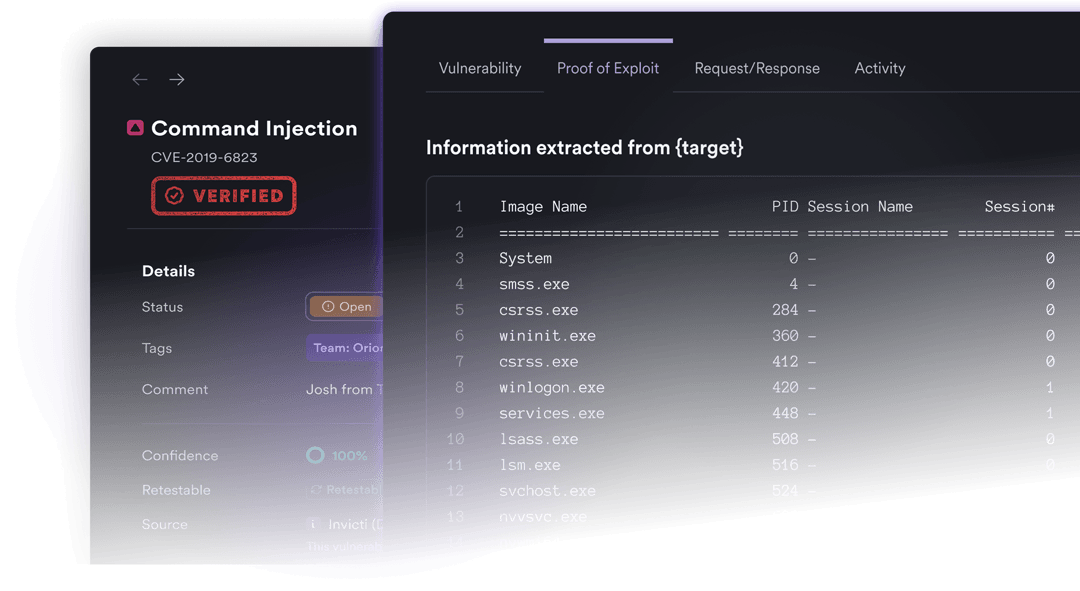
Proof-based scanning
Automatically confirm many exploitable vulnerabilities.

Agentic pentesting
DAST-grounded AI agents investigate application weaknesses and produce evidence-backed findings.

Advanced crawling
Reach complex, JavaScript-heavy, and deeply linked application areas.

SAST + DAST correlation
Connect runtime-verified vulnerabilities to the relevant source code and owner.

API security testing
Discover and test APIs along with websites and web apps.

Authenticated scanning
Test protected workflows, roles, and user states.

Out-of-band detection
Identify vulnerabilities that do not produce an immediate in-band response.

Multi-layer API discovery
Find APIs across source code, traffic, gateways, and scanning for better test coverage.

CI/CD integrations
Run security testing inside software delivery pipelines.

Runtime-to-code context
Help developers locate, understand, and remediate vulnerabilities faster.

Compliance reporting
Support governance, audit, and regulatory requirements.

Continuous scanning
Keep coverage current as applications and APIs change.

Automated fix retesting
Verify remediation and reopen findings that remain unresolved.

Issue-tracking automation
Route validated findings to the correct owner.

Application security posture management
Correlate findings, prioritize application risk, and track remediation across teams.
Compare Invicti and Tenable Nessus for your application environment
Industry
highlights


