Find risk. Prove what matters. Fix it faster.
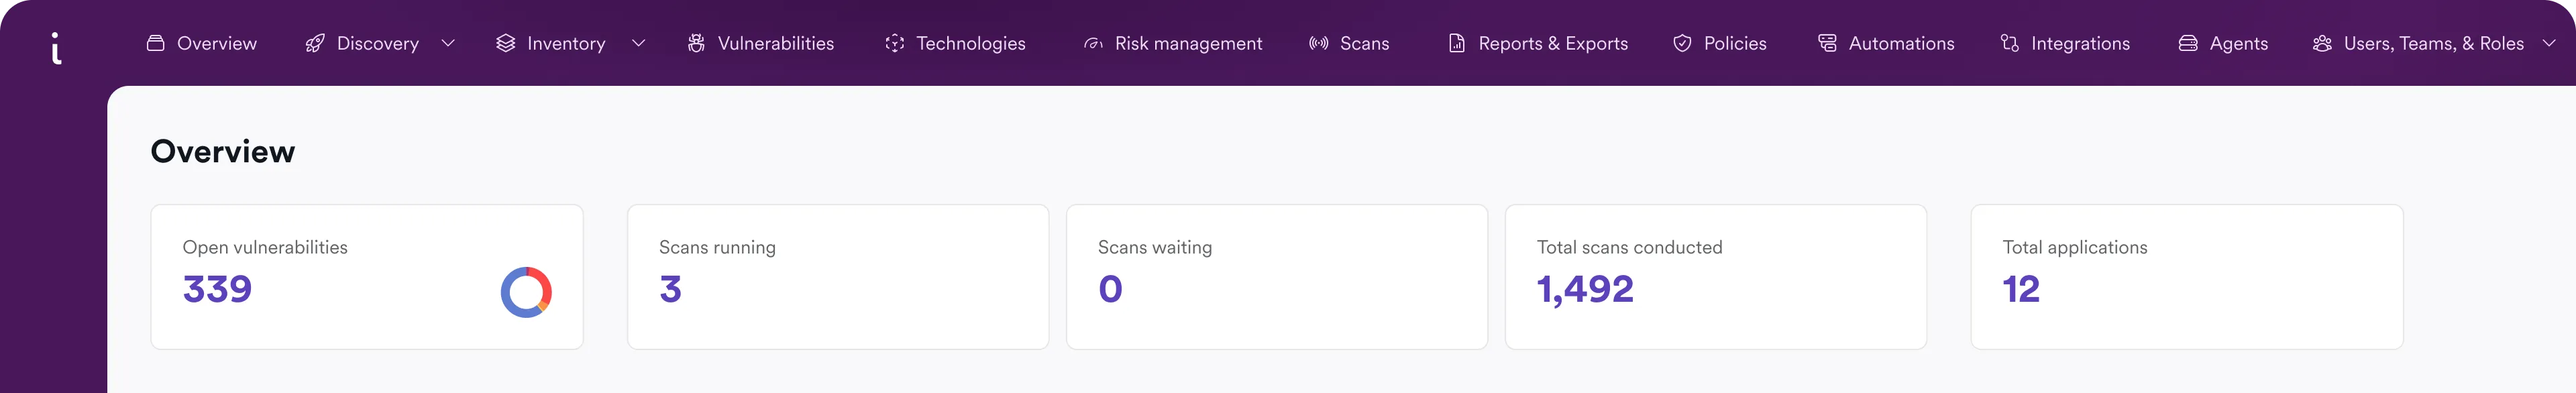
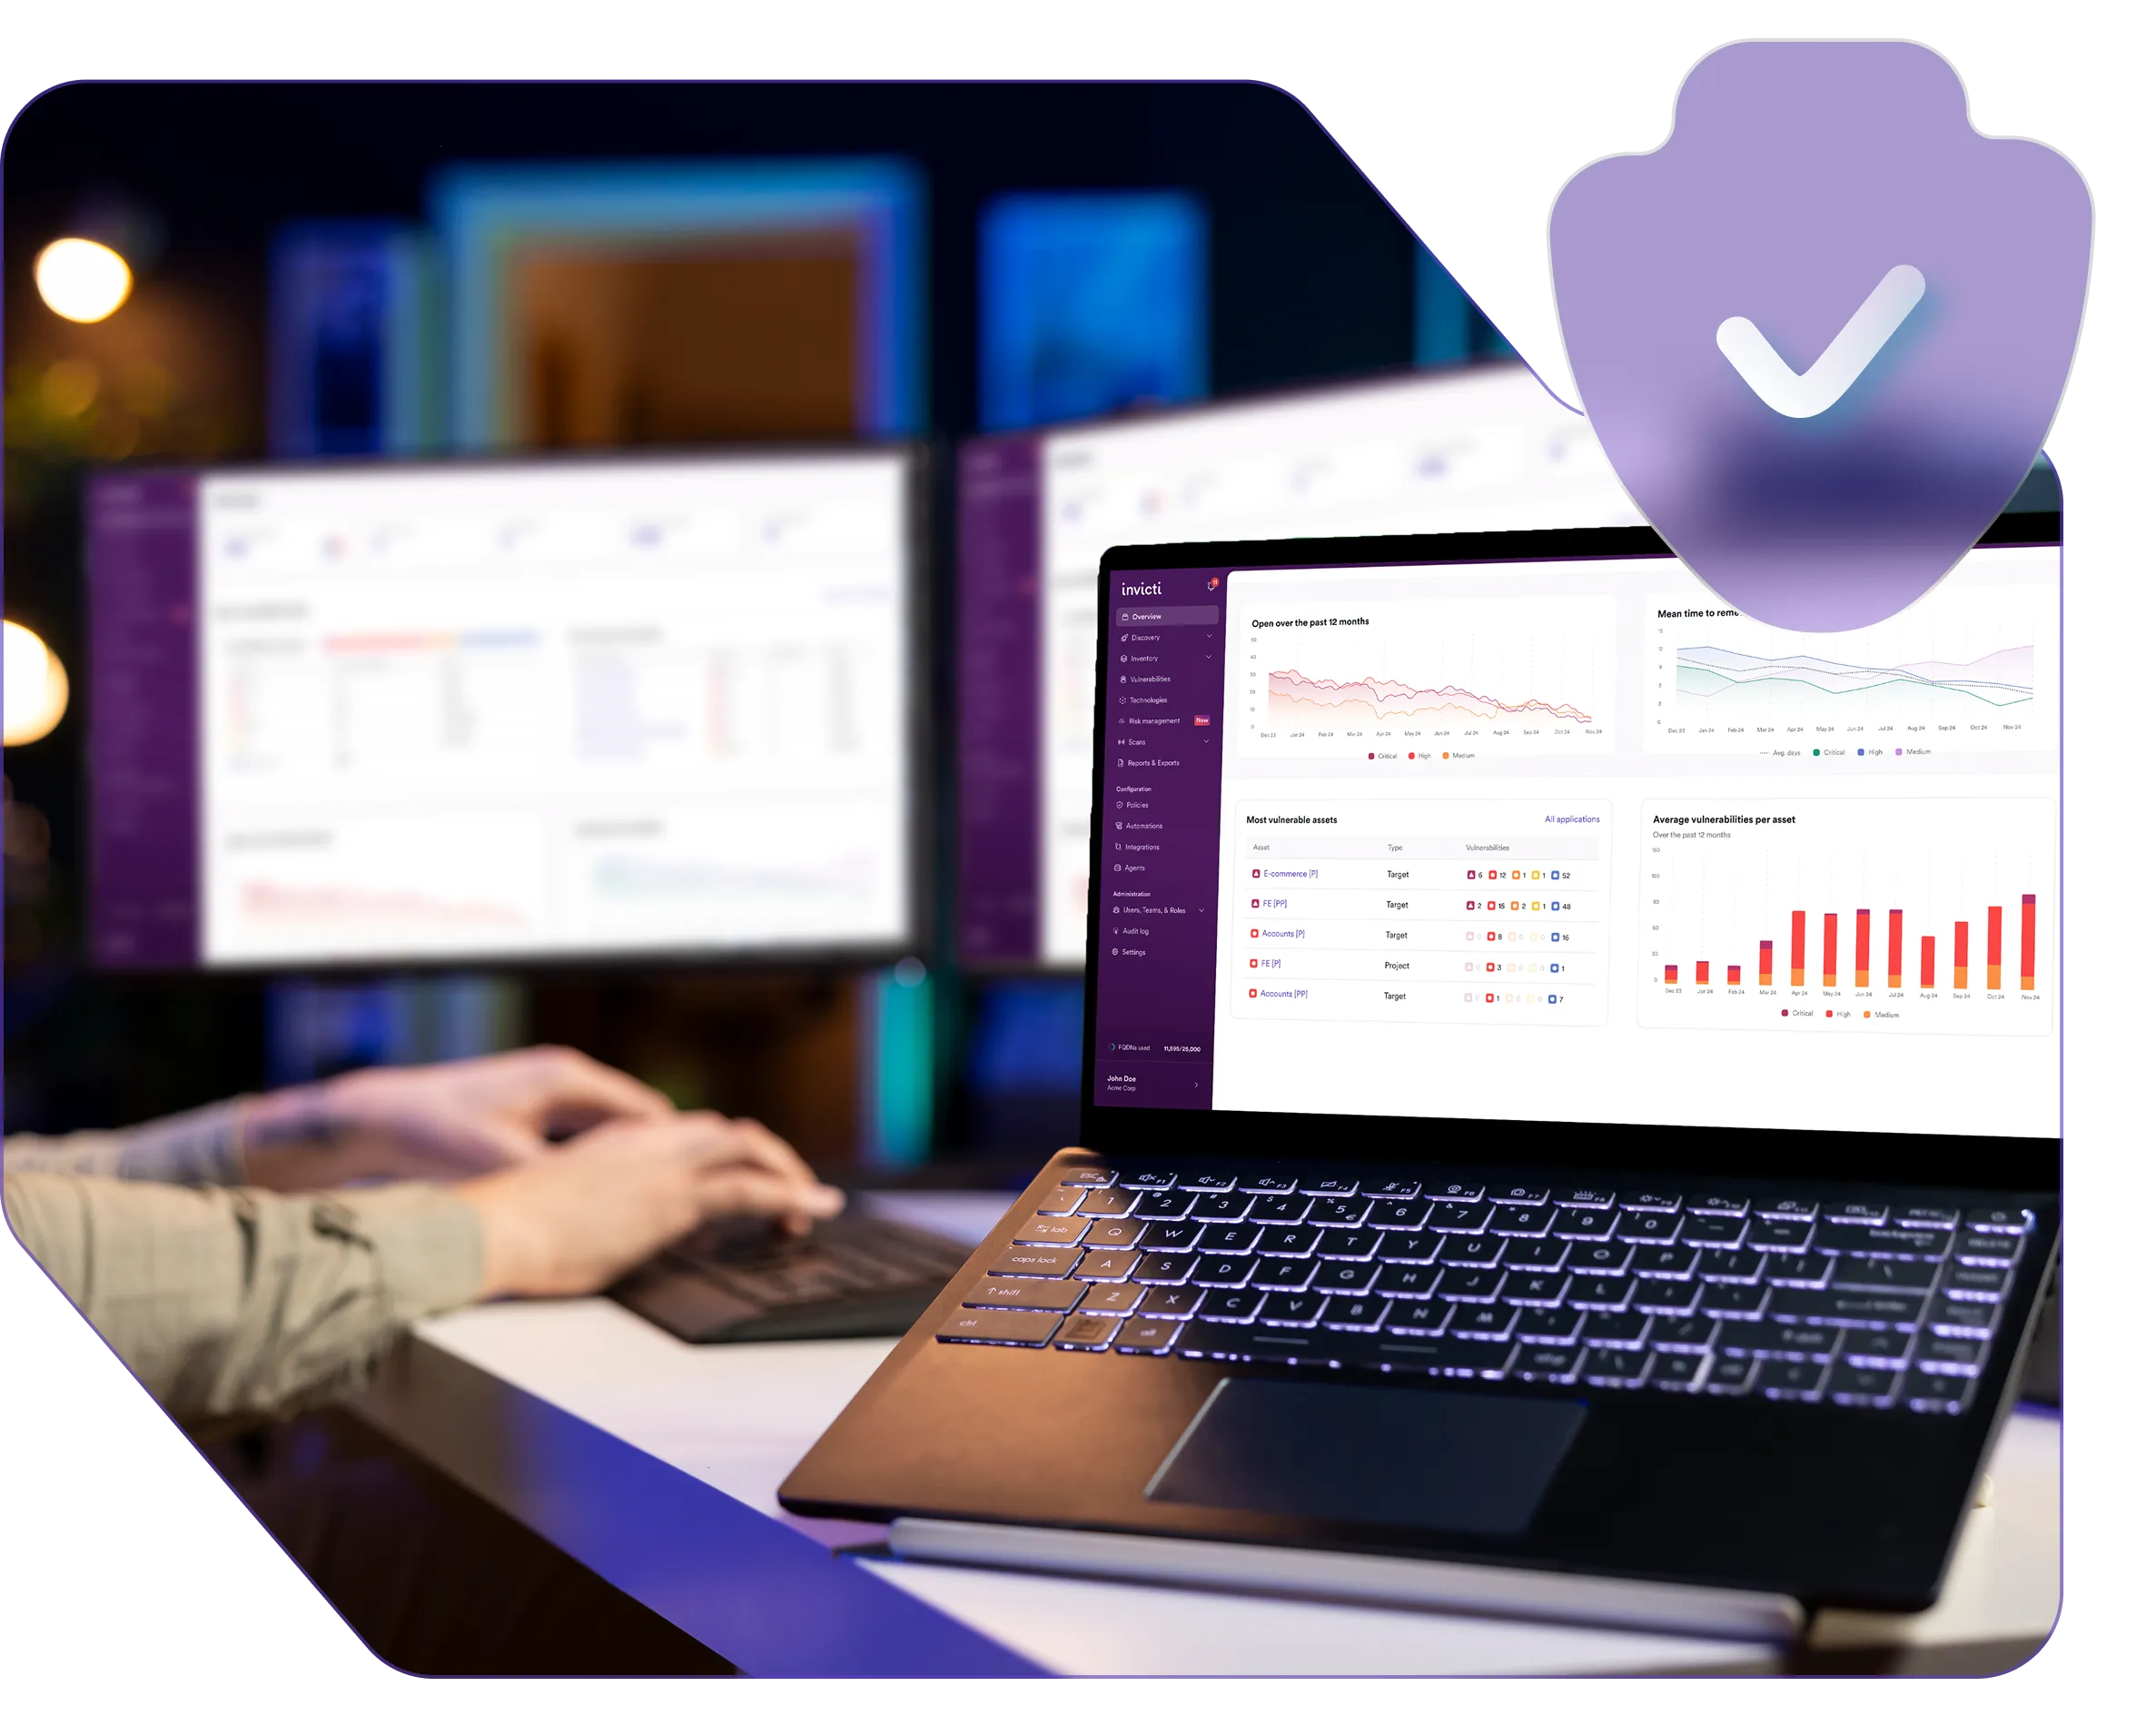
Invicti consolidates security findings into a single view and applies runtime reachability, exploitability, and business context to prioritize the risks that matter.
Complete AppSec in one platform. Use runtime intelligence to identify real, exploitable risk and help developers fix what matters faster.


Every scanner floods you with alerts. Without runtime prioritization, hours are wasted chasing false positives.
Manual triage and fragmented tools make it impossible to keep up with rapid release cycles.
Teams lack visibility into who owns critical vulnerabilities, remediation timelines, and whether fixes actually worked.
Invicti consolidates security findings into a single view and applies runtime reachability, exploitability, and business context to prioritize the risks that matter.


Lorem ipsum dolor sit amet consectetur. Arcu ornare est dui est congue gravida eget euismod mi.
“For more websites, we now don’t need to go externally for security testing. We can fire up Invicti, run the tests as often as we like, view the scan results, and mitigate to our hearts’ content. As a result, the budget we were spending every year on penetration testing decreased by approximately 60% almost immediately and went down even more the following year, to about 20% of our initial spending.”
“Invicti detected web vulnerabilities that other solutions did not. It is easy to use and set up...”

“I had the opportunity to compare expertise reports with Invicti ones. Invicti was better, finding more breaches.”

“Invicti is the best Web Application Security Scanner in terms of price-benefit balance. It is a very stable software, faster than the previous tool we were using and it is relatively free of false positives, which is exactly what we were looking for.”
The Invicti Platform takes a DAST-first approach to application security, focusing on exploitable vulnerabilities in live applications rather than theoretical risks. Unlike static testing tools that generate excessive false positives, Invicti uses proof-based scanning to automatically validate vulnerabilities with proof-of-exploit, eliminating guesswork and wasted effort.
False positives are one of the biggest challenges in application security. For many common vulnerability classes, Invicti addresses this with proof-based scanning, which automatically verifies whether a vulnerability is truly exploitable. This reduces alert fatigue and ensures development teams only spend time fixing real, high-risk issues.
Application security posture management (ASPM) provides centralized visibility and risk management across security tools, workflows, and teams. Invicti delivers the industry’s first proof-based ASPM by combining its leading DAST and API security with orchestration and management capabilities. This enables enterprises to prioritize, track, and remediate vulnerabilities across all applications with zero noise.
Yes. Invicti goes beyond web application scanning to include automated API discovery and testing. This helps organizations cover hidden parts of their attack surface, ensuring both web applications and APIs are continuously identified and secured against real-world threats.
Absolutely. The Invicti Platform is built for automation and scalability, with integrations into CI/CD pipelines, issue trackers, and collaboration tools. This allows security testing to run continuously in DevSecOps environments without slowing down development, ensuring vulnerabilities are detected and remediated early.
Yes. The Invicti Platform includes software composition analysis (SCA) and container security capabilities, allowing organizations to identify vulnerable open-source libraries, outdated technologies, and insecure container images. Combined with dynamic testing, this provides both static and runtime visibility into supply chain risks for a more complete security posture.