Invicti for Engineering Managers
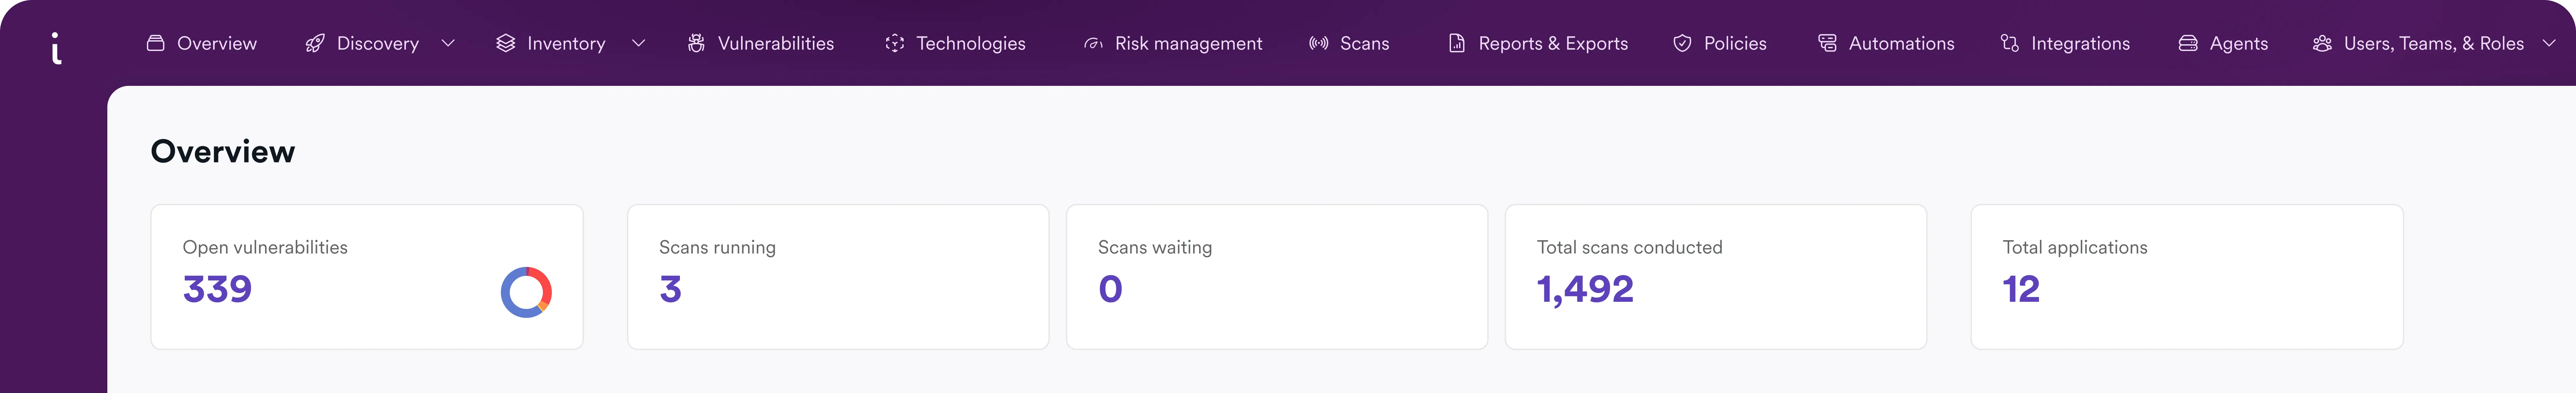
Invicti is a scalable, multi-user web application security solution with built-in workflow and reporting tools ideal for security teams. It’s available as a hosted and self-hosted solution and can be fully integrated in any development or testing environment.
Más de 5000 organizaciones líderes confían en Invicti


Initial Vulnerability Assessment
Invicti makes it easy for you to decide, which bugs need to be prioritized by your engineering teams. Its built-in vulnerability assessment functionality and issue tracker integration make it possible to automatically create issues with suitable severity settings and assign them to appropriate resources. All you need to do is monitor and tweak if necessary.

Supporting the Engineers
Because Invicti generates proof of exploit for every confirmed vulnerability it finds, an engineer can easily reproduce the bug and quickly find the solution. Thanks to this technology, engineers never need to waste time trying to fix something that does not need to be fixed at all.

Early Vulnerability Elimination
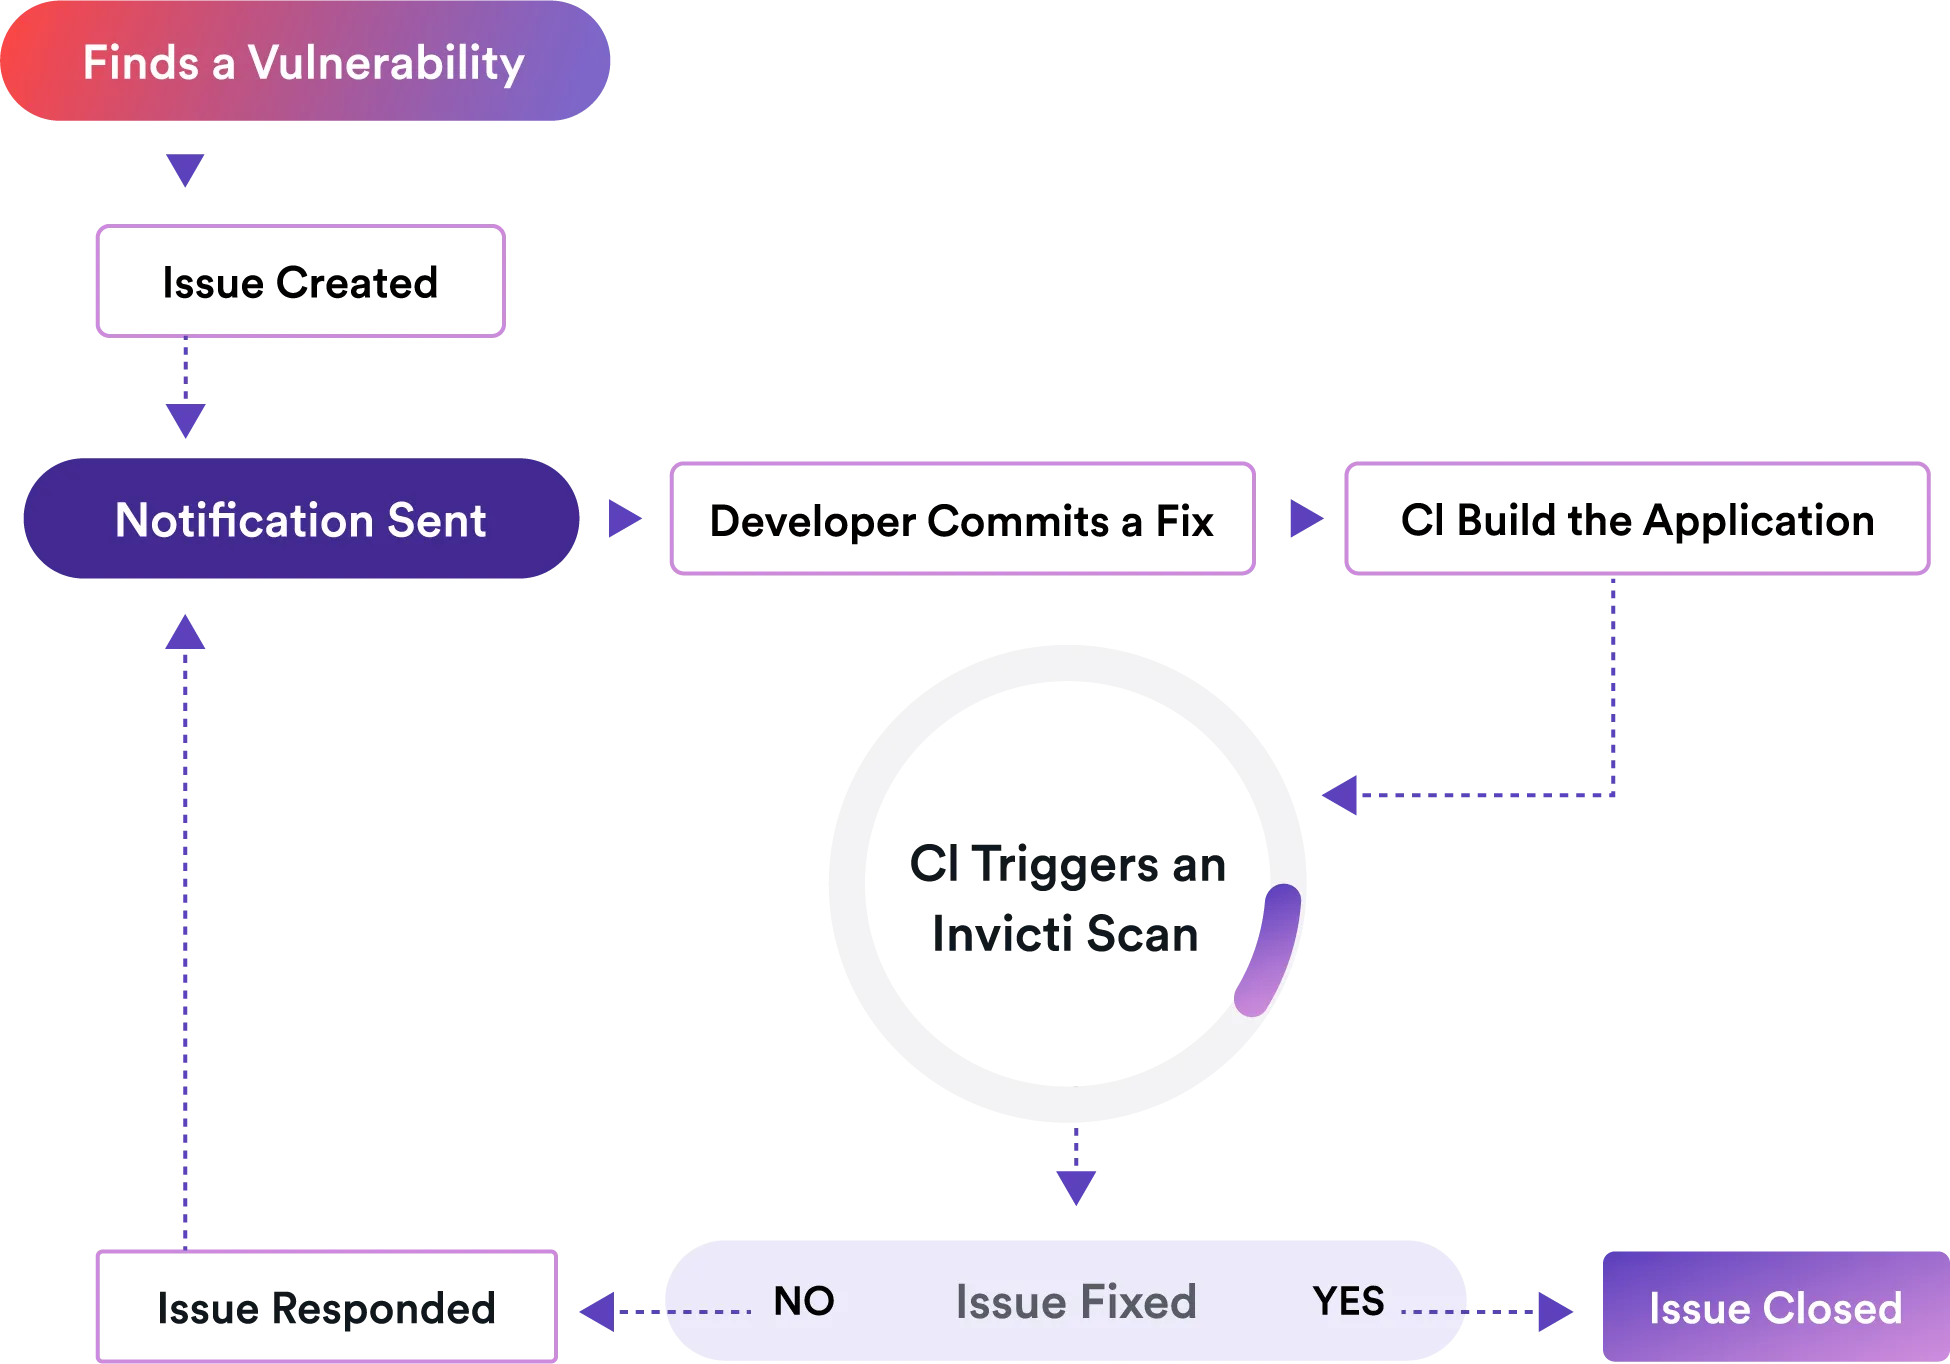
If a vulnerability makes it to a production system, its cost greatly increases. To resolve the issue, the software needs to go through the entire production cycle again. This consumes your valuable engineering time and resources. Invicti can be integrated into workflows so that every commit is automatically scanned. This way, the original engineer can immediately correct their mistake and no vulnerability makes it out of the development stage.
Lo que dicen nuestros clientes
"Para más sitios web, ya no necesitamos recurrir a servicios externos para las pruebas de seguridad. Podemos iniciar Invicti, ejecutar las pruebas tantas veces como queramos, ver los resultados del escaneo y aplicar las correcciones que necesitemos. Como resultado, el presupuesto que gastábamos cada año en test de penetración disminuyó aproximadamente un 60% casi de inmediato y se redujo aún más al año siguiente, hasta cerca del 20% de nuestro gasto inicial".
"Invicti detectó vulnerabilidades web que otras soluciones no encontraron. Es fácil de usar y configurar..."

"Tuve la oportunidad de comparar informes de expertos con los de Invicti. Invicti fue mejor, encontrando más brechas".

"Invicti es el mejor escáner de seguridad de aplicaciones web en términos de relación coste-beneficio. Es un software muy estable, más rápido que la herramienta que utilizábamos anteriormente y está relativamente libre de falso positivo, que es exactamente lo que buscábamos".
Featured Engineering Managers Content

Getting developers on board to transition from part of the problem to part of the process
7 principles of secure design in software development security
Secure software development: Building better software with secure practices
Save your security team hundreds of hours with Invicti’s web security scanner.