
Application security for security operations
Take control of offensive application security
Continuously test applications and APIs, validate exploitable vulnerabilities, and drive remediation with actionable evidence. Give your security team greater control without making development pipelines a prerequisite.
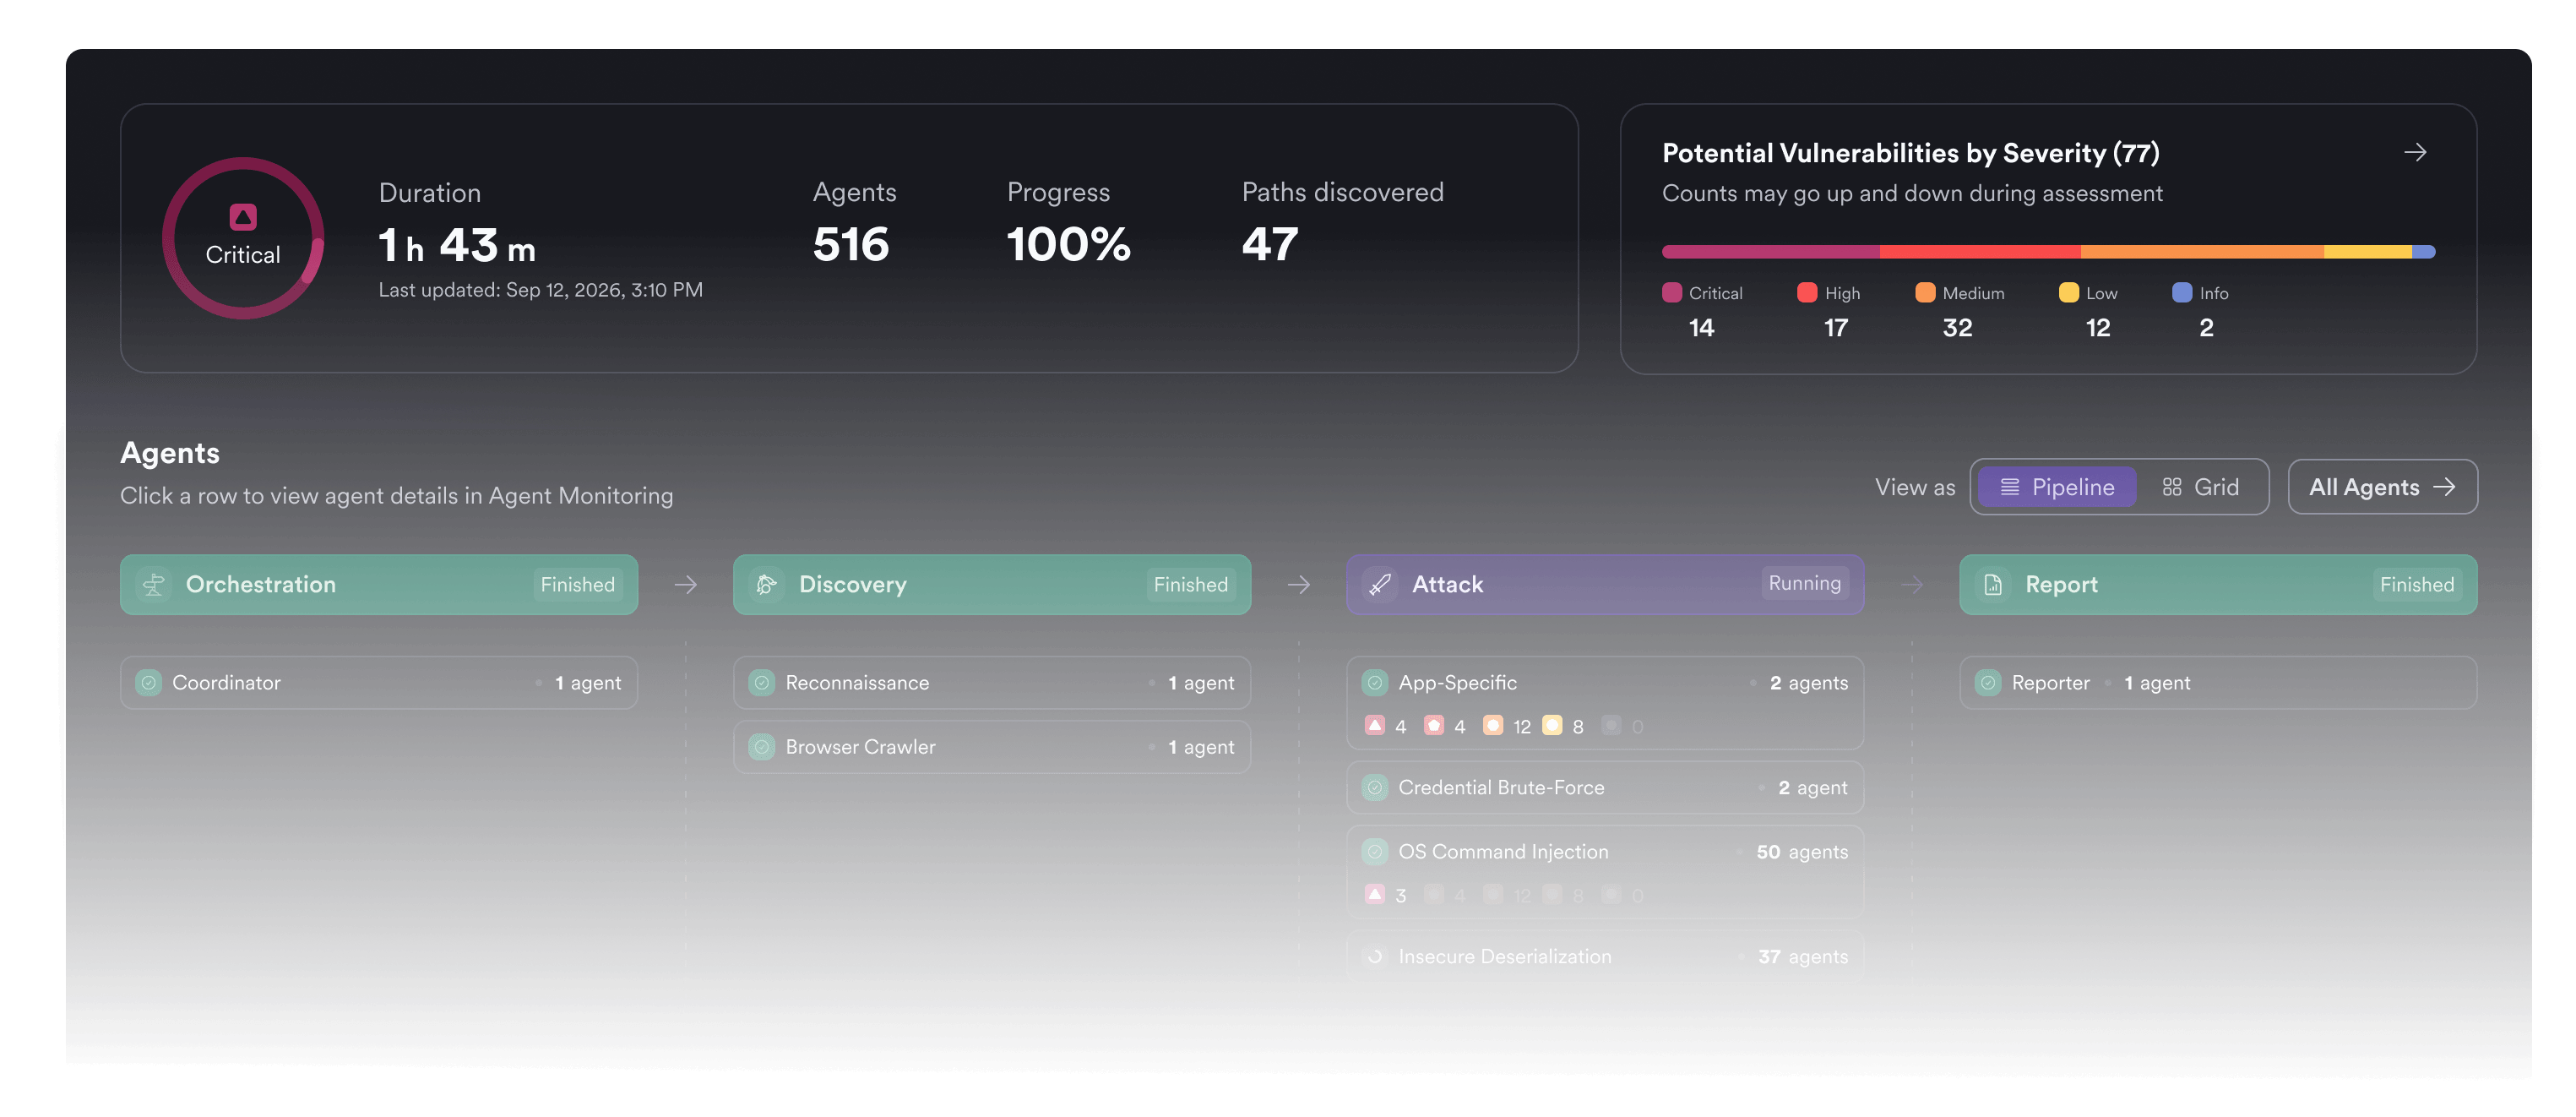


Better visibility
Know where application risk exists.

Smarter priorities
Focus on proven, high-impact threats.

Measurable progress
Track and demonstrate risk reduction.
Más de 5000 organizaciones líderes confían en Invicti




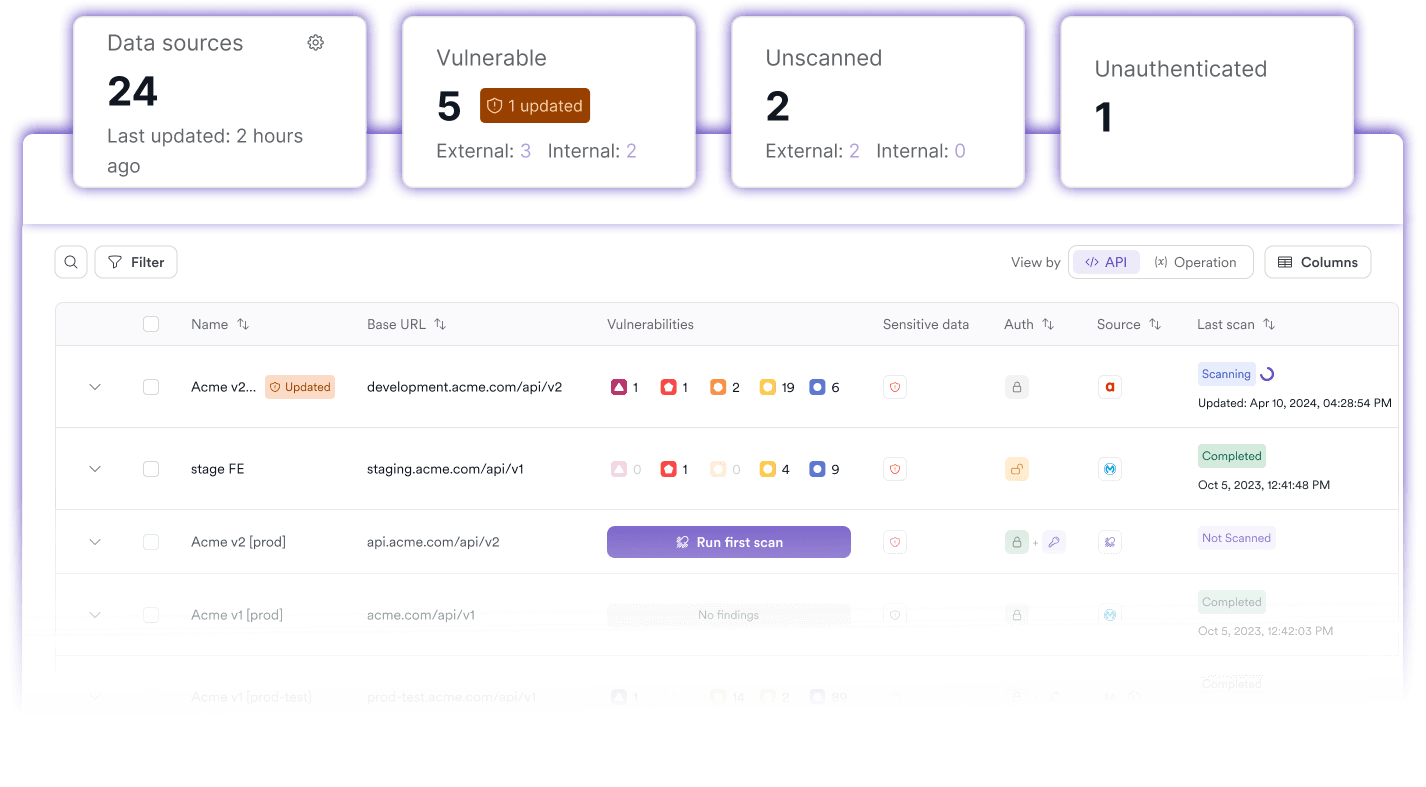
Find exposed applications and hidden APIs
Identify application and API assets that may be missing from your security inventory. Combine web scanning with API discovery across supported sources to bring more of your attack surface into testing.
Test more applications with less manual work
Schedule DAST scans and run agentic pentesting to assess applications and APIs more frequently. Automate repetitive assessments while retaining control over testing scope and timing.
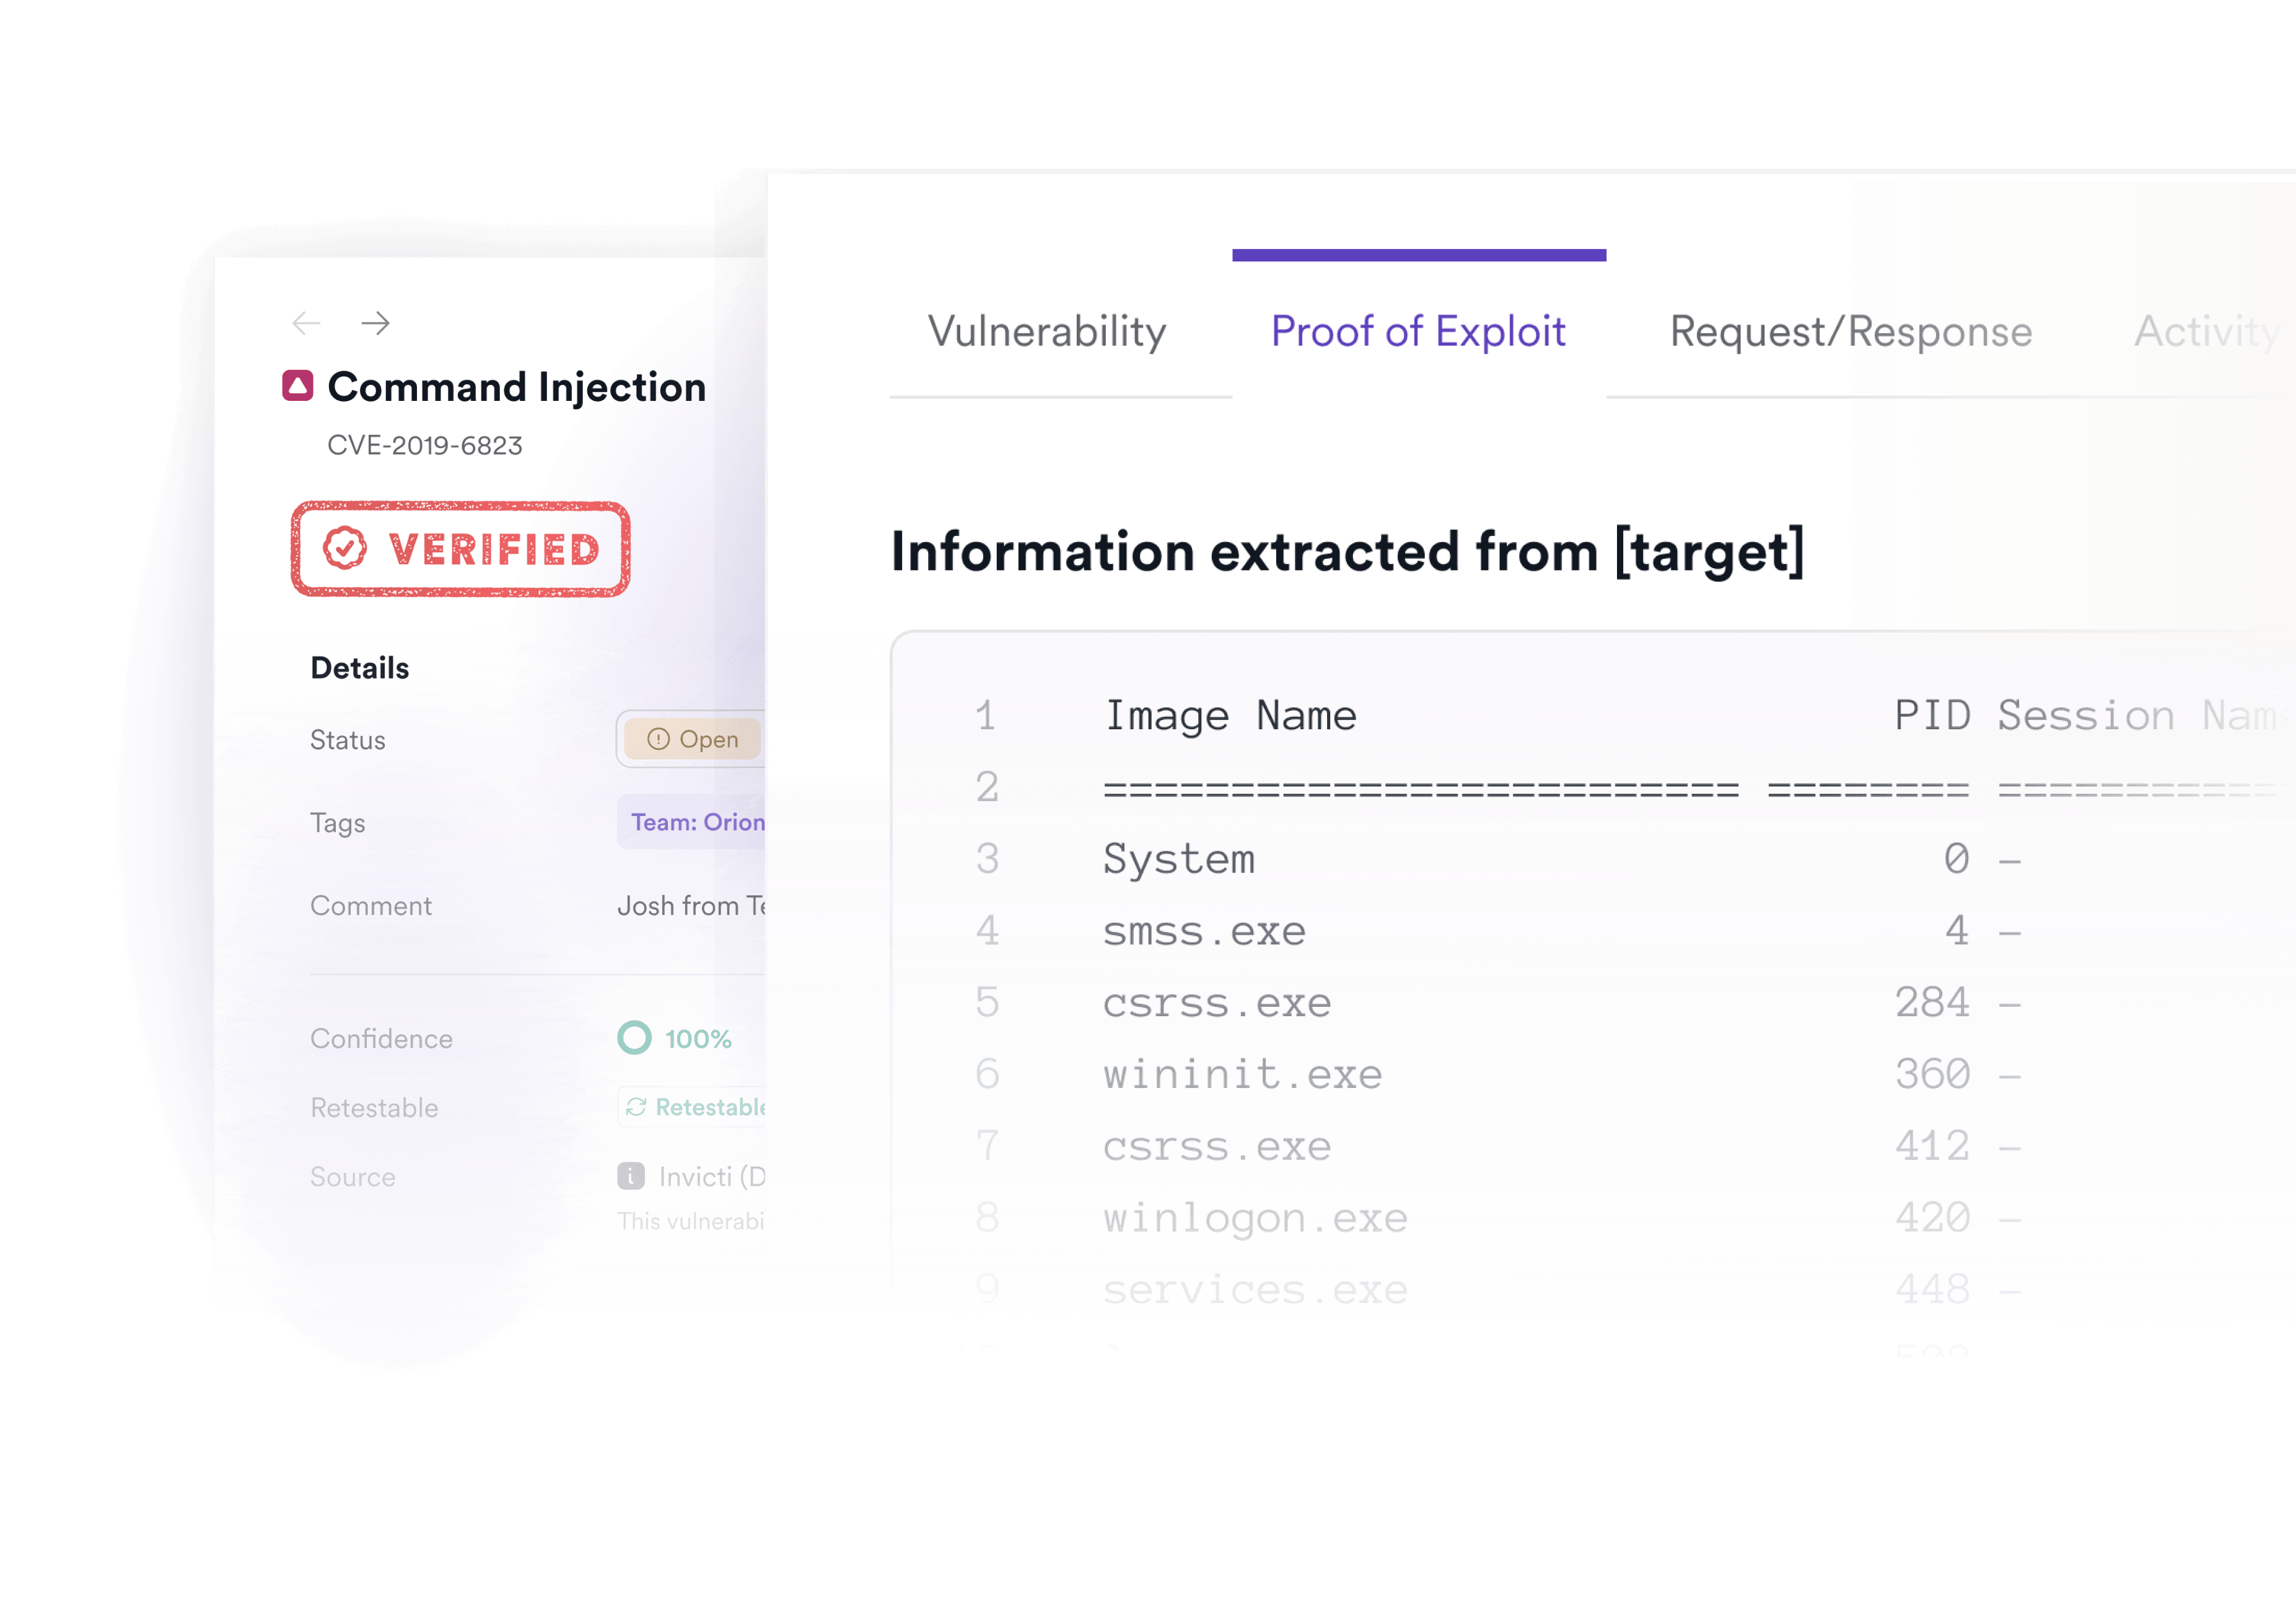
Know which vulnerabilities are real
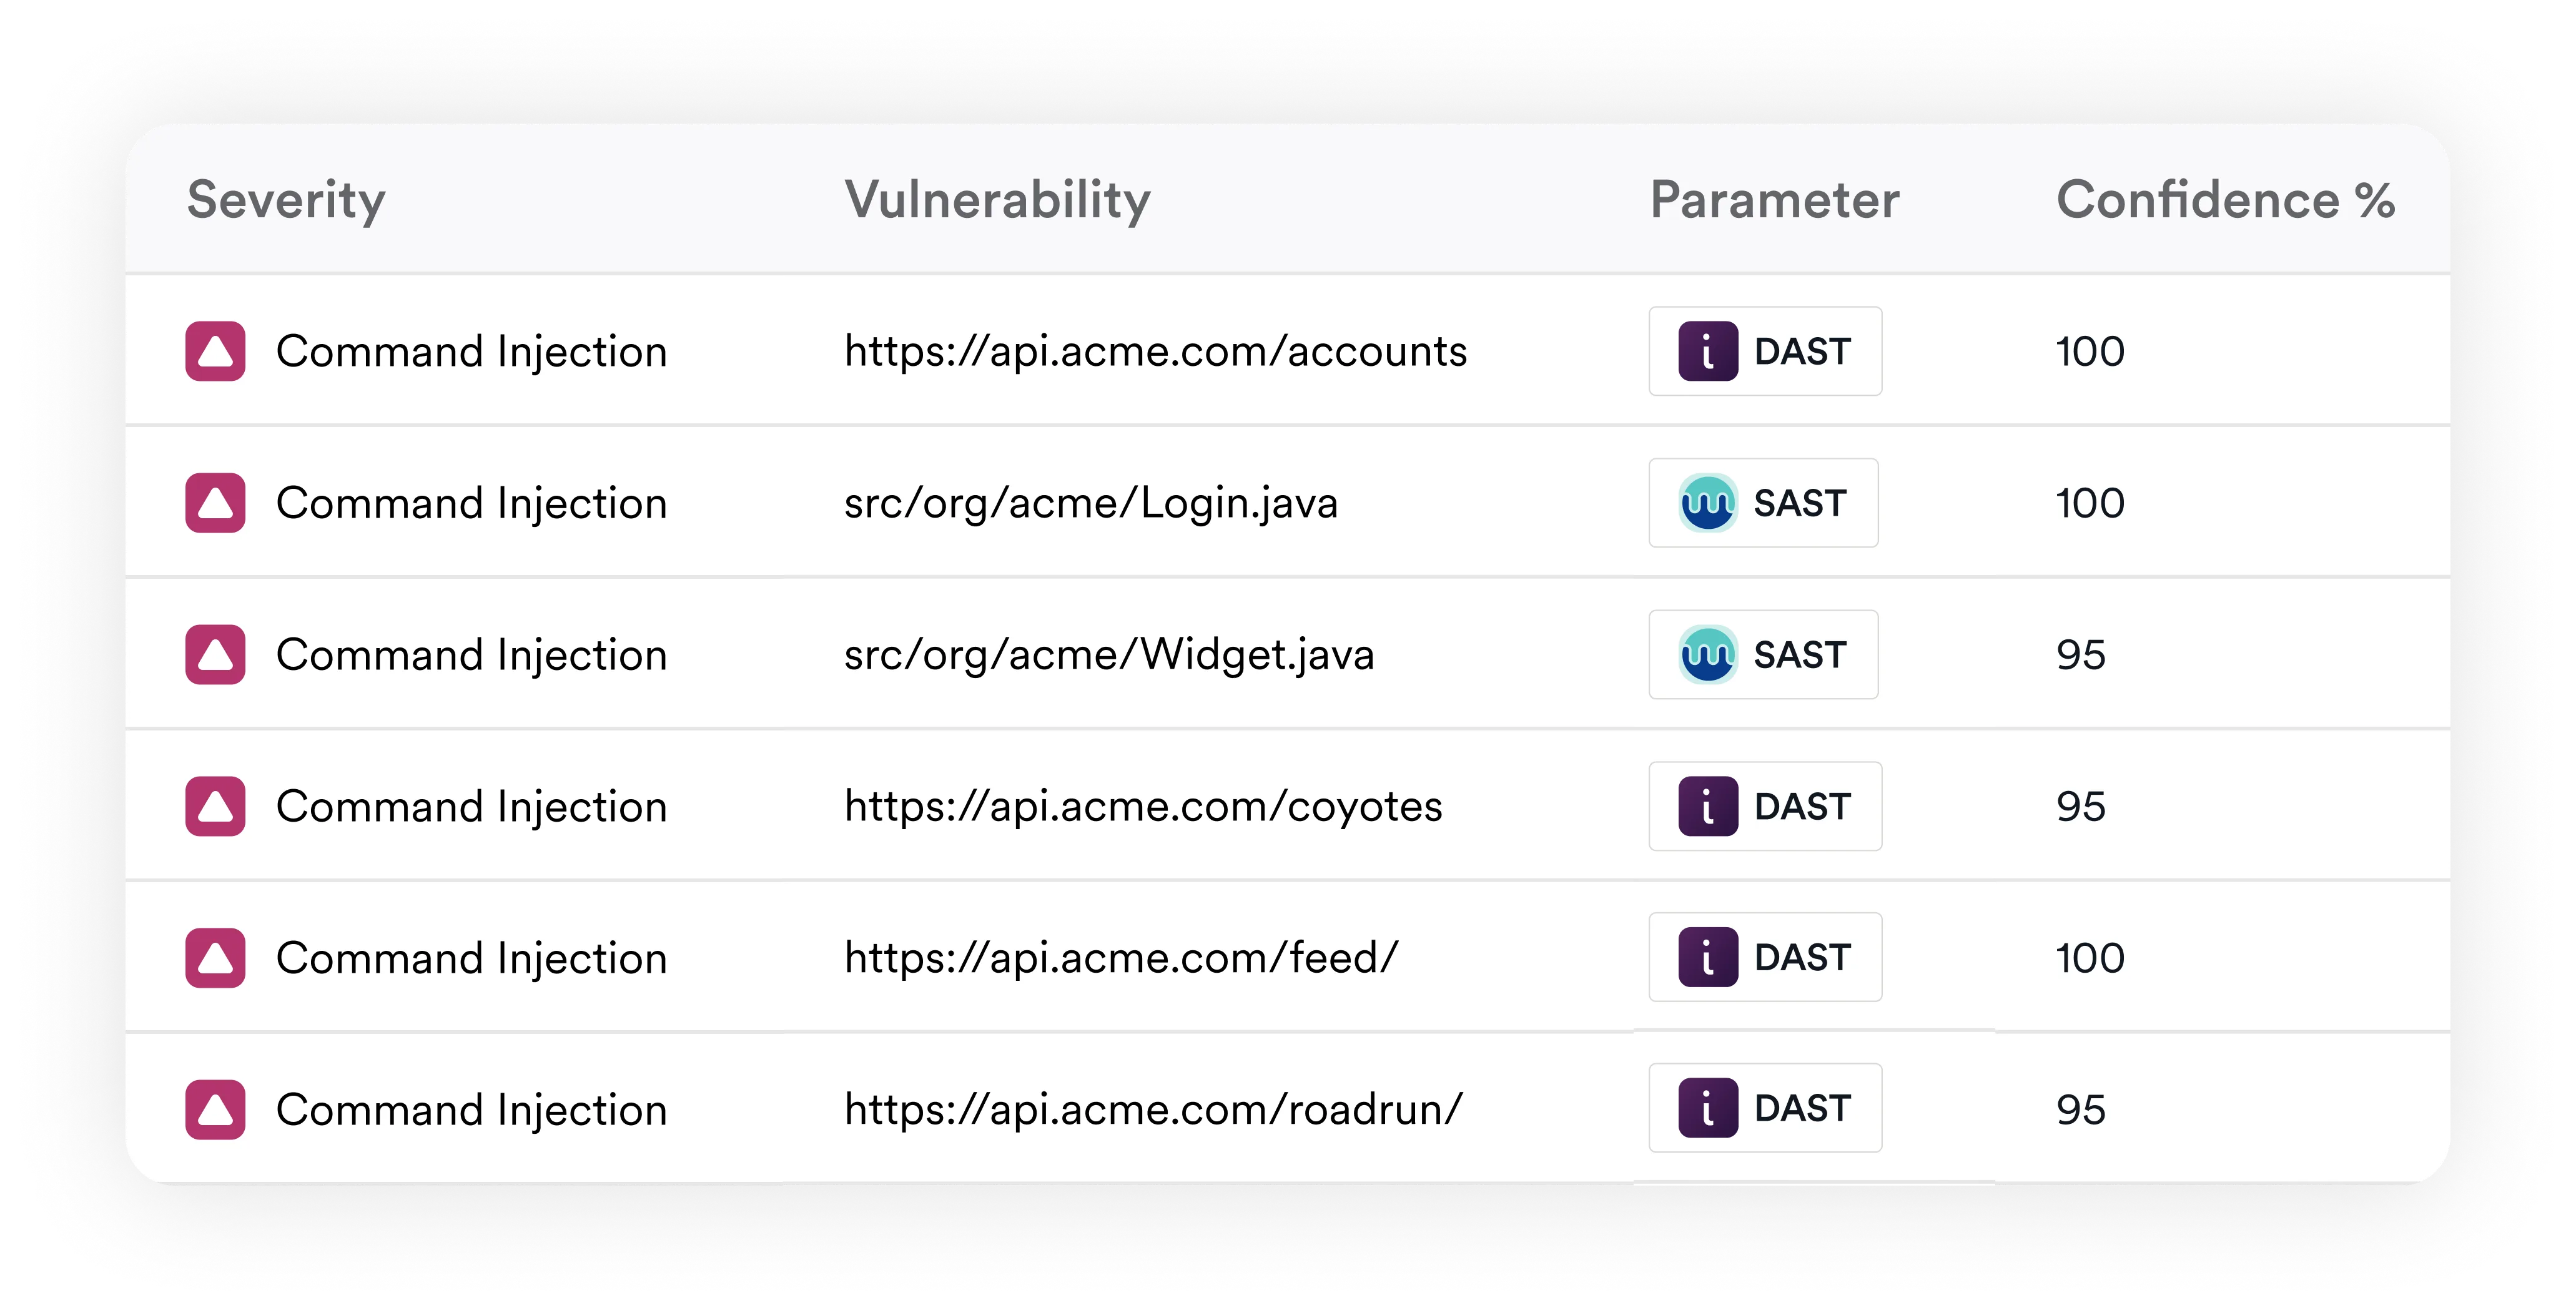
Use proof-based scanning to automatically verify supported vulnerabilities in running applications. Get technical evidence that reduces manual investigation and helps your team act with confidence.
Turn findings into fixes
Route actionable findings to the right teams, provide reproducible evidence, and automatically retest supported issues to confirm remediation. Keep security operations moving without unnecessary back-and-forth.
Find exposed applications and hidden APIs
Identify application and API assets that may be missing from your security inventory. Combine web scanning with API discovery across supported sources to bring more of your attack surface into testing.
Test more applications with less manual work
Schedule DAST scans and run agentic pentesting to assess applications and APIs more frequently. Automate repetitive assessments while retaining control over testing scope and timing.
Know which vulnerabilities are real
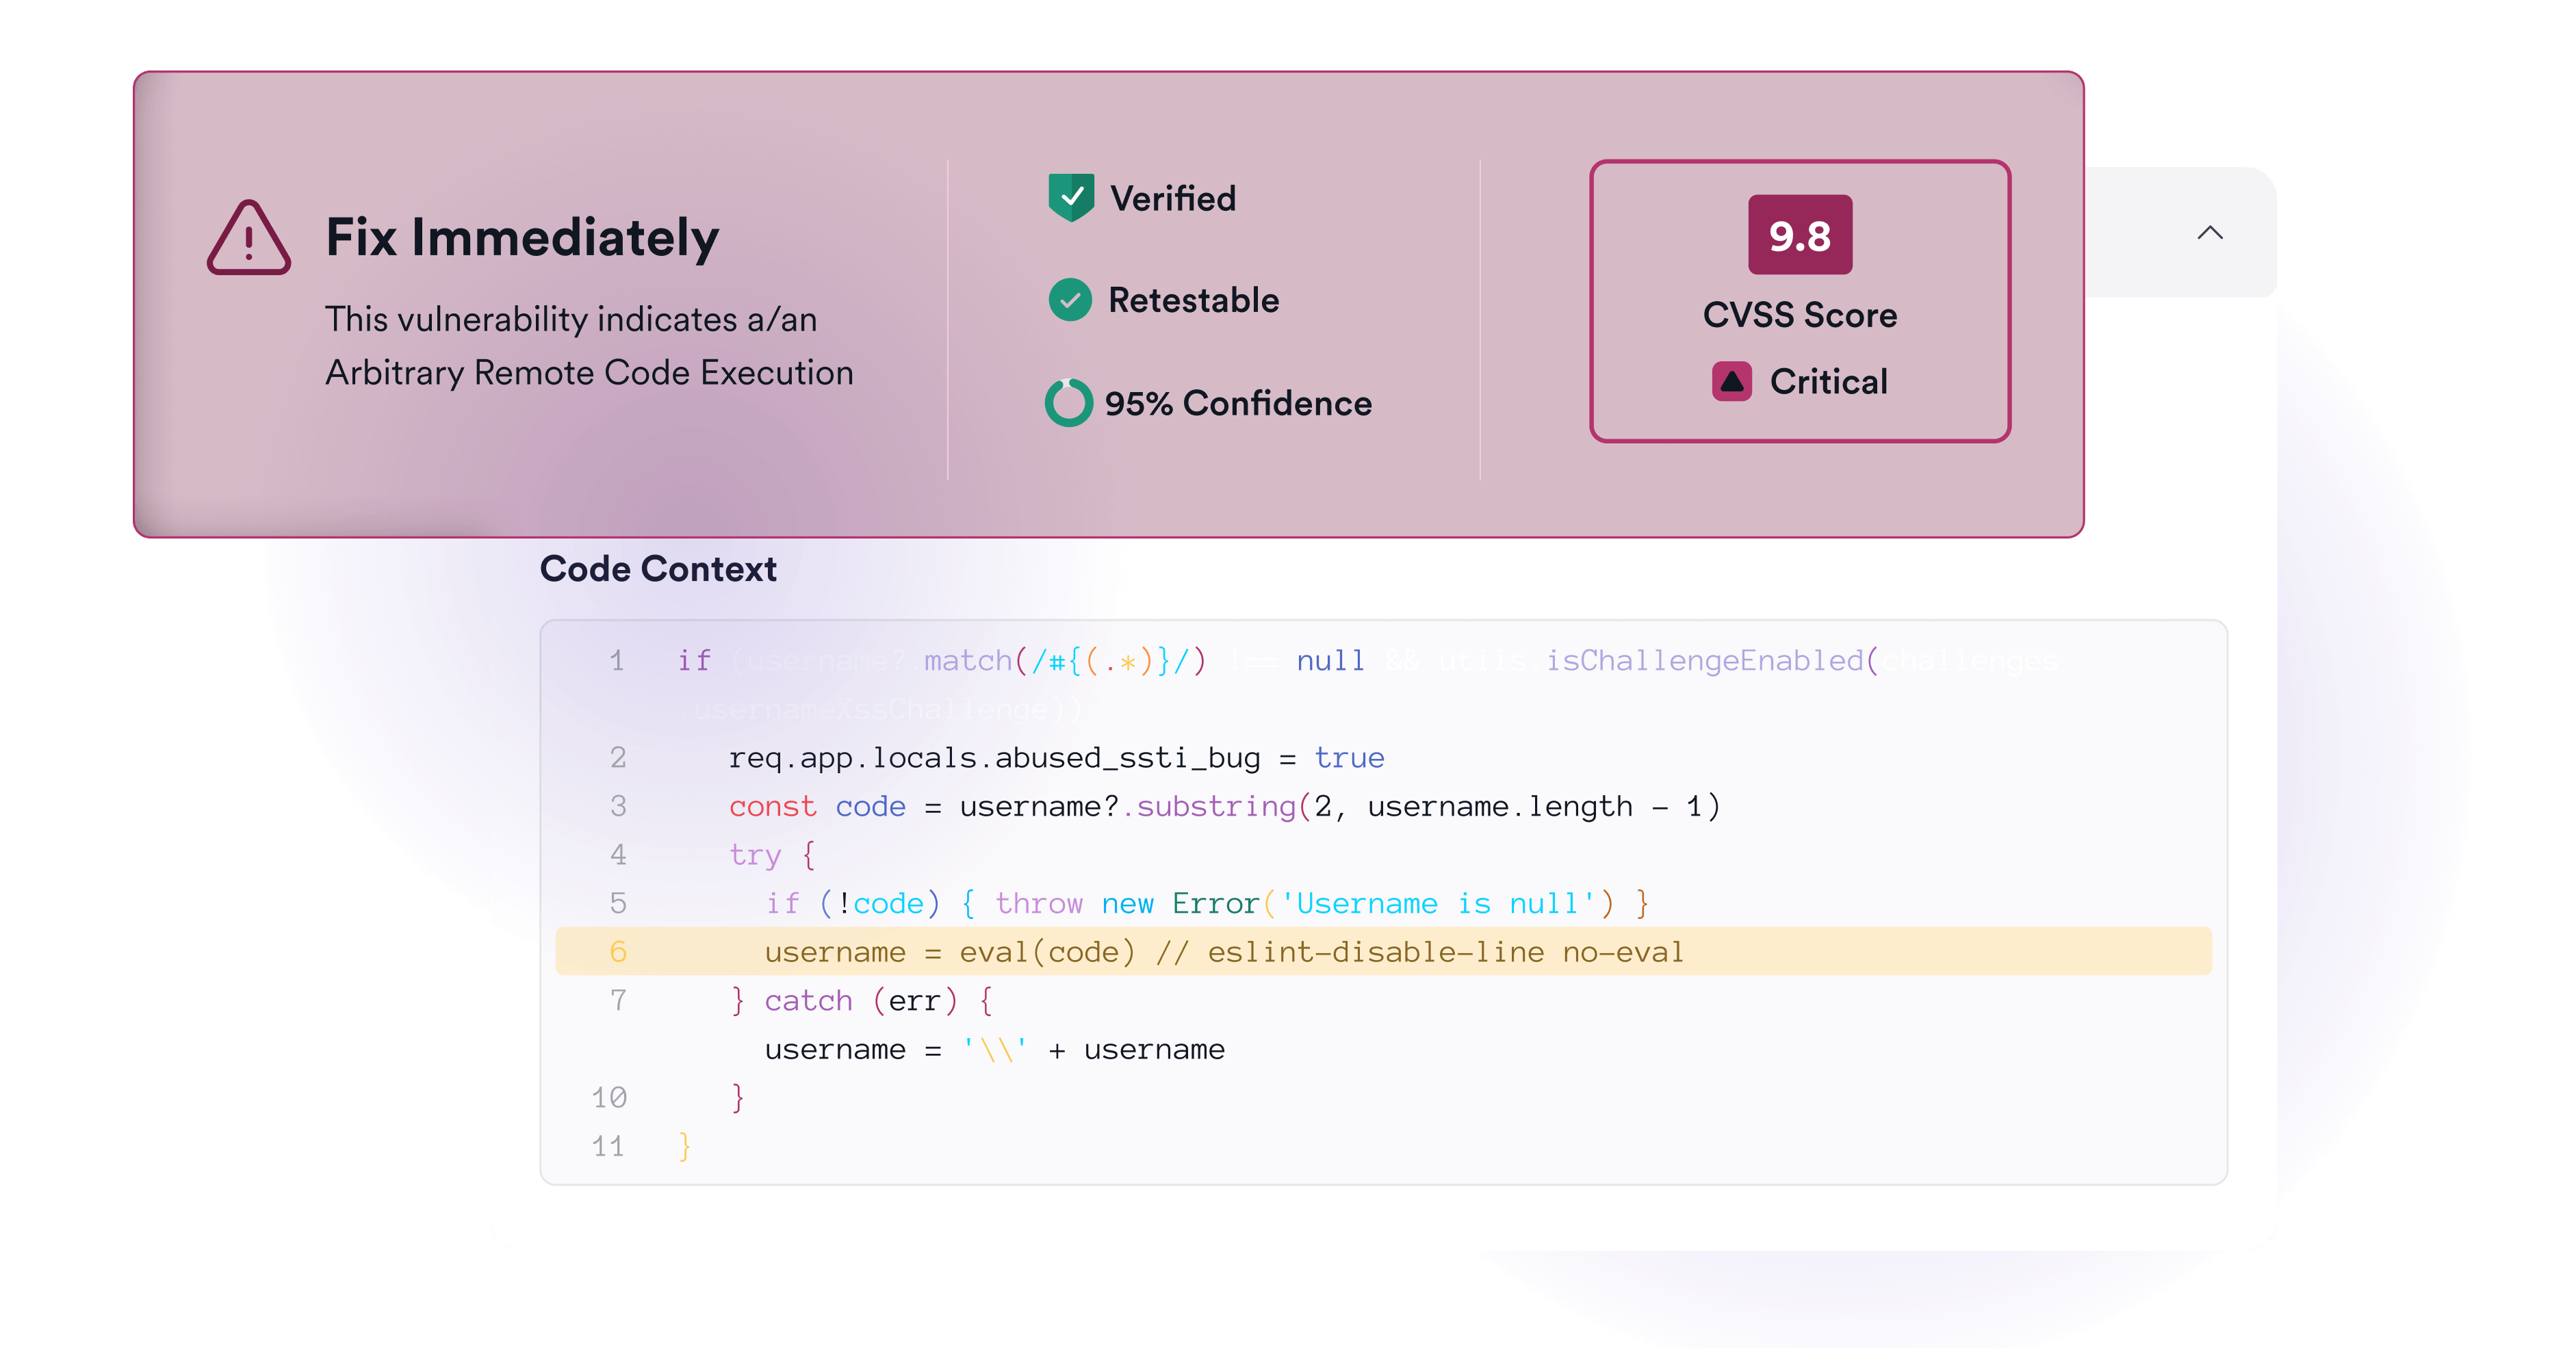
Use proof-based scanning to automatically verify supported vulnerabilities in running applications. Get technical evidence that reduces manual investigation and helps your team act with confidence.
Turn findings into fixes
Route actionable findings to the right teams, provide reproducible evidence, and automatically retest supported issues to confirm remediation. Keep security operations moving without unnecessary back-and-forth.

“We can fire up Invicti, run the tests as often as we like, and mitigate to our hearts’ content. The budget we were spending every year on penetration testing decreased by approximately 60% almost immediately …

“As opposed to other web application scanners we used, Invicti is very easy to use and does not require a lot of configuring. An out of the…

“Start integrating Invicti into your process and you’ll be surprised at how much time it saves you and how much ‘auto magic’ it brings to your entire development pipeline …

Offensive testing backed by application intelligence
Invicti combines DAST, agentic pentesting, API discovery, and source-code intelligence to help security teams find and validate application risk. ASPM connects testing results to prioritization, remediation workflows, and fix verification.
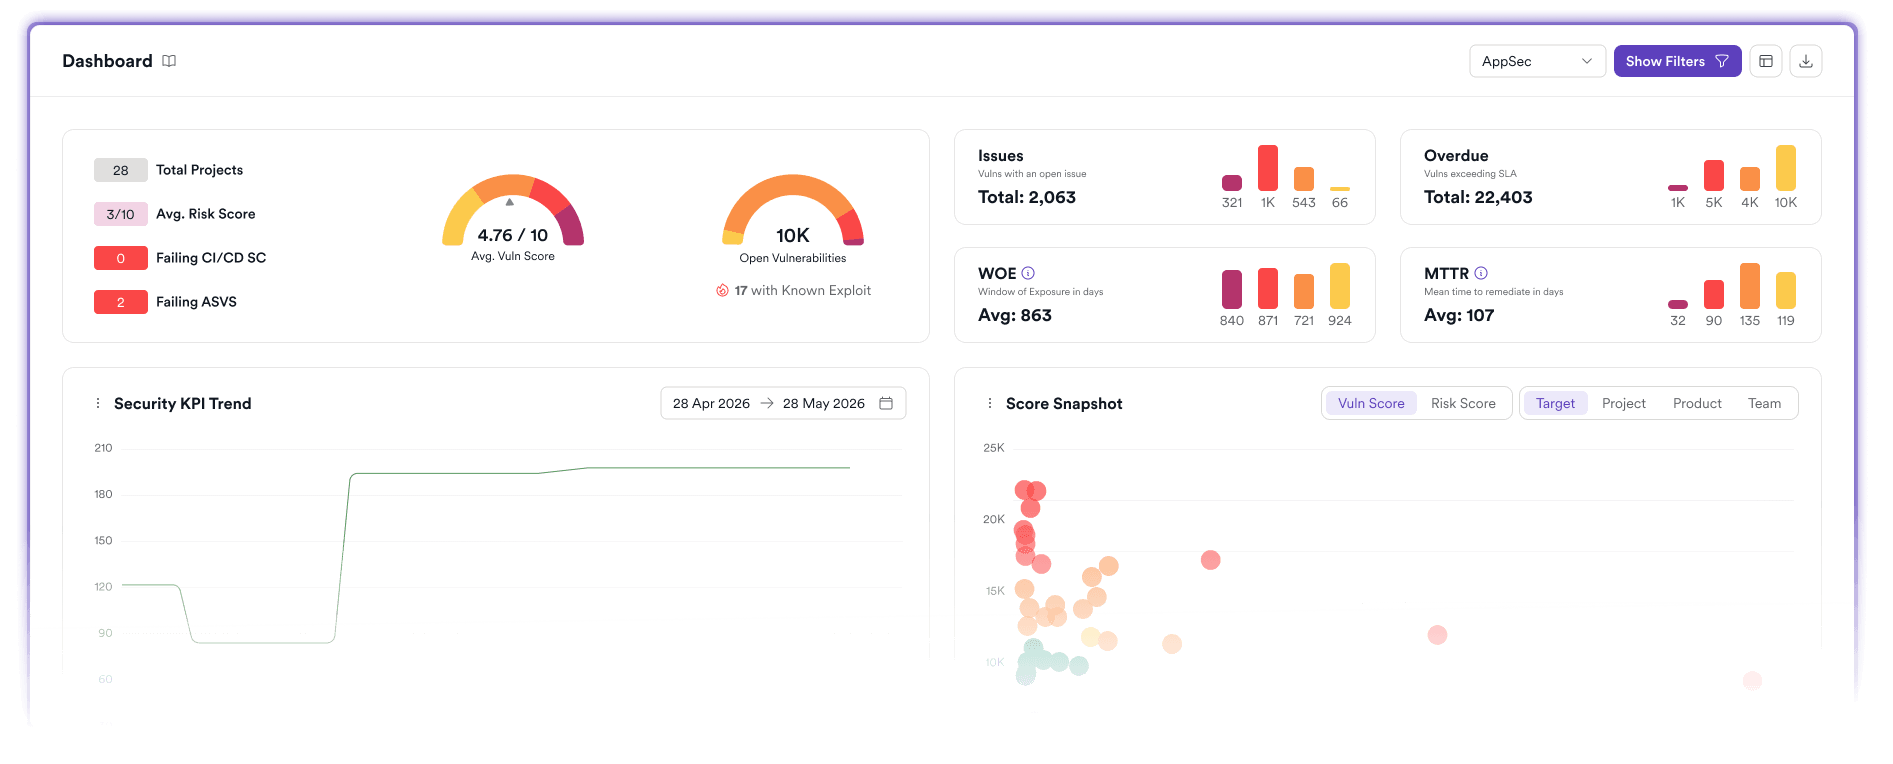
BUILT FOR SECURITY OPERATIONS
Security with more control and less manual effort

Own your testing schedule
Run scheduled and on-demand assessments without making CI/CD integration a prerequisite. Keep security testing under your team's control.

Expand offensive testing capacity
Combine automated DAST with agentic pentesting to assess more applications and APIs without proportionally increasing manual testing effort.

Uncover hidden attack surfaces
Discover applications and undocumented APIs that may otherwise escape security testing. Bring newly identified assets into your assessment workflows.

Reduce manual verification
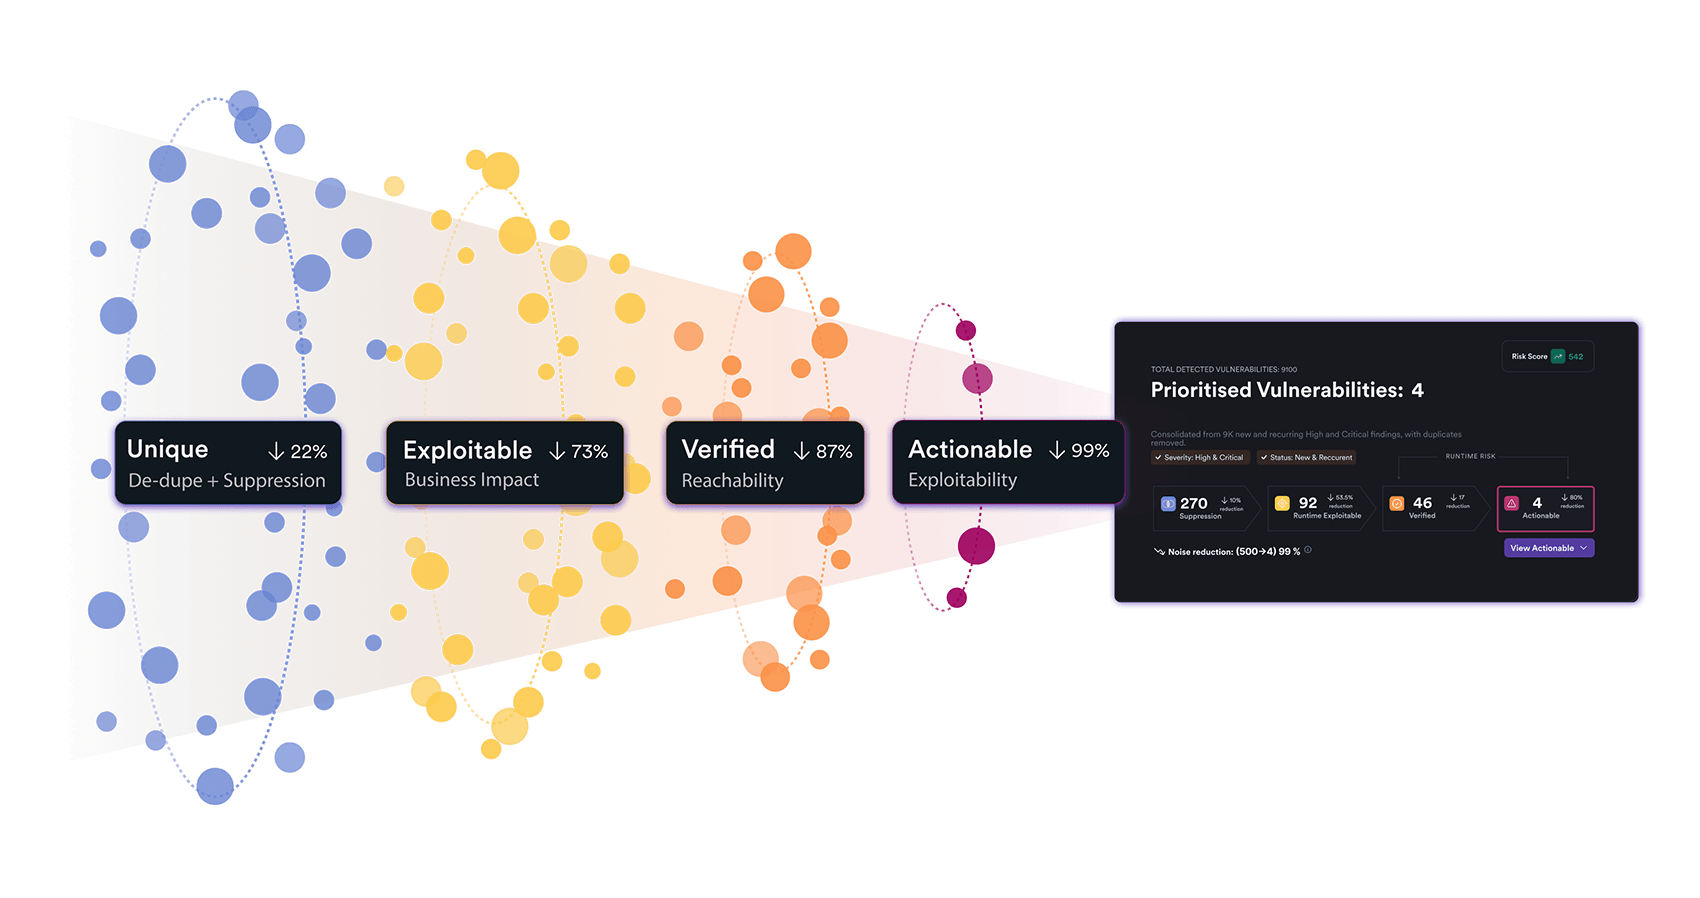
Automatically confirm exploitability for supported vulnerabilities using proof-based scanning. Spend less time investigating false alarms.

Give developers actionable findings
Provide reproducible vulnerability evidence and relevant source-code context where available, helping developers understand and investigate issues faster.

Verify that fixes work
Coordinate remediation, track vulnerability status, and use automated rescanning to confirm that supported issues have been addressed.
Get your priorities straight
Offensive security backed by proven testing expertise
Accurate findings and faster fixes, backed by independent benchmark results.
“Effortless Website Testing with Outstanding Support”
- Chris M. | System Administrator

A lot of security checks, that are easily customizable. You can make the exact scan profile/type that you want. Really good support that answering fast and giving you proper recommendations. Every time when we reported false positives - the reaction was fast and adequate. It is the best solution that you can find on a market.
Volodymyr S. | Senior Information Security Engineer
The user interface is great, making everything straightforward. The scanning engine stands out for producing high-quality results, especially when compared to competitors. It significantly reduces the manual effort and time needed to perform actions manually. I also found the initial setup to be very easy.
Zach G.
The most valuable aspect of Invicti is its ability to bridge the gap between active vulnerability scanning and dependency management. While many tools focus only on active threats, Invicti provides the SCA depth we need for enterprise portfolios.
Verified User in IT and Services
Demuestre vulnerabilidades y acelere la remediación con Invicti
See what attackers could exploit in your applications
Explore how Invicti tests applications and APIs, validates supported vulnerabilities, and helps teams prioritize fixes with greater confidence.