
Validate vulnerabilities. Prioritize real risk.
Continuously test your applications and APIs, confirm exploitable vulnerabilities with runtime evidence, and focus security efforts on the risks that matter most.

Über 5000 führende Unternehmen vertrauen auf Invicti





Severity scores are no longer enough
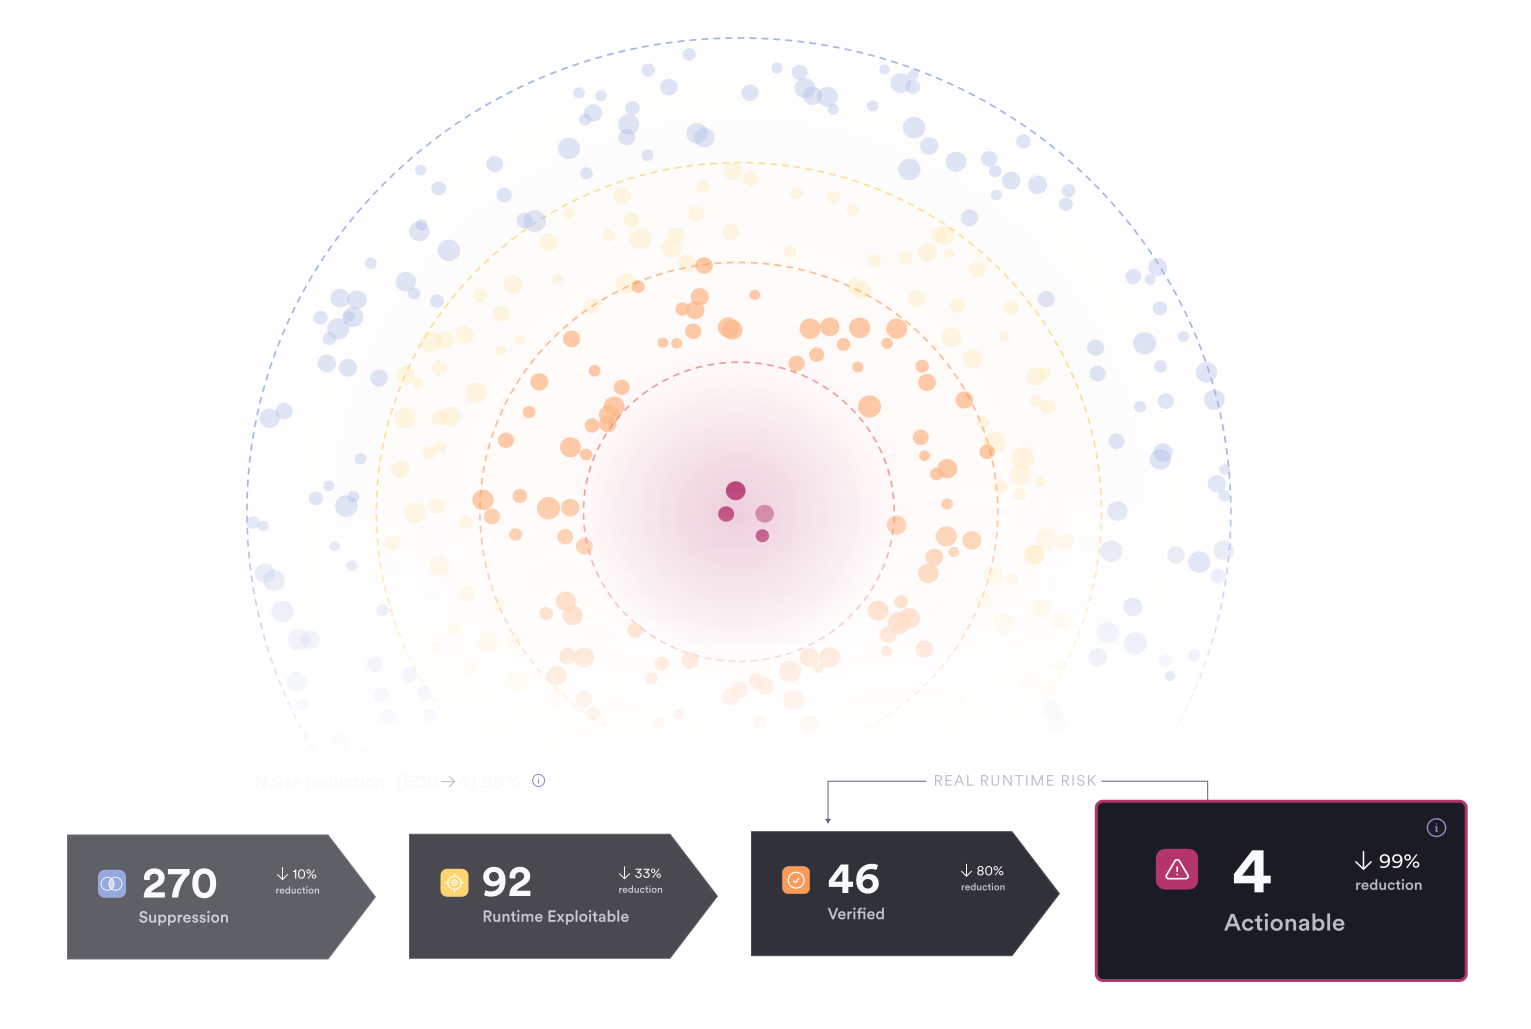
Security teams face more vulnerability findings than they can investigate. To prioritize, teams must know an issue is reachable, exploitable, and important to the business.

Too many potential threats
Large backlogs make it harder to identify the findings that need attention.

Limited proof of exploitability
Security teams spend time investigating vulnerabilities without conclusive evidence.

Unclear business impact
Technical severity alone doesn't show which exposed systems matter most.

Slow security response
Unverified findings and manual handoffs delay action on real risks.
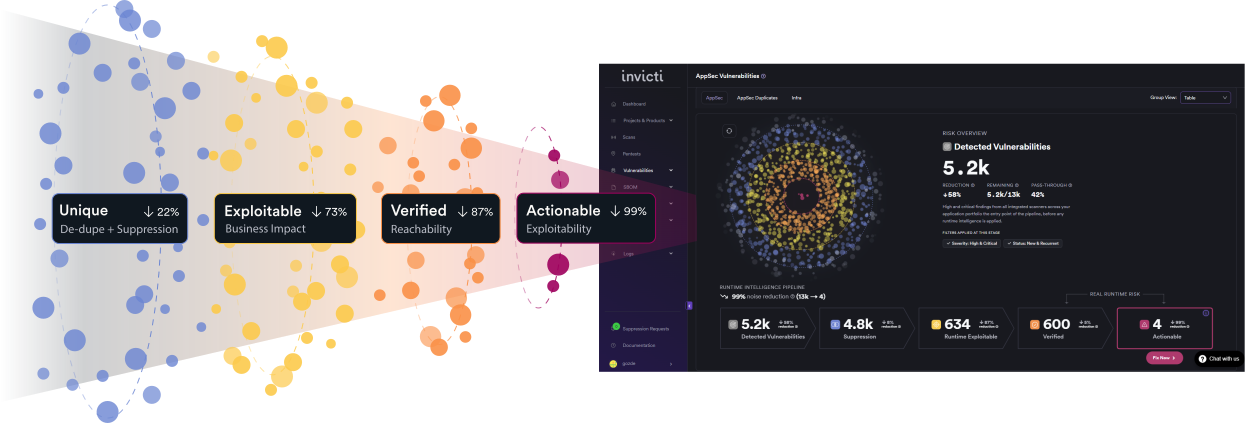
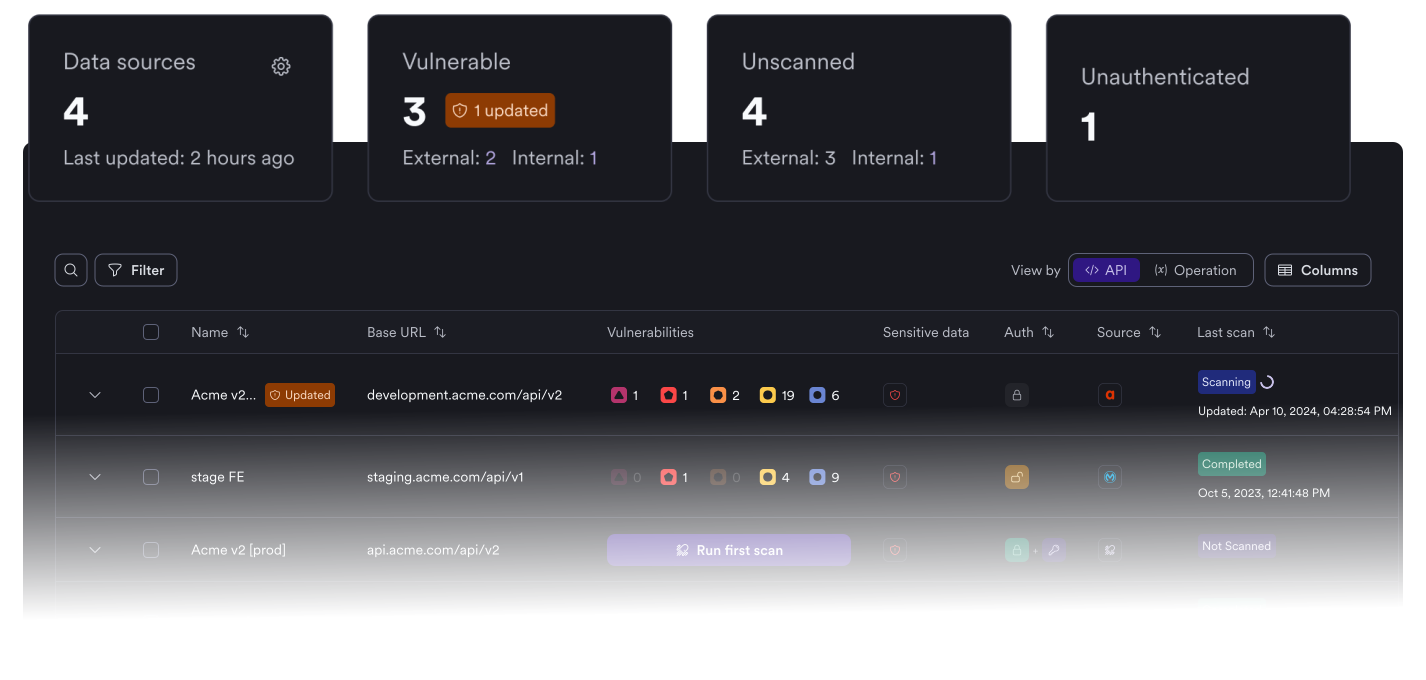
Consolidate AppSec alerts
Bring fragmented AppSec findings into one source of truth.
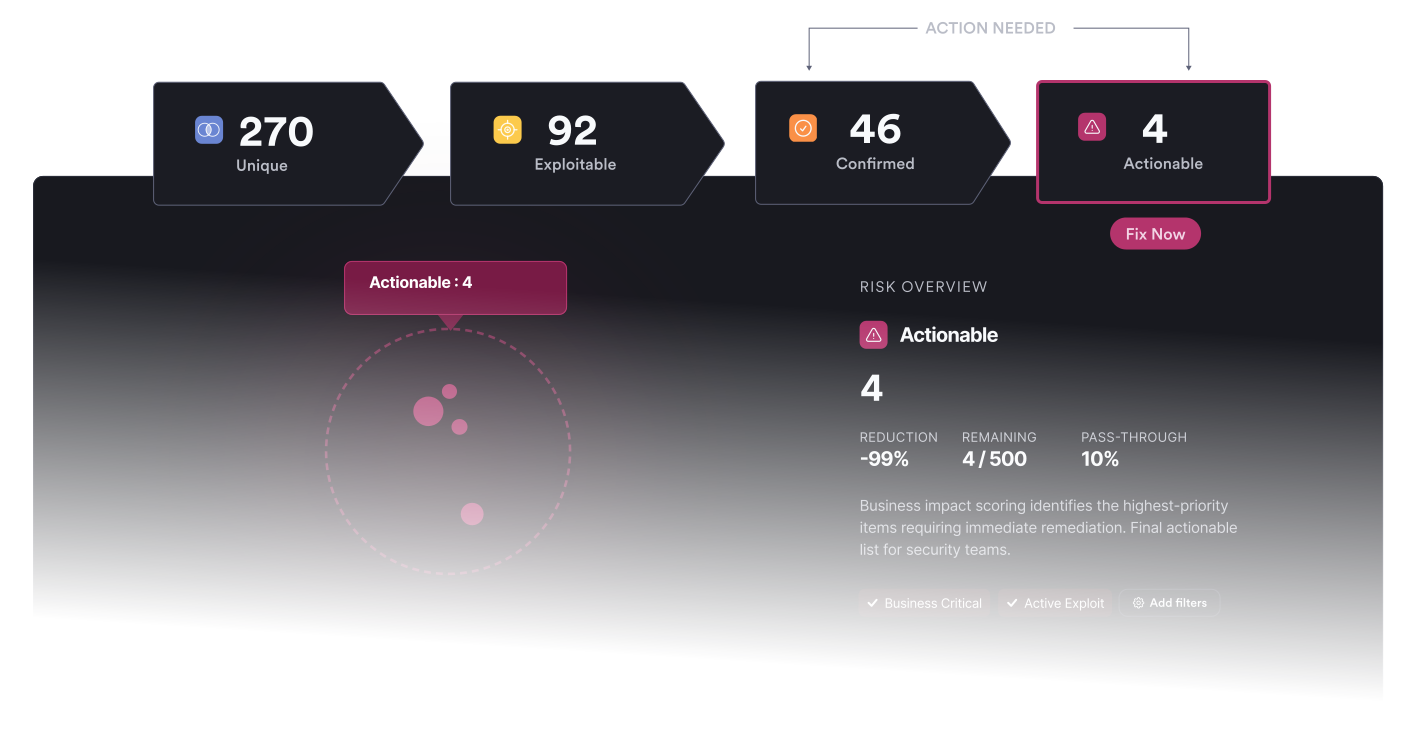
Prioritize real runtime risk
Move beyond severity scores with context about what can actually affect the business.
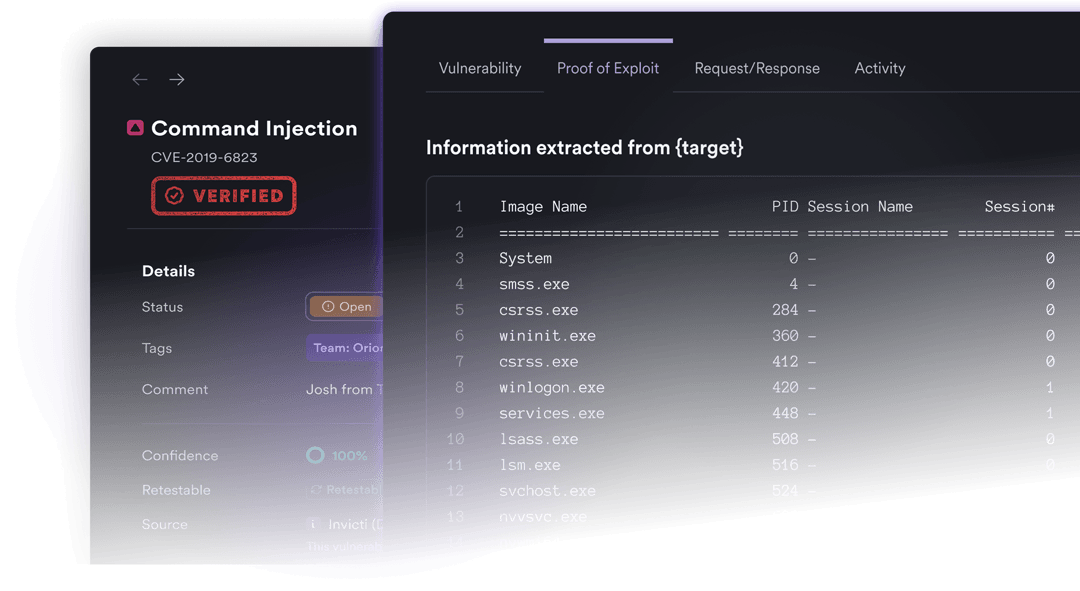
Validate what’s actually exploitable
Use outside-in runtime evidence to separate real risk from assumptions.
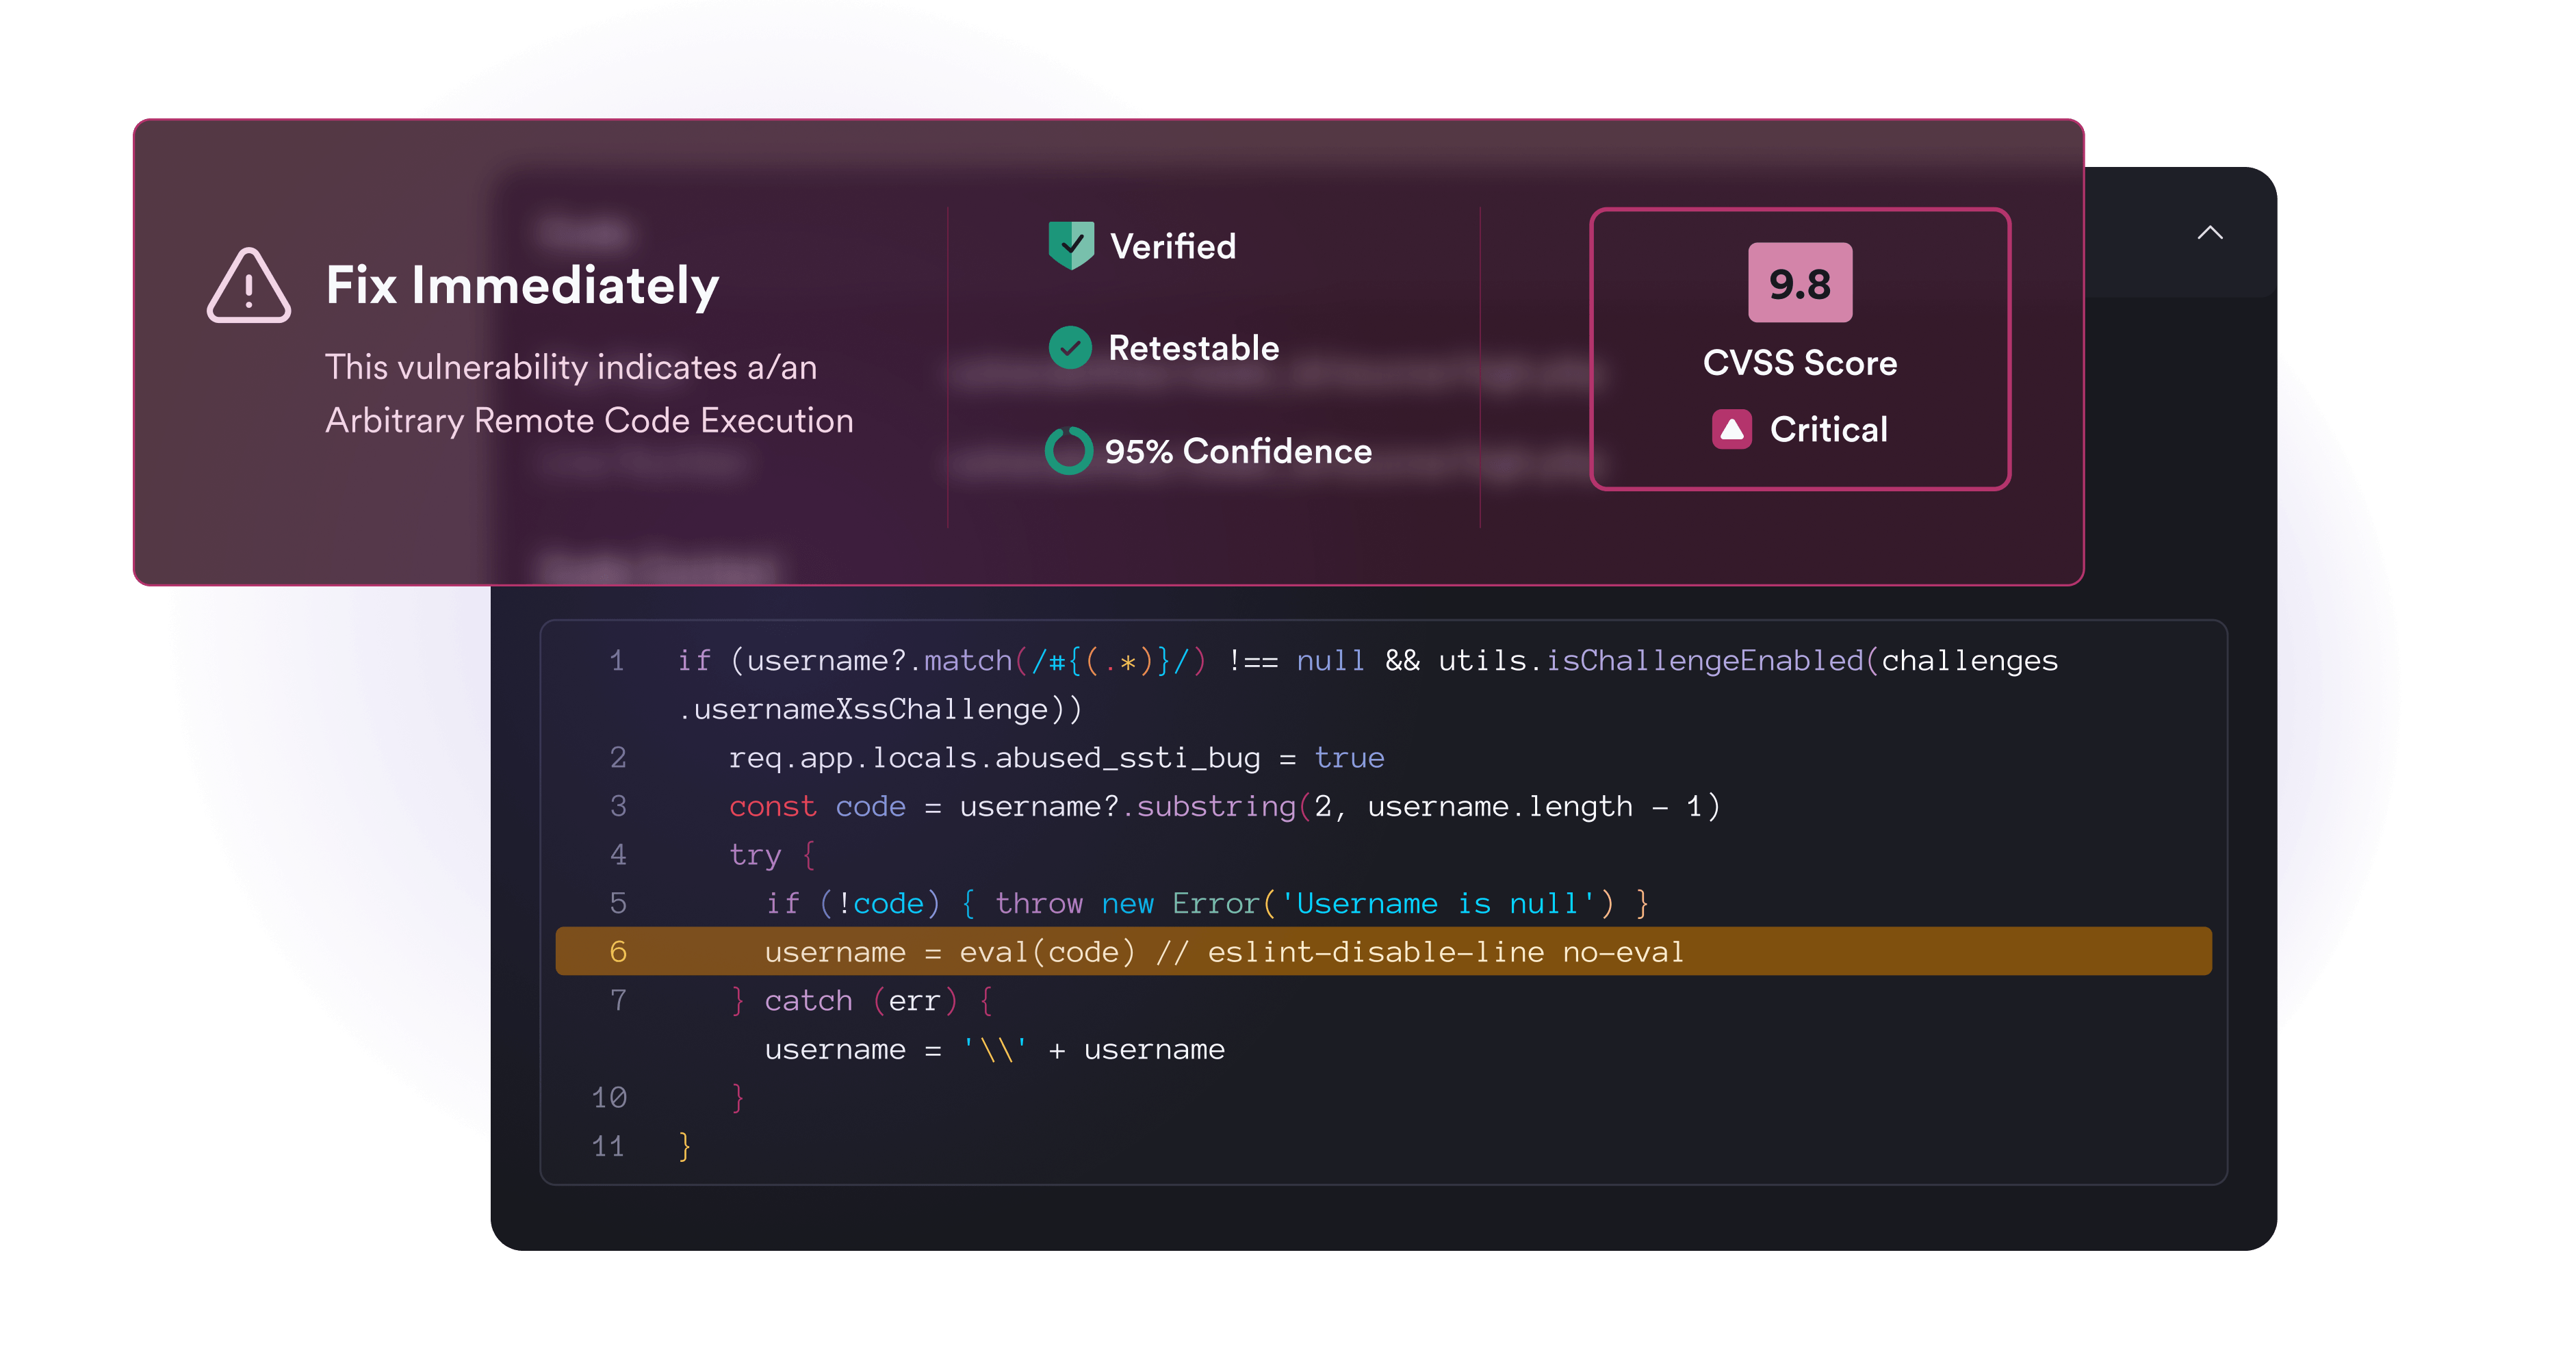
Turn priority into remediation
Get the right vulnerability to the right developer with context.
Leaders in AppSec innovation

Ready to finally clarify your priorities?
- Connect risk to exact code paths with DAST-to-SAST correlation.
- Automate handoff into developer workflows with tickets, policies, and CI/CD integrations.
- Verify the fix actually worked with retesting and runtime validation.
Frequently asked threat intelligence questions
How does Invicti determine whether a vulnerability is actually exploitable?
Invicti combines static findings with runtime context from DAST. When a SAST finding is confirmed exploitable by DAST, it can be elevated in priority; findings without supporting runtime evidence can be deprioritized. Reachability and business-impact context are then applied to generate a shorter list of real risks.
What role does reachability play in vulnerability prioritization?
Reachability helps determine whether vulnerable code or components are actually part of an executable path in the application. Invicti combines reachability with exploitability and business-impact context so teams can distinguish theoretical exposure from risk that is more likely to affect a running application.
How does DAST-to-SAST correlation improve prioritization?
Invicti overlays DAST and SAST findings onto dependency call graphs to correlate verified runtime vulnerabilities with the code paths that expose them. This allows teams to prioritize SAST findings that are tied to proven runtime risk and give developers exact code-level remediation context.
How does Invicti correlate findings across multiple AppSec scanners?
Invicti uses intelligent correlation and deduplication to merge related findings across DAST, SAST, SCA, container security, and other scanners. This prevents the same underlying issue from appearing as multiple separate alerts and creates a more unified view of application risk.
How is DAST used differently from static risk scoring?
Static analysis and contextual signals can estimate whether a vulnerability is likely to matter. DAST adds outside-in runtime evidence by testing the running application and confirming exploitability where possible. That runtime validation acts as an additional layer of proof rather than relying on severity or static context alone.
How does business context affect vulnerability priority?
Business context helps distinguish two technically similar findings that carry very different organizational risk. Application criticality, project context, exposure, sensitive data, and other business factors can be used alongside technical signals to determine which vulnerabilities should move to the top of the remediation queue.
How does Invicti turn prioritization into remediation?
Invicti connects prioritized findings to developer workflows by mapping findings to vulnerable code locations, providing context-aware guidance, and integrating with source repositories and issue-tracking workflows. The goal is to move directly from prioritized risk to a developer-ready fix.
Trace risk to the source
Prioritize better with Invicti
