The future of AppSec isn't more tools. It's better outcomes.
Latio's 2026 Application Security Market Report reveals why the best security programs have stopped optimizing for findings volume, and what they're doing instead.

Über 5000 führende Unternehmen vertrauen auf Invicti





Research Overview
A Market in Transition
Application security is changing rapidly. The report explores how teams are adapting to AI-generated code, API-first architectures, expanding attack surfaces, and growing pressure to secure software without slowing development.
Understanding the Modern AppSec Stack
Latio provides a detailed breakdown of the major AppSec categories—including SAST, DAST, API security, supply chain security, runtime technologies, vulnerability management, and ASPM—explaining how each category has evolved, where it fits today, and where the market is heading next.
Inside the Minds of AppSec Buyers
Drawing on practitioner survey data, the report reveals how security teams evaluate tools, organize responsibilities, prioritize investments, and prepare for emerging challenges. Readers gain insight into the technologies, workflows, and capabilities shaping purchasing decisions across the industry.
Emerging Technologies and Market Trends
Beyond traditional testing approaches, the report examines the impact of AI on application security, the growing importance of APIs, the evolution of runtime security, and the shift from standalone scanners toward broader platform-based approaches.
Practical Guidance for Security Leaders
Part market analysis and part buyer's guide, the report helps security leaders understand which capabilities matter most, which trends are gaining momentum, and how to evaluate application security solutions in an increasingly crowded and rapidly changing market.
Key Findings
Future-Proof AppSec for the AI Era
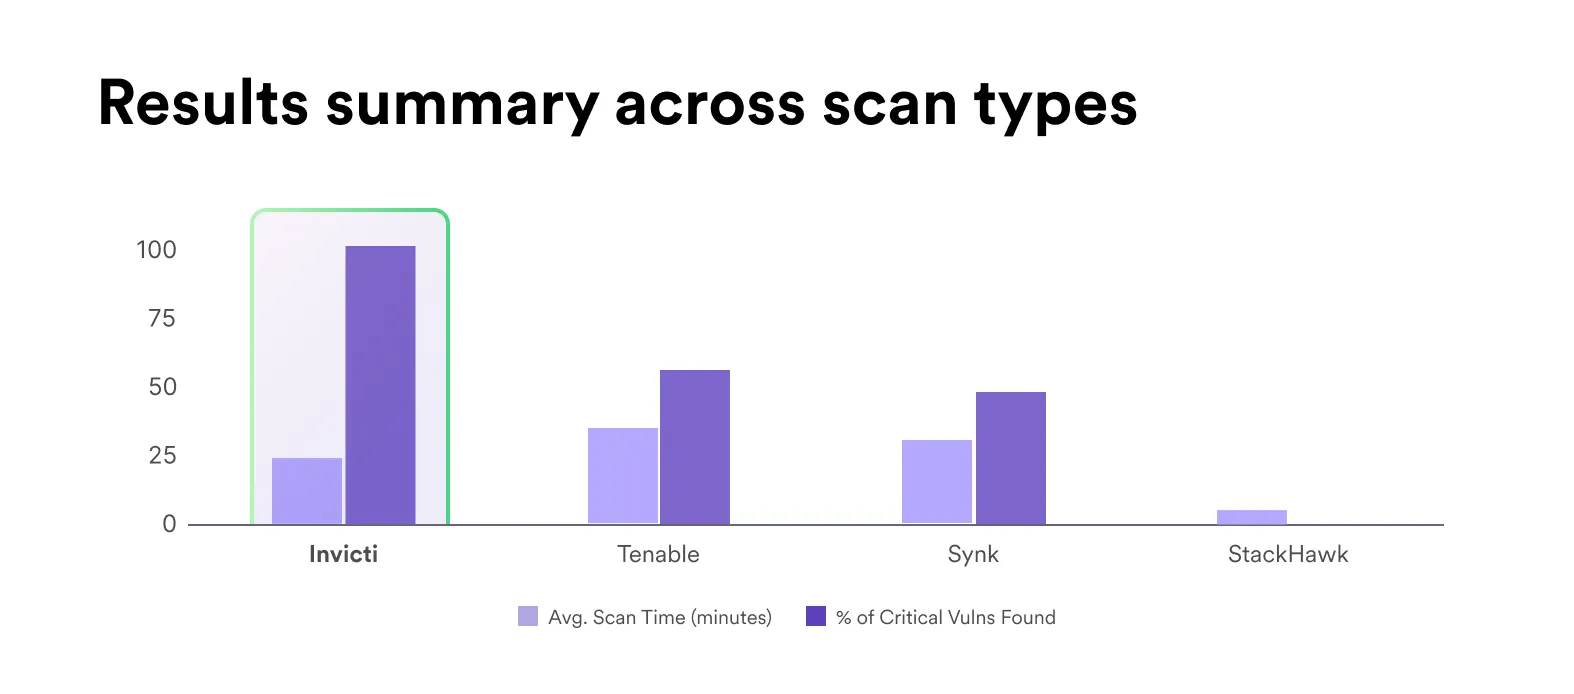
Latio's 2026 report highlights a shift toward platforms that reduce noise, improve developer experience, and focus teams on real risk. Invicti is built for exactly that.
One Platform Based on Proof
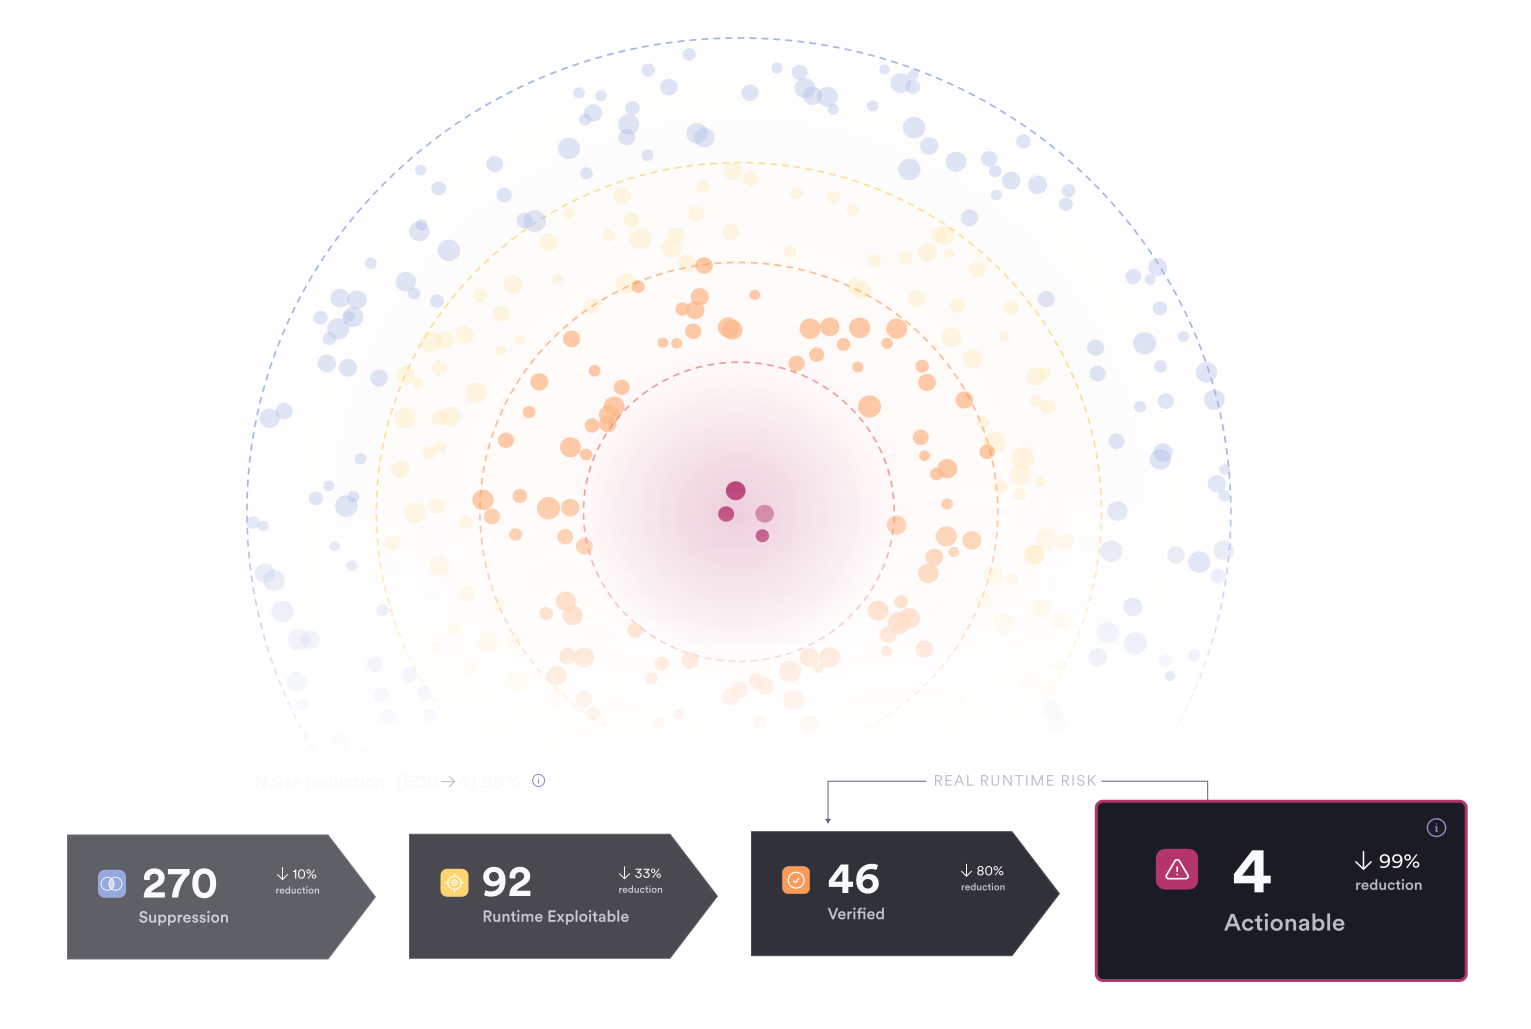
The future of AppSec isn't more scanners. It's understanding what's exploitable.
Industry-Best API Testing
Modern applications run on APIs. Security platforms must discover, inventory, and test them without false positives.
Ready for AI-Powered Apps
As organizations adopt AI-powered applications, security teams need visibility into LLMs, AI integrations, and emerging AI-specific attack vectors.
What Customers Say

„Für weitere Websites müssen wir für Sicherheitstests nun nicht mehr auf externe Anbieter zurückgreifen. Wir können Invicti starten, die Tests so oft durchführen, wie wir möchten, die Scan-Ergebnisse einsehen und die Behebung nach Belieben vornehmen. Infolgedessen sank das Budget, das wir jährlich für Penetrationstests ausgegeben haben, fast sofort um etwa 60 % und ging im Folgejahr sogar noch weiter auf etwa 20 % unserer ursprünglichen Ausgaben zurück.“
- Brian Brackenborough | Chief Information Security Officer



„Invicti ist der beste Web Application Security Scanner im Hinblick auf das Preis-Leistungs-Verhältnis. Es ist eine sehr stabile Software, schneller als das Tool, das wir zuvor verwendet haben, und weitgehend frei von False Positives – genau das, wonach wir gesucht haben.“
- Harald Nandke | Principal Consultant, Unify (jetzt Mitel)